SOC 2 compliance software is a platform that collects audit evidence and monitors your security controls, so you can pass a SOC 2 audit faster.
The main SOC 2 compliance vendors in 2026 are UprootSecurity, Vanta, Drata, Secureframe, Sprinto, Scrut, Scytale, and Thoropass, plus enterprise and consulting options. We make UprootSecurity, so we list it first, and every vendor below gets the same honest pros and cons.
Reviewed by Riya Ann Varghese, GRC Engineer, ISO 27001 lead auditor certified. Last updated October 22, 2026.
How We Compared These Vendors
We used public price data, not guesses. Starting prices come from each vendor's AWS Marketplace listing, typical prices come from Vendr's buyer data, and a few come from quotes our team has seen. Every figure comes from these sources and is dated. We also read each vendor's own product pages and our full reviews of seven of them. A GRC engineer checked every section.
What Is SOC 2 Compliance Software?
SOC 2 compliance software connects to your cloud, identity, HR, and code tools, checks your controls, and stores the evidence an auditor asks for.
Most platforms do the same core jobs:
- Evidence collection: pulls proof like MFA settings, access reviews, and backups from your tools automatically.
- Continuous monitoring: flags a control that breaks between audits, before your auditor finds it.
- Policies: ready-made security policies and tracked employee sign-offs.
- Auditor access: a read-only view so your CPA firm can test evidence in one place.
Does SOC 2 Compliance Software Include the Audit?
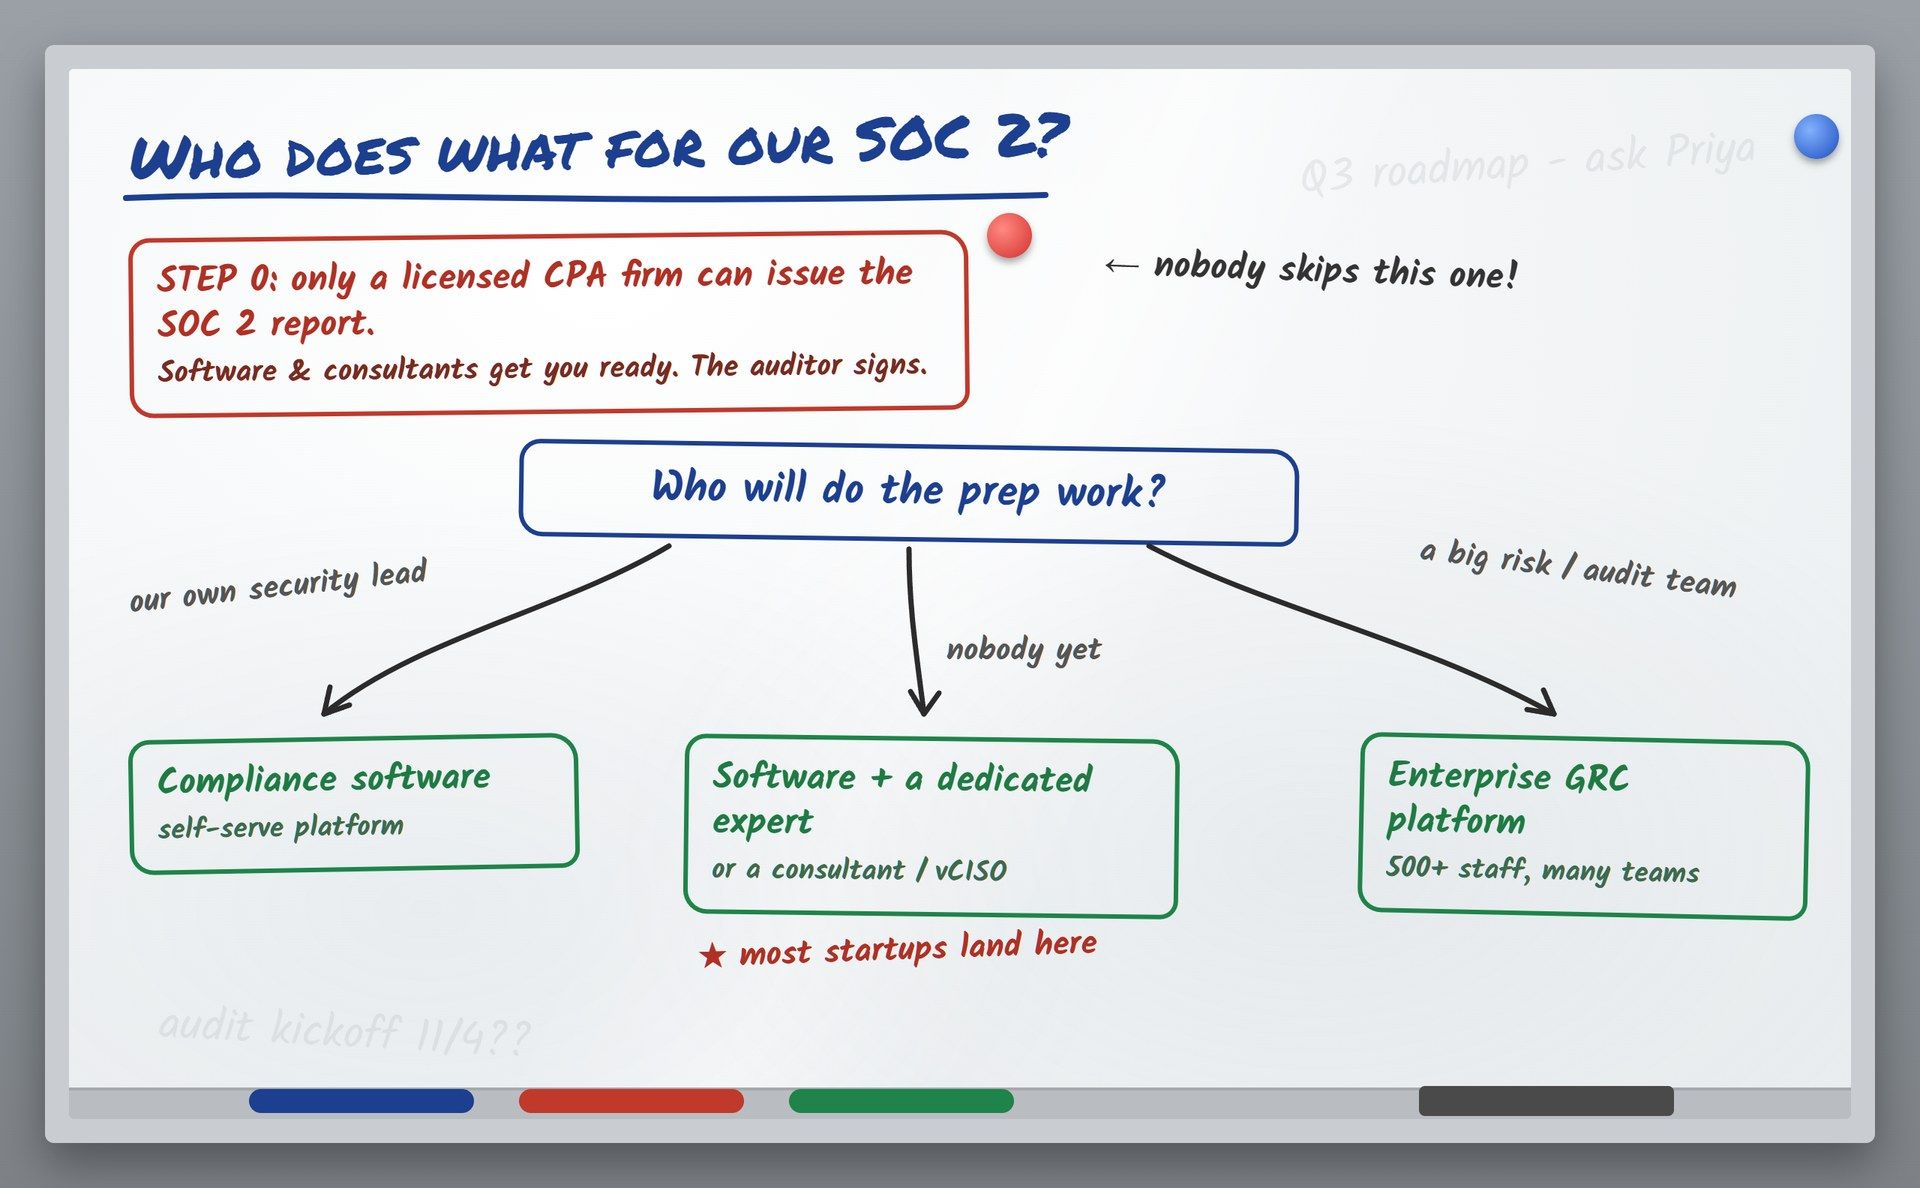
No, SOC 2 compliance software does not issue your SOC 2 report; only a licensed CPA firm can do that.
This is the most common mix-up when buying SOC 2 tools. The platform gets you ready, and an independent auditor tests your controls and signs the report. Some vendors bundle an audit into the price or own an audit firm, but the report still comes from a licensed CPA firm. Our guide to the best SOC 2 auditors covers how to pick that firm.
Which Kind of SOC 2 Provider Do You Need?
Most companies need two kinds of SOC 2 provider: one to get ready, and a CPA firm to do the audit.
| Provider type | What it does | Issues the report? | Best for |
|---|---|---|---|
| Compliance software | Automates evidence, monitoring, and policies | No | Teams with someone who already knows SOC 2 |
| Software plus a dedicated expert | Software, plus a person who guides you to the audit | No | Startups with no compliance lead |
| Consultant or vCISO | People who design and run the program for you | No | Companies that want the work done for them |
| Enterprise GRC platform | SOC 2 inside a wider risk and internal audit program | No | Companies with 500+ staff and many teams |
| CPA audit firm | Tests your controls and signs the SOC 2 report | Yes | Everyone, every year |
Best SOC 2 Compliance Software at a Glance
The best SOC 2 compliance software for most startups is a platform that includes expert help and a penetration test, because auditors and customers usually expect both.
Price, Pentest, and Audit
| Vendor | Starting price (list) | Typical yearly cost | Pentest included | Audit included |
|---|---|---|---|---|
| UprootSecurity | Custom quote | Custom quote | Yes, every plan | No, we introduce you to audit firms |
| Vanta | $14,000 | About $20,000 | No | No, bring your own auditor |
| Drata | $32,500 for SOC 2 | Not published | No | No |
| Secureframe | $15,000 | About $20,000 | No | No, audit support only |
| Sprinto | $9,500 for SOC 2 | About $15,000 | No | No, partner auditors |
| Scrut | $15,000 (up to 20 staff) | From about $4,000 in quotes we have seen | Yes, in quotes we have seen | Can be bundled in the quote |
| Scytale | $7,500 | Higher with add-ons | Add-on ($4,500) | Add-on |
| Thoropass | Not published | About $26,900 | Offered | Yes, its own CPA firm |
| Optro (formerly AuditBoard) | Custom | Custom | No | No |
| Fractional CISO | By company size | By company size | No | No, refers you to auditors |
How we count prices: some lists show Vanta, Drata, and Secureframe "from $7,500". Those figures are often a single line in a marketplace listing, such as one framework fee. The starting prices above are what SOC 2 itself costs on each vendor's AWS Marketplace listing.
The 10 Best SOC 2 Compliance Vendors
1. UprootSecurity
UprootSecurity is a compliance platform that pairs automated evidence collection with a dedicated compliance expert and a yearly penetration test in every plan.
- What you get: continuous monitoring across 140+ integrations, ready-made policies, a trust center, security questionnaire automation, and support for 22 frameworks, including SOC 2, ISO 27001, and HIPAA.
- Pentest: one web application on Starter, two targets on Growth, and three on Enterprise.
- Price: a custom quote based on your scope, with a 14-day free trial.
- Pros: an expert from gap assessment to final report, and a pentest without a second vendor.
- Cons: fewer integrations than Vanta, and only a handful of public G2 reviews so far.
- Best for: startups and scaleups that want SOC 2 done with expert help, not just software.
Reviewers on G2 score UprootSecurity 5.0 out of 5, but across only 2 reviews so far, so the score says little yet.
2. Vanta
Vanta is the most widely known SOC 2 compliance platform, with 400+ integrations and hourly automated tests.
- Price: list price starts at $14,000 a year for 1 to 20 employees, and Vendr's median contract is about $20,000.
- Pros: easy to use, a large integration library, and a well-known name with buyers.
- Cons: the audit and a pentest cost extra, and costs grow with each framework and add-on.
- Best for: growing software companies with someone in-house to drive the work. Read our full Vanta review.
Reviewers on G2 score it 4.5 out of 5 across 2,858 reviews, praising its ease of use and automation, while price and integration gaps draw the most complaints.
3. Drata
Drata is a compliance automation platform with 200+ integrations and shared controls across 20+ frameworks.
- Price: a $25,000 yearly platform fee plus $7,500 per framework, so $32,500 for SOC 2 at list price.
- Pros: deep automation and strong multi-framework mapping.
- Cons: priced for larger companies, and the audit and pentest are extra.
- Best for: companies with 500+ employees and their own security team. See our Drata review.
Drata scores 4.7 out of 5 across 1,410 combined G2 and PeerSpot ratings on its AWS Marketplace listing, with reviewers rating its support and ease of use highly.
4. Secureframe
Secureframe is a compliance platform that assigns every customer a dedicated compliance expert who is a former auditor, according to its AWS Marketplace listing.
- Price: $15,000 list for SOC 2 and up to 100 employees, with a typical contract of about $20,000.
- Pros: expert help, 300+ integrations, and 30+ frameworks, including CMMC.
- Cons: no pentest in the list price, and integration issues are the top G2 complaint.
- Best for: teams that want software plus an ex-auditor's guidance. Read the Secureframe review.
Reviewers on G2 score it 4.7 out of 5 across 831 reviews, 699 of them five stars, with integration issues as the most common complaint.
5. Sprinto
Sprinto is a lower-cost SOC 2 compliance platform with 300+ integrations and 25+ frameworks.
- Price: $9,500 a year for SOC 2 at list price, and a Vendr median of about $15,000.
- Pros: affordable, with a guided path for first-time teams.
- Cons: the audit and a pentest are separate purchases, and some reviews mention slow responses.
- Best for: cost-conscious startups. See our Sprinto review.
Sprinto scores 4.7 out of 5 across 1,690 combined G2 and PeerSpot ratings on its AWS Marketplace listing, though recent G2 reviews are mixed on response times.
6. Scrut Automation
Scrut is a compliance platform that can bundle the SOC 2 audit and a penetration test into one quote.
- Price: from about $4,000 a year including the audit and a pentest, in quotes we have seen, against a $15,000 AWS list price for up to 20 employees.
- Pros: low starting price, many frameworks, and hands-on support.
- Cons: its own pages list different framework and integration counts, so confirm them in a demo.
- Best for: startups that need several frameworks on a budget. Read our Scrut review.
Reviewers on G2 score it 4.9 out of 5 across 1,332 reviews, the highest score of any vendor on this list.
7. Scytale
Scytale is a compliance platform sold with optional expert consulting packages.
- Price: $7,500 a year for the platform and one framework; consulting starts at $4,000 and a pentest at $4,500.
- Pros: a low entry price and well-rated expert support.
- Cons: the total grows as you add consulting, pentesting, and the audit.
- Best for: startups that want to pick only the help they need. See the Scytale review.
Scytale shows 4.7 out of 5 from 773 G2 ratings on its AWS Marketplace listing, with reviewers mostly praising its hands-on support team and integrations drawing the most complaints.
8. Thoropass
Thoropass is a compliance platform with its own licensed CPA firm, Thoropass Assurance, so software and audit come from one company.
- Price: Vendr's median is about $26,900 a year (February 2026), and Thoropass does not publish prices.
- Pros: one contract for software, audit, and penetration testing.
- Cons: some buyers prefer an auditor that is independent from their software vendor, and prices are not published.
- Best for: teams that want software and the audit from one provider.
Reviewers on G2 score Thoropass 4.7 out of 5 across 586 reviews, praising its ease of use and customer support, while unclear guidance and integration issues draw the most complaints.
9. Optro (formerly AuditBoard)
Optro is an enterprise GRC platform that runs SOC 2 inside a wider risk, internal audit, and regulatory program. AuditBoard renamed itself Optro in March 2026.
- Price: custom enterprise pricing.
- Pros: one system for many departments and frameworks.
- Cons: far more than most startups need, with longer setup.
- Best for: large, regulated companies with internal audit teams.
Reviewers on G2 score Optro 4.6 out of 5 across 1,639 reviews, praising its ease of use and audit management, while limited functionality and customization draw the most complaints.
10. Fractional CISO
Fractional CISO is a virtual CISO service that runs your SOC 2 program for you instead of selling software.
- Price: based on company size, scope, and IT complexity.
- Pros: a credentialed CISO and analyst do the work, and it works with any platform.
- Cons: no platform included, and it costs more than software alone.
- Best for: companies with no security lead that want the program run for them.
How UprootSecurity Helps You Get SOC 2 Done
UprootSecurity combines the software, the expert, and the penetration test that most SOC 2 programs need, in one quote.
- A dedicated compliance expert from gap assessment to the final report.
- A yearly penetration test in every plan, so you do not buy one separately.
- Continuous monitoring across 140+ integrations to keep evidence current between audits.
→ See how it works: book a demo
How Much Does SOC 2 Compliance Software Cost?
SOC 2 compliance software typically costs $7,500 to $32,500 a year at list price, and Vendr's median contracts run from about $15,000 to $27,000.
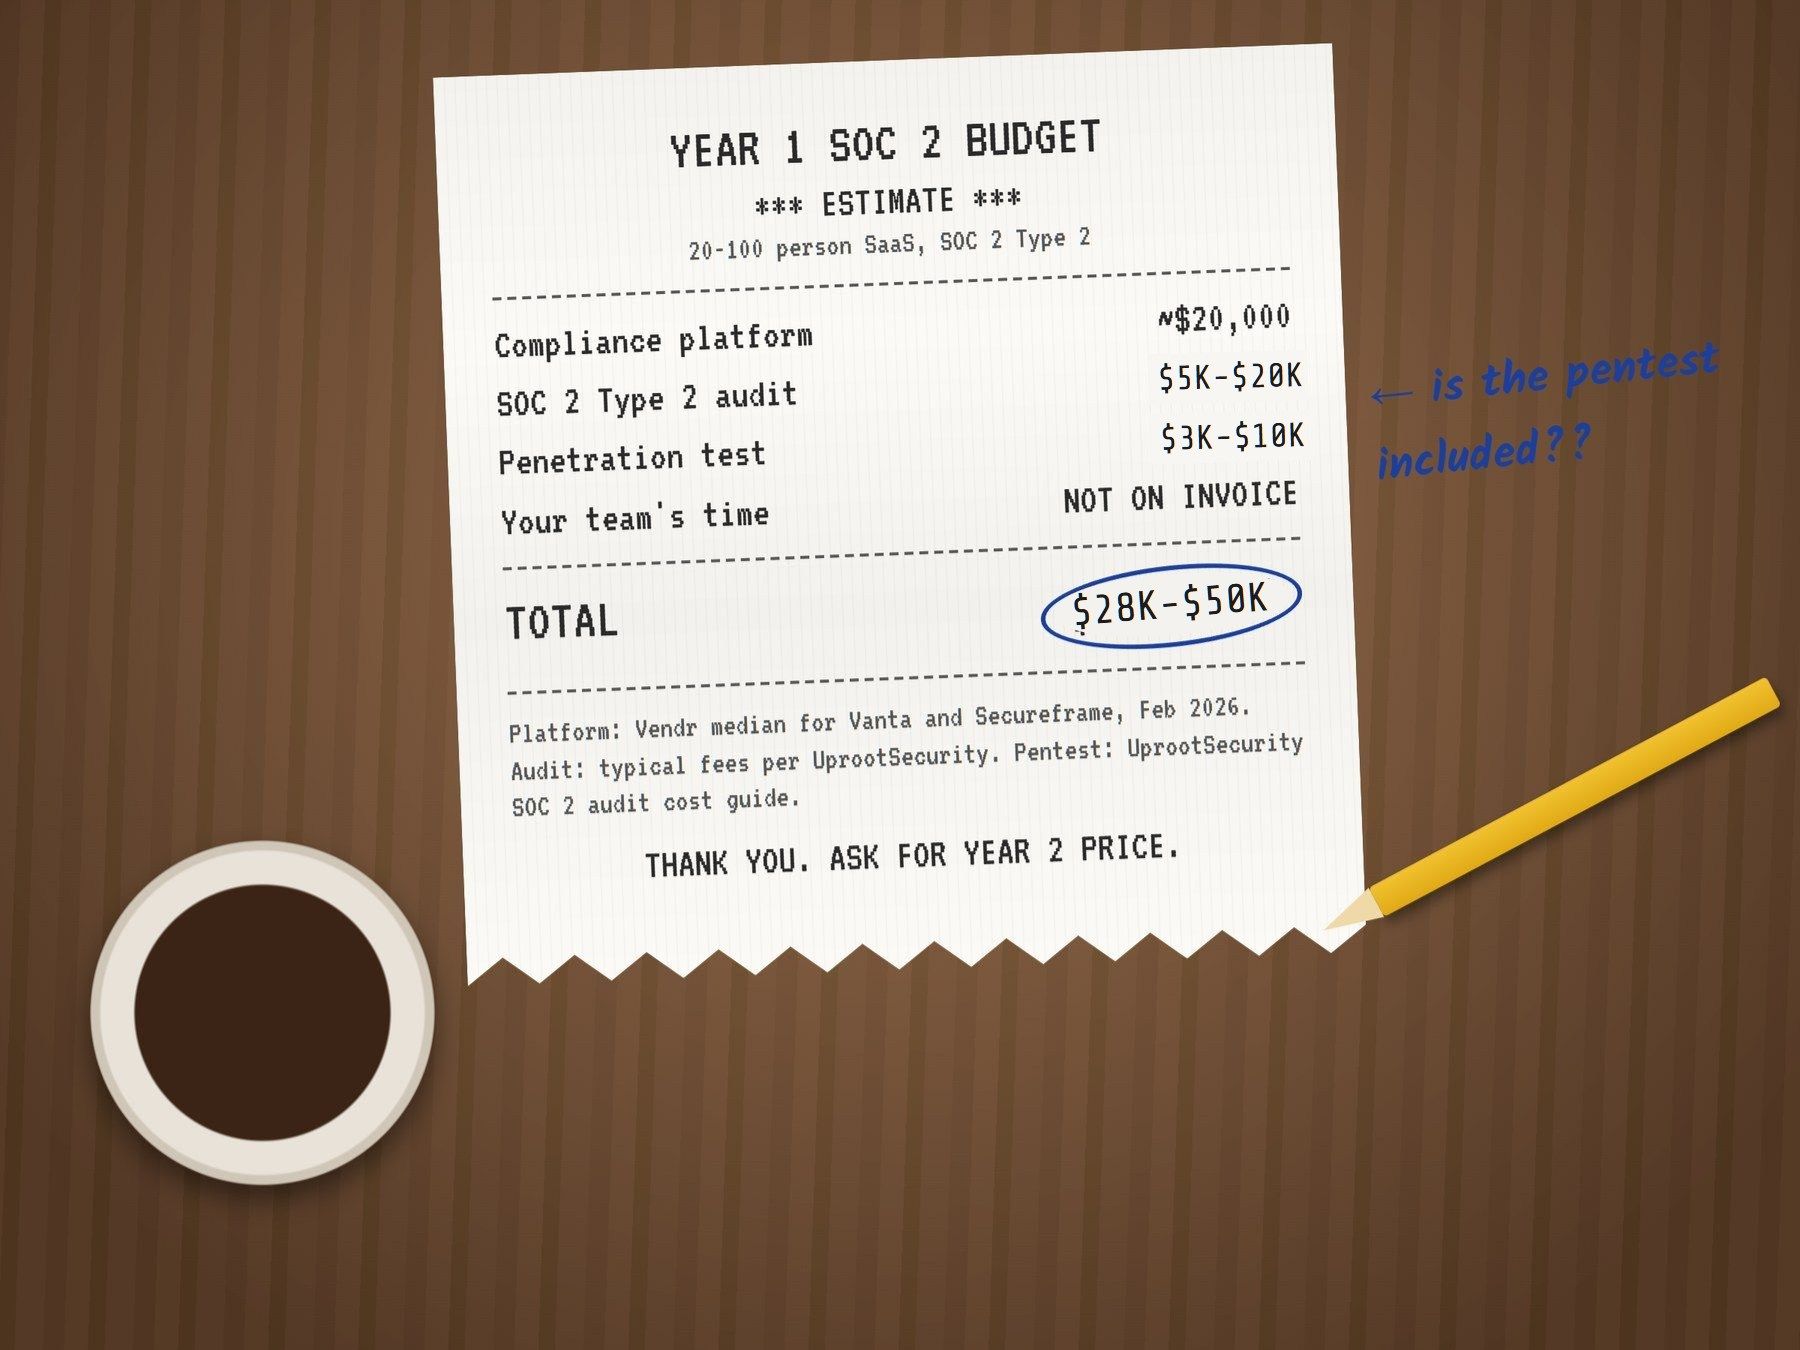
The software is only part of the bill. For a 20 to 100 person SaaS company getting a first SOC 2 Type 2 report, a realistic first-year budget looks like this:
| Cost | Typical amount | Source |
|---|---|---|
| Compliance platform | About $20,000 | Vendr median for Vanta and Secureframe |
| SOC 2 Type 2 audit | $5,000 to $20,000 | Our SOC 2 audit cost guide |
| Penetration test | $3,000 to $10,000 | Our SOC 2 audit cost guide |
| Your team's time | Not on any invoice | Engineering and leadership hours |
| Total | About $28,000 to $50,000 | Estimate |
This is an estimate. Bundles change the math: a platform that includes the pentest or the audit removes a line from this table. Our guide to SOC 2 audit costs breaks the audit fee down by company size.
How to Choose SOC 2 Compliance Software
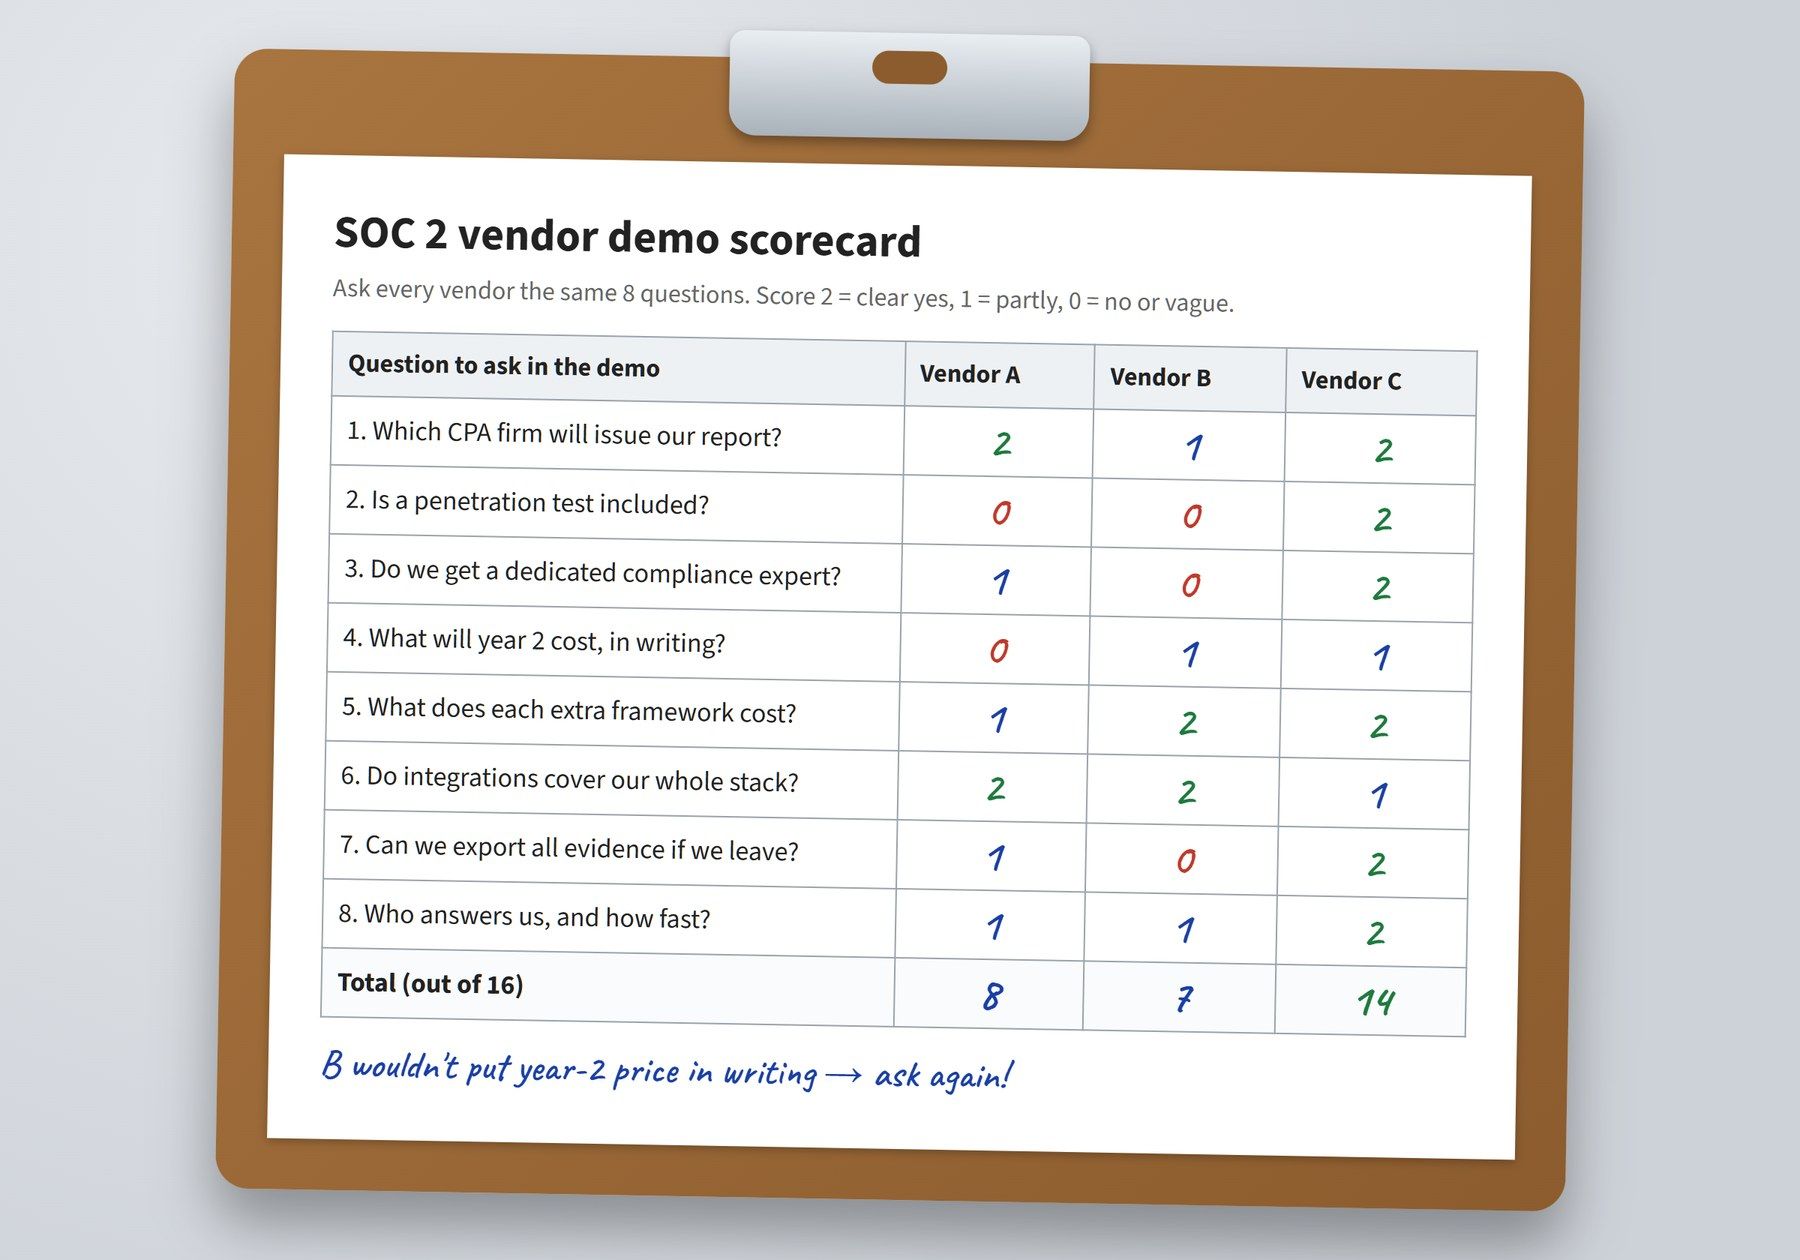
To choose SOC 2 compliance software, compare the full first-year cost and ask all SOC 2 vendors the same questions in the demo.
- Which CPA firm will issue our report? Get a name, and check the firm is licensed.
- Is a penetration test included? Most customers and auditors expect one.
- Do we get a dedicated compliance expert? Ask how many other clients that person supports.
- What will year 2 cost, in writing? Renewal increases are a common complaint.
- What does each extra framework cost? ISO 27001 or HIPAA often comes next.
- Do the integrations cover our whole stack? Check your cloud, identity, HR, and code tools.
- Can we export all our evidence if we leave? Avoid getting locked in.
- Who answers our questions, and how fast? Response time matters most during the audit.
Can a Self-Serve Tool Get You SOC 2 Ready Without a Consultant?
A self-serve SOC 2 tool can get you ready without a consultant if someone on your team already understands security controls and audits.
Without that person, teams often stall on scoping, policies, and auditor questions. That is why many startups choose a platform that includes a dedicated expert.
5 Mistakes to Avoid When Buying SOC 2 Software
The most common SOC 2 software mistake is buying a platform before deciding what your audit needs to cover.
- Buying before scoping. Decide which trust services criteria your customers need first. Changing scope halfway through costs weeks.
- Finding an auditor last. CPA firms book up months ahead, so talk to auditors while you prepare, not after.
- Rebuilding evidence at the end. A Type 2 audit tests the whole observation period, so evidence must be collected from day one.
- Treating Type 1 as the finish line. Larger customers usually ask for a Type 2 report next, so choose software that can carry you through it.
- Leaving AI tools out of scope. If staff put customer data into AI tools, those tools belong in your risk assessment and vendor reviews.
How Long Does SOC 2 Take With Compliance Software?
SOC 2 with compliance software usually takes a few months for a Type 1 report and about 5 to 15 months for a first Type 2 report.
| Phase | Typical time | What happens |
|---|---|---|
| Scope and connect | 1 to 2 weeks | Pick your criteria, connect cloud, identity, HR, and code tools |
| Fix gaps | 3 to 8 weeks | Write policies, fix failing controls, run staff training |
| Type 1 audit | A few weeks | Auditor checks control design on a single date |
| Type 2 observation period | 3 to 12 months | Controls run while the software keeps collecting evidence |
| Type 2 audit and report | A few weeks | Auditor tests the period and issues the report |
These are typical ranges, not promises. Software speeds up evidence collection, but it cannot shorten the observation period. Our guide to the SOC 2 Type 2 report explains that period in detail.
Best SOC 2 Compliance Software by Company Type
| Company type | What matters most | Good fit |
|---|---|---|
| Early-stage startup, first SOC 2 | Expert help and a low total cost | UprootSecurity, Scrut, Scytale, Sprinto |
| HR and payroll software | Privacy controls, since you hold employee data | A platform covering SOC 2 plus GDPR or privacy frameworks |
| Health tech | SOC 2 and HIPAA together | UprootSecurity, Vanta, Secureframe |
| Defense suppliers | CMMC alongside SOC 2 | Secureframe, Vanta |
| Enterprise, 500+ staff | Many frameworks and departments | Drata, Optro |
| No security lead at all | Someone to run the program | UprootSecurity, Fractional CISO |
Not sure which criteria your scope needs? Our guide to the SOC 2 trust services criteria explains which ones to include, and our Vanta alternatives guide compares more options.
How UprootSecurity Approaches Compliance
Picking SOC 2 compliance software is the first decision. Getting a clean report, and keeping it every year, is the work that follows.
| What your SOC 2 needs | How UprootSecurity handles it |
|---|---|
| Someone who knows SOC 2 | A dedicated compliance expert from gap assessment to the final report |
| Evidence that stays current | Continuous monitoring across 140+ integrations |
| Real security testing | A yearly penetration test in every plan |
| More than one framework | SOC 2, ISO 27001, HIPAA, and 22 frameworks in total |
| Proof for customers | A trust center and security questionnaire automation |
| A clear price | A custom quote based on your scope, plus a 14-day free trial |
UprootSecurity is a compliance platform for startups and scaleups that need SOC 2, ISO 27001, HIPAA, or other frameworks. See our SOC 2 framework page and plans.
Frequently Asked Questions
The best SOC 2 compliance software depends on how much help your team needs. Vanta and Drata suit teams with in-house security staff. UprootSecurity, Secureframe, and Scytale add expert help, and UprootSecurity also includes a penetration test in every plan. Compare the full first-year cost, not just the platform fee.
SOC 2 compliance software is a platform that connects to your cloud, identity, HR, and code tools to collect audit evidence and monitor security controls. It also manages policies and gives your auditor a place to review evidence. It prepares you for the audit but does not issue the SOC 2 report.
SOC 2 compliance software typically costs $7,500 to $32,500 a year at list price, and Vendr's median contracts run from about $15,000 to $27,000. The audit and a penetration test usually cost extra, so a first-year SOC 2 Type 2 budget for a small SaaS company often lands between $28,000 and $45,000.
No, SOC 2 compliance software does not perform the audit or issue the report. Only a licensed CPA firm can do that. Some vendors bundle an audit into the price or own an audit firm, like Thoropass, but the report still comes from an independent, licensed CPA firm.
Scrut has the lowest price we have seen, from about $4,000 a year including the audit and a penetration test, in quotes our team has seen. Scytale lists $7,500 a year for its platform, and Sprinto lists $9,500 for SOC 2. Always compare the full cost, including the audit and pentest.
UprootSecurity includes a yearly penetration test in every plan. Scrut has included one in quotes we have seen, and Thoropass offers pentesting as a service. Vanta, Drata, Secureframe, and Sprinto do not include a pentest in their list prices, and Scytale sells one as an add-on.
Vanta is usually better for smaller growing teams, with a $14,000 starting list price and 400+ integrations. Drata suits larger companies with several frameworks, at $32,500 a year for SOC 2 at list price. Neither includes the audit or a penetration test, so add those to your budget.
Yes, a self-serve compliance tool can get you SOC 2 ready if someone on your team understands security controls and audits. Teams without that person often get stuck on scoping, policies, and auditor questions, so many startups choose a platform that includes a dedicated compliance expert.
A SOC 2 Type 1 report can take a few weeks to a few months once your controls are in place. A SOC 2 Type 2 report needs an observation period of 3 to 12 months, plus audit fieldwork. Software speeds up evidence collection but cannot shorten the observation period.
Yes, most SOC 2 compliance software also supports ISO 27001 and HIPAA by mapping shared controls across frameworks. Check what each extra framework costs, because some vendors charge per framework. UprootSecurity supports 22 frameworks, and Drata, for example, charges $7,500 for each framework at list price.