A security questionnaire is a list of questions a customer sends to check how your company protects their data before they buy.
For B2B software companies, these questionnaires arrive in almost every enterprise deal, and a slow or sloppy answer can stall the sale. This guide shows what a security questionnaire asks, the common types, and how to answer one fast and accurately, with example answers and the evidence to attach.
Reviewed by Riya Ann Varghese, GRC Engineer, ISO 27001 lead auditor certified. Last updated: November 10, 2026.
What Is a Security Questionnaire?
A security questionnaire is a buyer's due diligence check on a vendor's security, sent as a spreadsheet, a portal or a standard form.
The buyer's security or procurement team sends it, which is why it is also called a vendor security questionnaire, and the vendor's team fills it in. If you sell software, you are the vendor. Questionnaires range from 20 quick questions to several hundred, and they usually come with a request for evidence such as a SOC 2 report or your policies. The buyer side of this process, choosing and scoring vendors, is covered in our third-party risk management guide.
What Does a Security Questionnaire Ask?
A security questionnaire asks how you control access, protect data, handle incidents, manage vendors and keep the service running.
| Topic | Typical question | Evidence often requested |
|---|---|---|
| Access control | Do you enforce multi-factor authentication for all staff? | Identity provider settings, access policy |
| Data protection | Is customer data encrypted at rest and in transit? | Encryption policy, architecture overview |
| Incident response | Do you have a tested incident response plan? | Incident response plan, last tabletop exercise date |
| Vendor management | How do you assess your own vendors? | Vendor list, vendor review process |
| Business continuity | Do you back up data and test restores? | Backup policy, restore test record |
| Compliance | Do you have a SOC 2 report or ISO 27001 certificate? | SOC 2 report under NDA, ISO certificate |
| Privacy | Where is personal data stored, and who can see it? | Data processing agreement, subprocessor list |
Common Types of Security Questionnaires
The most common security questionnaires are the SIG, the CAIQ, the HECVAT and custom spreadsheets that each buyer writes.
| Questionnaire | Published by | Who sends it | Cost |
|---|---|---|---|
| SIG (Standardized Information Gathering) | Shared Assessments | Banks, insurers and large enterprises running vendor risk programs | Licensed by the sender; a corporate license is listed at $7,000 a year |
| CAIQ (Consensus Assessments Initiative Questionnaire) | Cloud Security Alliance | Buyers of cloud and SaaS services; yes or no questions mapped to the Cloud Controls Matrix (current version 4.1) | Free to download |
| HECVAT | EDUCAUSE, with Internet2 and REN-ISAC | Colleges and universities buying technology (current version 4.1.6, with privacy and AI questions) | Free for institutions and their vendors |
| Custom spreadsheet or portal | The buyer | Most mid-size and enterprise buyers | Free |
Sources: Shared Assessments SIG page, Cloud Security Alliance CAIQ page and EDUCAUSE HECVAT page, checked November 2026.
If you sell to universities, keep a completed HECVAT ready. If you sell cloud software, a completed CAIQ answers many cloud-focused buyers in one go.
Security Questionnaire Examples: Weak vs Strong Answers
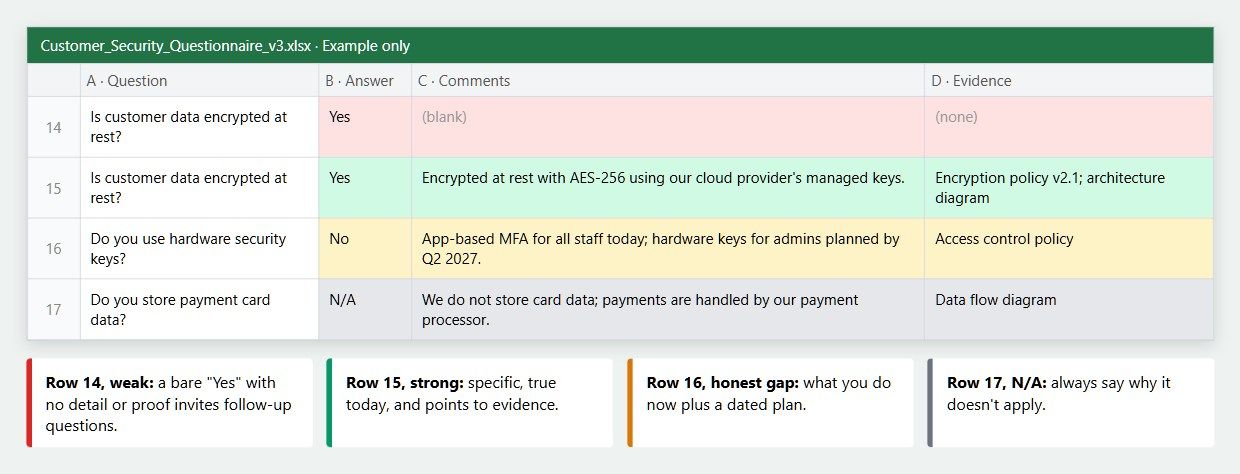
A strong security questionnaire answer is short, specific, true today, and points to evidence the buyer can check.
| Question | Weak answer | Strong answer | Evidence to attach |
|---|---|---|---|
| Do you enforce MFA for all employees? | Yes, we take security seriously. | Yes. MFA is enforced through our identity provider for all employees and contractors, including admin accounts. | Access control policy; identity provider MFA setting |
| Is customer data encrypted at rest? | Yes. | Yes. Customer data is encrypted at rest with AES-256 using our cloud provider's managed keys. | Encryption policy; architecture diagram |
| Do you have an incident response plan? | We handle incidents quickly. | Yes. Our incident response plan defines roles, severity levels and customer notification timelines, and we test it every year. | Incident response plan; date of last test |
| Do you review your own vendors? | N/A. | Yes. We review vendors that handle customer data before onboarding and every year, including their SOC 2 reports. | Vendor management policy; vendor list |
| Do you have a SOC 2 Type 2 report? | We're working on it. | Our SOC 2 Type 2 observation period runs January to June 2027. We can share our SOC 2 Type 1 report and a readiness letter now. | SOC 2 Type 1 report under NDA; auditor letter |
Only give answers that are true for your company today. The examples show the shape of a good answer, not facts about your setup.
How to Answer "No" or "N/A" Without Losing the Deal
An honest "No" with a short reason and a dated plan almost always beats a "Yes" you cannot prove.
Buyers expect some gaps. What worries them is an answer that turns out to be false, because questionnaire answers are often attached to the contract. If you answer "yes" to a control you only plan to build, you may be promising something you cannot deliver.
- For a real gap: say what you do today, what you will add, and when. For example: "We run quarterly access reviews manually today and will automate them by Q2 2027."
- For "N/A": say why it does not apply. For example: "N/A. We do not store payment card data; payments are handled by our payment processor."
- For a compensating control: explain the other control that covers the risk.
Too many questionnaires, too little time? Talk to a compliance expert about building an answer library and trust center that answers most of them for you.
How to Build a Security Questionnaire Answer Library
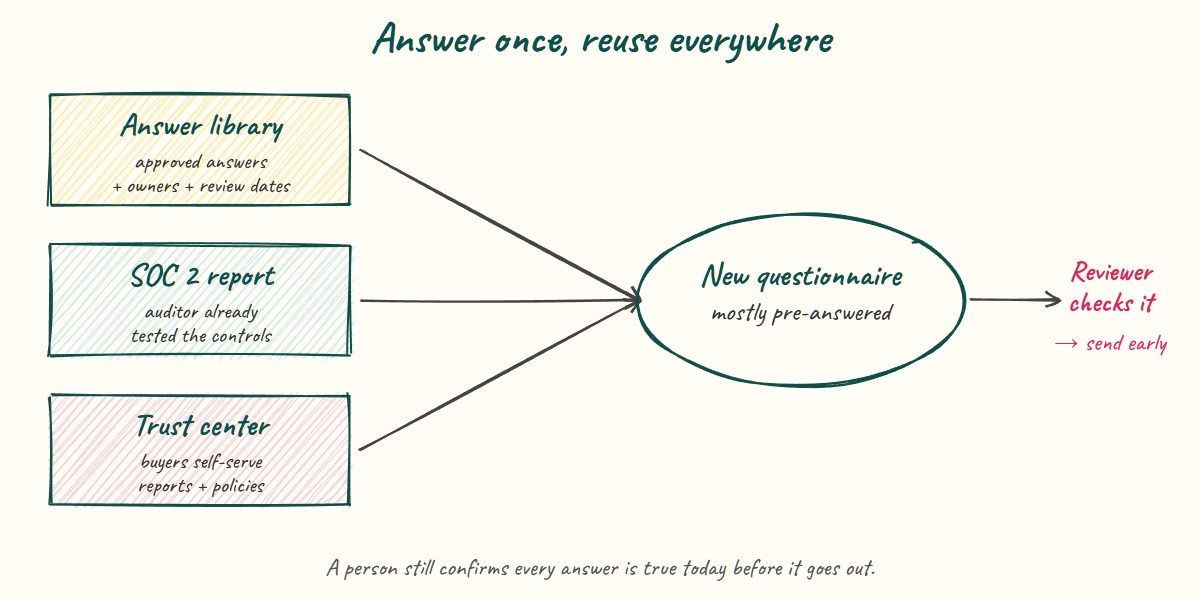
A security questionnaire answer library is one shared set of approved answers, organized by topic, with an owner and a review date for each.
- Organize by topic, for example access control, encryption and incident response, not by customer.
- Give each answer an owner who confirms it is still true.
- Add a review date and check answers every quarter or after a major change.
- Link the evidence to each answer so the policy or report goes out with it.
Most teams build the first version from their last five completed questionnaires, and the library then becomes the core of your AI knowledge base.
Answer Once: Use a SOC 2 Report and a Trust Center
You answer fewer security questionnaires when buyers can get a SOC 2 report and your security documents from a trust center first.
Many buyers will accept a SOC 2 Type 2 report in place of large parts of a questionnaire, because an auditor has already tested the controls. A trust center lets prospects request that report, your policies and your certificates without a single email. Between reports, a SOC 2 bridge letter covers the gap.
How to Use AI to Answer Security Questionnaires: Build a Knowledge Base
To answer security questionnaires with AI, give it a knowledge base of approved documents and a memory file of rules, then review every draft.
Without your own material, AI guesses, and a guessed answer can lose a deal. The knowledge base has two parts: context files with the facts, and a memory file that tells the AI how to use them.
What Goes in the Knowledge Base: Context Files
Context files are the documents the AI reads to find facts, so every answer traces back to something you have approved.
| Context file | What it gives the AI | Keep it fresh by |
|---|---|---|
| Answer library (export) | Approved short and long answers by topic | Owner review every quarter |
| Security policies | Exact wording for access, encryption, incident response, backups | Re-export after each policy approval |
| SOC 2 report or ISO 27001 certificate summary | What an auditor has already tested, and the audit period | Replace when a new report or bridge letter arrives |
| System and data flow description | Where data lives, hosting region, which services touch it | Update after any architecture change |
| Subprocessor and vendor list | Who else handles customer data | Update when you add or drop a vendor |
The Memory File: Rules the AI Follows Every Time
A memory file is a short instruction file the AI reads before every questionnaire, with company facts, answer rules and claims to avoid.
Most AI assistants let you save this as project instructions or a saved prompt, so you do not repeat it each time. A good memory file covers:
- Company facts: legal name, product in scope, hosting provider and region, frameworks you hold and their dates.
- Answer rules: lead with Yes, No or Partial; keep the first sentence short; name the evidence file for every answer.
- Never claim: certifications you do not hold, controls you only plan, or numbers that are not in a context file.
- When unsure: write "Needs owner" with the reason, instead of guessing.
Example rule lines: "If the context files do not answer the question, reply NEEDS OWNER. Cite the file name after every answer. Never say we hold a certification unless the certificate is in the context files."
How to Set It Up: 6 Steps
- Collect and clean the sources. Pull the latest versions and delete old ones so the AI cannot quote them.
- Write the memory file. Start with the rules above and add your company facts.
- Load both into a private AI workspace. Use a business plan that does not train on your data, or the security questionnaire automation in your compliance platform.
- Draft with sources. Paste the questions and ask for answers that cite the context file each one came from.
- Review every answer. The answer owner checks it is still true, fixes the wording of any gap and approves it.
- Save approved answers back. New and corrected answers go into the library, so the knowledge base gets better with each questionnaire.
What AI Cannot Do for You
AI drafts answers quickly, but it cannot confirm a control still works or decide how to explain a gap to a buyer.
Security questionnaire automation works best when your answer library is current. What these tools cannot do is decide whether an answer is still true or how to word a gap, so keep a reviewer on every questionnaire. Never paste secrets, keys or customer data into a public AI tool, and check how long your AI provider keeps what you upload. For the wider picture, see how compliance automation and AI agents for compliance fit in.
Common Mistakes in Security Questionnaire Responses
The most common security questionnaire mistakes are inconsistent answers, overpromising, missing the deadline and sharing too much.
- Inconsistent answers across sections or across customers.
- Overpromising controls you only plan to build.
- Missing the deadline, which slows the deal more than any single gap.
- Sharing too much, such as internal network diagrams, without an NDA.
- Skipping questions instead of explaining them.
How UprootSecurity Helps You Answer Security Questionnaires
UprootSecurity can answer security questionnaires for you: our AI drafts the answers from your approved documents, and our compliance team checks and completes them.
Send us the questionnaire and get it back filled in. Uproot's AI builds the first draft from your answer library, policies and audit reports, the same knowledge base approach described above. Your dedicated compliance expert then checks every answer, writes up any gaps honestly and flags anything that needs your input before it goes to the buyer.
| What you need | How UprootSecurity delivers it |
|---|---|
| Someone to answer it for you | Uproot's compliance team completes the questionnaire with you |
| Fast first drafts | Uproot AI drafts answers from your knowledge base (questionnaire automation on Growth and Enterprise plans) |
| Answers you can trust | A dedicated compliance expert reviews every answer, with 22 frameworks mapped to one set of controls |
| Fewer questionnaires | A trust center on Growth and Enterprise plans for your SOC 2 report and policies |
| Up-to-date evidence | Continuous monitoring across 140+ integrations |
| Proof beyond paperwork | A yearly penetration test included |
A security questionnaire holding up your next deal? → Book a demo today
Frequently Asked Questions
A security questionnaire is a list of questions a customer sends a vendor to check how it protects data before signing a contract. It covers topics like access control, encryption, incident response and vendor management, and it often asks for evidence such as a SOC 2 report or security policies.
The vendor fills out the security questionnaire, usually led by one owner from security, compliance or engineering. That owner pulls answers from an answer library and asks teams such as HR, legal and infrastructure for specific details. Sales sends it on, but should not answer technical questions alone.
A short security questionnaire can take an hour, while a long standard one such as the SIG can take days the first time. With an up-to-date answer library, a SOC 2 report and automation, most teams turn questionnaires around much faster, because they reuse approved answers instead of starting over.
You answer security questionnaires faster by keeping an approved answer library, assigning one owner, sharing a SOC 2 report and trust center up front, and using automation for first drafts. Reviewing answers every quarter keeps them accurate, so you spend less time checking facts on each new questionnaire.
The SIG, or Standardized Information Gathering questionnaire, is a vendor risk questionnaire published by Shared Assessments. Banks, insurers and large enterprises use it to assess their vendors. The sending organization licenses it, and vendors who receive one fill it in like any other questionnaire.
CAIQ, the Consensus Assessments Initiative Questionnaire, is a Cloud Security Alliance questionnaire of yes or no questions for cloud providers. It maps to the CSA Cloud Controls Matrix, the current version is 4.1, and it is free to download. Many SaaS companies complete it once and share it.
HECVAT, the Higher Education Community Vendor Assessment Toolkit, is a security questionnaire colleges and universities send to technology vendors. EDUCAUSE publishes it with Internet2 and REN-ISAC. Version 4 covers security, privacy, accessibility and AI, and it is free for institutions and their vendors.
A SOC 2 report often replaces large parts of a security questionnaire, but rarely all of it. Many buyers accept the report for control questions because an auditor already tested them. They may still send a shorter questionnaire for topics outside the report, such as privacy or AI use.
AI can draft answers to security questionnaires when you give it a knowledge base: your approved answer library, policies and audit reports as context files, plus a memory file of rules. It should not submit answers alone, because it cannot confirm that an answer is still true or word a gap carefully. Keep a person reviewing every answer.
If you don't meet a requirement, answer "No" honestly, explain what you do today, and give a dated plan to close the gap. Mention any compensating control that reduces the risk. Buyers accept honest gaps far more readily than answers that later prove false.
Sources
- Shared Assessments, SIG questionnaire and license pricing (checked Nov 2026): https://sharedassessments.org/sig/
- Cloud Security Alliance, CAIQ v4 (version 4.1, released Jan 27, 2026): https://cloudsecurityalliance.org/artifacts/star-level-1-security-questionnaire-caiq-v4
- EDUCAUSE, HECVAT 4 (current version 4.1.6, checked Nov 2026): https://www.educause.edu/hecvat