SOC 2 is an independent audit that checks how a service company protects its customers' data.
The company receives a report describing what was checked and the auditor's findings. Customers can use that report when deciding whether to trust the company with their data.
SOC 2 stands for System and Organization Controls 2. It was created by the American Institute of Certified Public Accountants (AICPA), and the audit is performed by a licensed CPA firm. SOC 2 isn't a government certification or a pass/fail badge, it's a professional attestation. It also has nothing to do with a SOC, or security operations center, which is a team that monitors security alerts.
A situation this actually solves: a payroll software company wants to sell to a larger business. The buyer asks how employees' salary information is protected. A SOC 2 report helps the buyer assess the provider's security measures. The auditor might examine who can access that information, and how access is removed when an employee leaves.
Is SOC 2 a Framework?
SOC 2 is often called a framework, and in practice it works like one. The AICPA's Trust Services Criteria set the areas a company must cover, and each company designs its own controls to meet them. Formally, though, SOC 2 is the report a CPA firm issues after testing those controls. See our SOC 2 framework page for how the controls fit together.
Who Asks for a SOC 2 Report, and Why
SOC 2 applies to service organizations that store, process, or transmit customer data. SaaS companies, cloud service providers, data centers, managed IT providers, HR platforms, and similar technology businesses. SOC 2 for SaaS companies in particular has become close to table stakes in enterprise sales. It's rare to get past procurement without one.
It isn't a legal requirement like HIPAA or GDPR, but it's become a commercial one. Large organizations routinely require a current SOC 2 report as part of vendor assessment, and deals are frequently paused until one is provided. Beyond closing deals, preparing for SOC 2 forces a company to document controls, close gaps, and build security habits that hold up over time, not just on the day of the audit.
The Five Areas SOC 2 Can Cover
An auditor evaluates against up to five Trust Services Criteria. Security is the only mandatory one; the rest are included based on what's relevant to the services a company provides.
- Security (mandatory). Protects against unauthorized access, misuse, and breaches. Example: multi-factor authentication on admin accounts.
- Availability. Covers whether systems are accessible as promised. Example: a tested disaster-recovery plan, not just a backup that's never been restored.
- Processing integrity. Covers whether the system processes data completely and accurately. Relevant to payment processors and similar systems where "did this transaction go through correctly" matters.
- Confidentiality. Covers whether data marked confidential stays that way throughout its lifecycle, through encryption and access restrictions.
- Privacy. Covers how personal information is collected, used, retained, and disposed of. Relevant to anyone handling PII or sensitive personal data.
See our full breakdown of the SOC 2 Trust Services Criteria for how each one maps to real controls.
SOC 2 Report Types: Type 1 vs Type 2
Understanding SOC 2 Type 1 vs Type 2 comes down to one question: does the report look at a single date, or a period of time?
| Type 1 | Type 2 | |
|---|---|---|
| What does it examine? | Whether the security measures are suitably designed at a specified date. | Their design and whether they operated effectively over an agreed period. |
| What time does it cover? | One specified date. | A defined period of time, agreed with the auditor. |
| Does it examine whether measures worked over time? | No. | Yes. |
A common misconception is that Type 2 always requires a fixed six-month minimum. It doesn't. The AICPA doesn't set a universal minimum reporting period. First-time Type 2 reports are sometimes as short as three months, with the exact period, and what work happens during it, agreed between the company and its auditor. What matters isn't a specific number of months, it's whether the period is long enough for the auditor to actually observe the controls operating.
Most enterprise customers ask for Type 2 specifically because it shows controls working over time, not just existing on paper for one day. Which report you need depends on what your buyers are actually asking for. Some accept Type 1 as an interim step, others want Type 2 from the start.
What Is a SOC 2 Report?
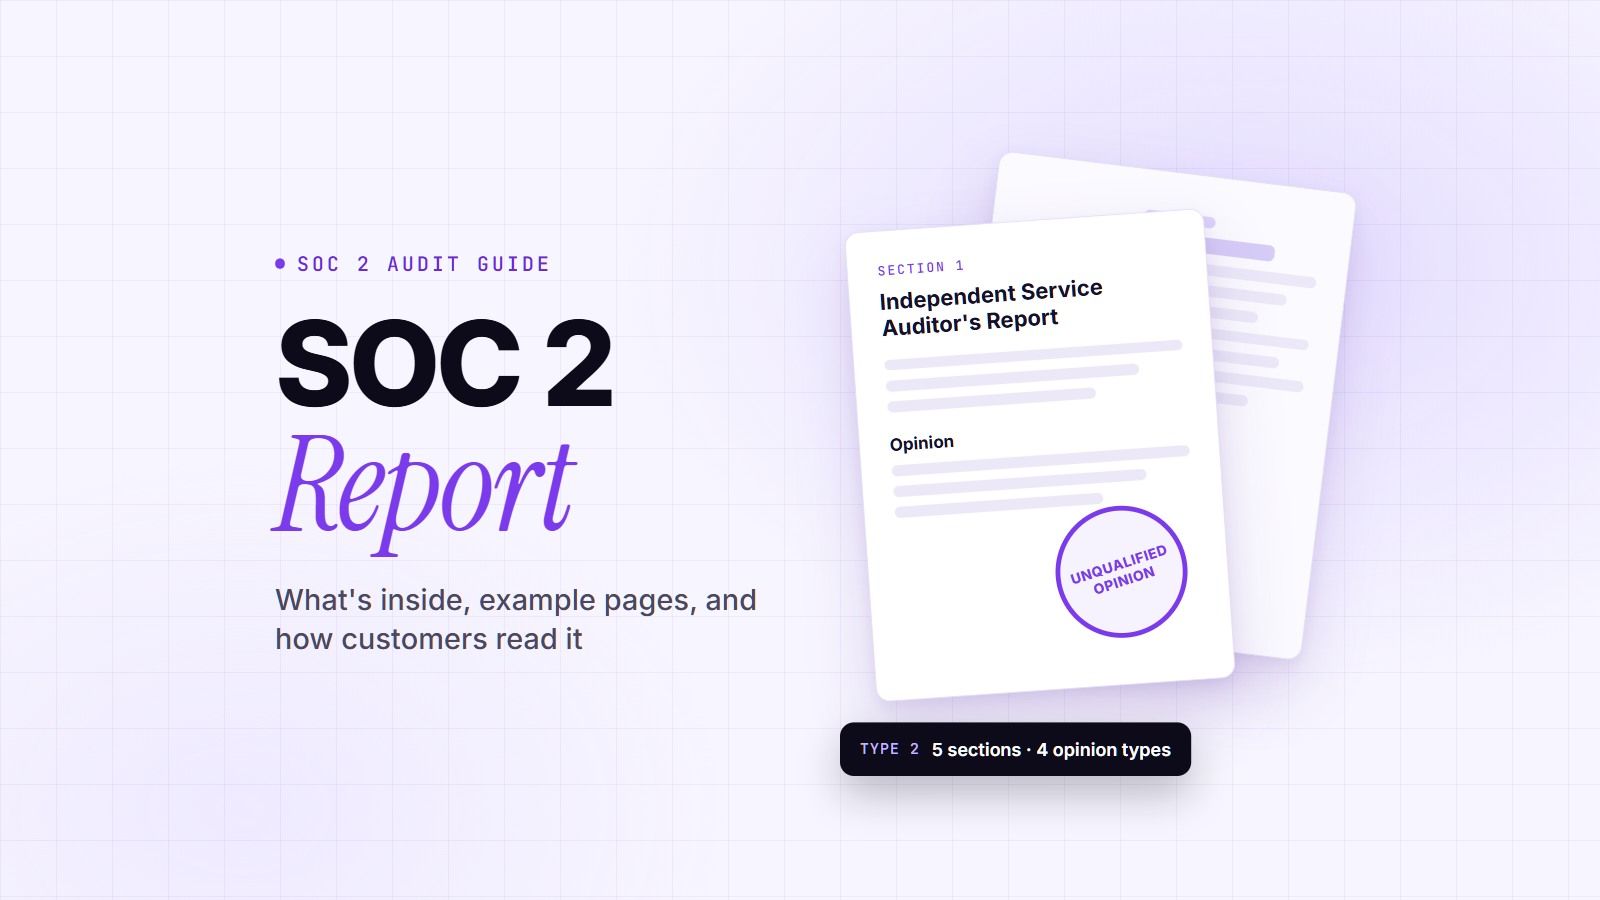
A SOC 2 report is the document a CPA firm issues after the audit, showing what it tested and its opinion. It isn't a simple pass/fail slip. The report contains several parts: management's assertion (the company's own statement that its controls operate as described), the auditor's opinion on whether that assertion holds up, a description of the system in scope, and the results of the auditor's testing, including any exceptions found.
The auditor's opinion falls into one of four categories:
- Unqualified. The best result. Controls are suitably designed and, for Type 2, operated effectively. No material exceptions.
- Qualified. Problems were found in specific areas, but the rest of the controls held up.
- Adverse. Controls are not suitably designed or not operating effectively. This is the result buyers worry about.
- Disclaimer of opinion. The auditor didn't have enough information to reach a conclusion.
A buyer reviewing your report should look at more than just the headline opinion. The system description and any noted exceptions tell them what was actually tested and what, if anything, needs follow-up. SOC 2 reports are confidential and typically shared under NDA or through a secure portal, not published publicly.
Can You Fail a SOC 2 Audit?
There is no formal pass or fail in SOC 2, but an adverse opinion works like a fail. A qualified opinion or a disclaimer also tells buyers something went wrong. A single exception, such as one missed access review, usually appears in the report with management's response and does not sink the whole report. A security incident during the audit period does not automatically mean failure either. What the auditor looks at is whether your controls responded the way they were designed to. See our SOC 2 audit process guide for what happens when an auditor finds an exception. Our guide to SOC 2 exceptions covers the types, the four opinions, and a management response template.
How a SOC 2 Audit Works
Only a CPA firm licensed by a U.S. state board of accountancy, independent of your organization, can issue a valid report. An auditor who also built your controls can't sign off on them. See our top SOC 2 auditors if you're choosing one.
The process itself, briefly:
- Scoping. Deciding which systems and which of the five criteria apply.
- Readiness assessment (optional, recommended). Checking controls against the criteria before the real audit, so gaps get fixed while they're still cheap to fix.
- The observation period (Type 2 only). Controls run and get evidenced over the agreed period.
- Examination. The auditor tests controls through document review, interviews, and technical checks.
- Reporting. The report is issued, typically a few weeks to two months after the period ends.
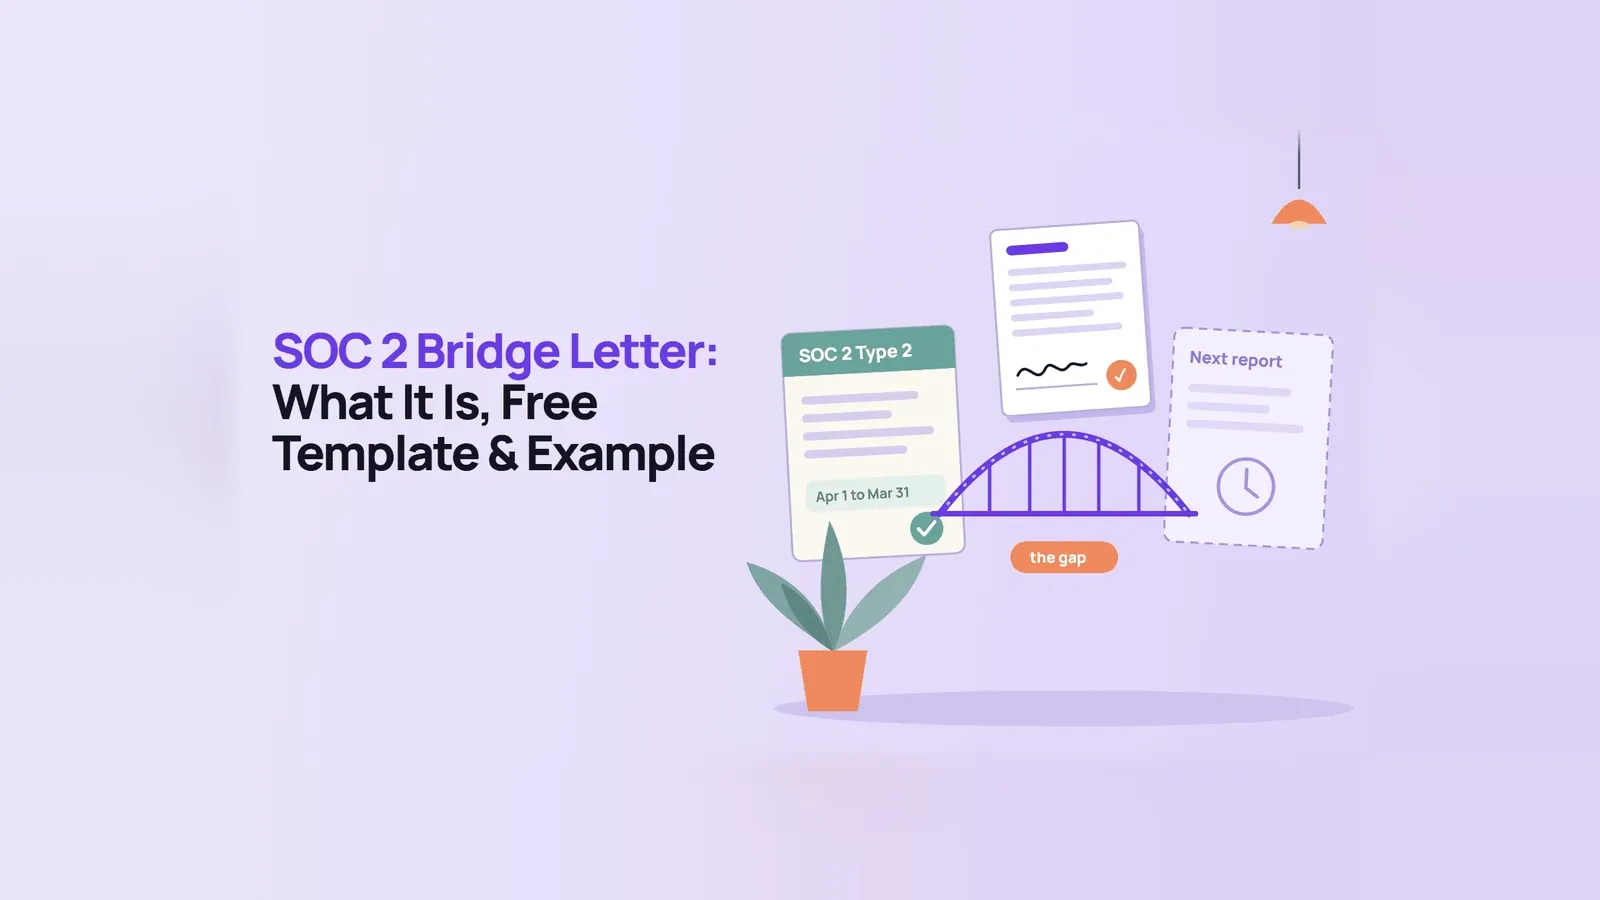
- Annual renewal. Most companies repeat this yearly, since reports are time-bound. If a customer needs assurance between reports, a SOC 2 bridge letter from your management can cover the gap.
Here's a SOC 2 audit example with real records, not just a category list:
| Business question | Example security measure | Example record an auditor might examine |
|---|---|---|
| Can former employees still access customer information? | Access is removed when someone leaves. | An offboarding record and account-removal timestamps. |
| Who is allowed to view sensitive information? | Access is reviewed and limited to appropriate staff. | An access list and a completed review record. |
| Can the company restore important information? | Backups are made and restoration is tested. | A dated restoration-test record, where relevant to the audit scope. |
For the full walkthrough, including report-section detail and what happens after you receive your report, see our SOC 2 audit process guide. Before the audit itself, most teams work through a SOC 2 readiness checklist covering access, HR, infrastructure, change management, and vendor management. Many teams also use SOC 2 compliance software to collect that evidence automatically.
What Affects the Time and Cost
How much does SOC 2 cost? There's no single number, but here are the ranges that matter. Audit fees typically range from $5,000 to $20,000, and total compliance cost, including readiness work, remediation, tooling, and internal time, typically lands between $10,000 and $100,000 for a first Type 2 report, based on company size. These are broad ranges; the actual number depends heavily on scope, how mature your controls already are, and which auditor you choose.
Timeline-wise, a Type 1 usually takes one to three months. For a Type 2, the auditor watches your controls over an agreed period, often three to six months for a first report, so a first Type 2 usually takes longer end to end once you add preparation and report writing.
How SOC 2 Compares to SOC 1, SOC 3, and ISO 27001
SOC 1 vs SOC 2 vs SOC 3. All three come from the AICPA, but answer different questions. In short:
| Report | What it covers | Who sees it |
|---|---|---|
| SOC 1 | Controls relevant to a customer's financial reporting | Customers and their auditors |
| SOC 2 | Security and the other Trust Services Criteria above | Customers, under NDA |
| SOC 3 | The same ground as SOC 2, in a short summary | Anyone, it is public |
If SOC 1 might be relevant to your business, see our SOC 1 vs SOC 2 comparison.
SOC 2 vs ISO 27001. SOC 2 is a U.S.-issued attestation, most recognized in North American procurement. ISO 27001 is an international certification, more widely recognized in Europe and Asia Pacific, built around implementing a full Information Security Management System against 93 reference controls (the standard was revised down from 114 controls in 2022). The two overlap significantly, which is why many companies pursue both rather than duplicating the work twice. See our full SOC 2 vs ISO 27001 comparison.
Frequently Asked Questions
No, SOC 2 is not a certification; it is an attestation report from an independent CPA firm. There's no pass/fail badge to display. The auditor issues an opinion alongside a description of what was tested, and companies usually share that report with customers under NDA. People still say "SOC 2 certified" informally, but the correct term is a SOC 2 report.
SOC 2 stands for System and Organization Controls 2. It is one of the SOC reports created by the AICPA, the U.S. accounting standards body. SOC 1 covers controls that affect a customer's financial reporting, SOC 2 covers security and data protection, and SOC 3 is a public summary of a SOC 2. It is not related to a security operations center.
No, SOC 2 is not legally required, but many enterprise customers require it before they buy. It has become a commercial requirement for SaaS and service companies selling to larger businesses. Customers routinely ask for a current report during vendor assessment, and deals are often paused until one is provided.
Service companies that store, process, or transmit customer data usually need a SOC 2 report. That includes SaaS companies, cloud and hosting providers, data centers, managed IT providers, and HR or payroll platforms. The real trigger is usually a customer asking for it, most often a larger business during its vendor security review.
No, ISO 27001 and SOC 2 are different, though much of the same security work supports both. SOC 2 is a U.S. attestation report from a CPA firm, most requested in North America. ISO 27001 is an international certification of a full information security management system, more common in Europe and Asia Pacific. Many companies pursue both and reuse the overlapping controls.
SOC 2 audit fees typically range from $5,000 to $20,000. Total cost for a first Type 2, including readiness work, fixing gaps, tools, and internal time, usually lands between $10,000 and $100,000. The final number depends on scope, how mature your controls already are, how many Trust Services Criteria you include, and which auditor you choose.
A first SOC 2 Type 2 usually takes longer than its observation period, which is often 3 to 6 months. Before that, you need time to prepare controls and fix gaps. After it ends, the auditor typically needs a few weeks to two months to issue the report. A Type 1, which looks at a single date, usually takes 1 to 3 months.
SOC 2 is not hard to understand, but it takes steady work over several months. Most effort goes into writing policies, setting up access reviews, onboarding and offboarding steps, and collecting evidence that controls ran. Your team does not need to be deeply technical, but someone must own the project. A readiness assessment before the audit makes it much easier.
There is no formal pass or fail, but an adverse opinion is effectively a failed SOC 2 audit. A qualified opinion or a disclaimer also signals problems to buyers. A single exception usually appears in the report with management's response rather than sinking it. Most bad outcomes come from skipping a readiness assessment before the audit starts.
Sometimes, if the customer agrees to accept a Type 1 while your Type 2 is in progress. Many buyers accept a Type 1 report plus a written plan showing when the Type 2 observation period ends. Ask early in the deal. If the contract or RFP strictly requires Type 2, a Type 1 alone usually will not meet it.
A SOC 2 report has no official expiry date, but most buyers expect one covering the last 12 months. That is why most companies repeat the audit every year. If there is a gap between your last report's end date and today, a bridge letter from your management can cover it until the next report is issued.
Only an independent CPA firm licensed by a U.S. state board of accountancy can perform a SOC 2 audit. The firm cannot have helped build the controls it is testing. Big 4 firms carry the highest fees and most recognized names; mid-tier and boutique firms with SOC experience are often a better fit for SaaS and mid-market companies on cost and responsiveness.
If you're still early in the process, our SOC 2 readiness checklist is a practical next step. See how Uproot Security helps organize SOC 2 preparation with continuous evidence collection and monitoring, or book a demo to see it against your own environment.