A GRC implementation roadmap is a phased plan for setting up governance, risk management and compliance in your company, from scope to audit-ready.
This guide gives you a 90-day GRC roadmap for 2027, built for a growing software company whose first goal is SOC 2 or ISO 27001.
It covers each phase, who owns what, the first controls to set up, how long GRC implementation really takes, and how to measure progress.
Reviewed by Riya Ann Varghese, GRC Engineer, ISO 27001 lead auditor certified. Last updated: November 10, 2026.
Looking for a GRC career roadmap instead? See our guide to the best GRC certifications.
What Is GRC Implementation?
GRC implementation means putting governance, risk management and compliance into daily practice, with owners, controls and evidence instead of documents on a shelf.
Governance sets who decides and how. Risk management finds and ranks what could go wrong. Compliance proves you meet the rules your customers and regulators expect. For the building blocks themselves, see our guide to the GRC framework. This roadmap shows how to implement GRC: the order and timing of the work.
The 90-Day GRC Implementation Roadmap for 2027
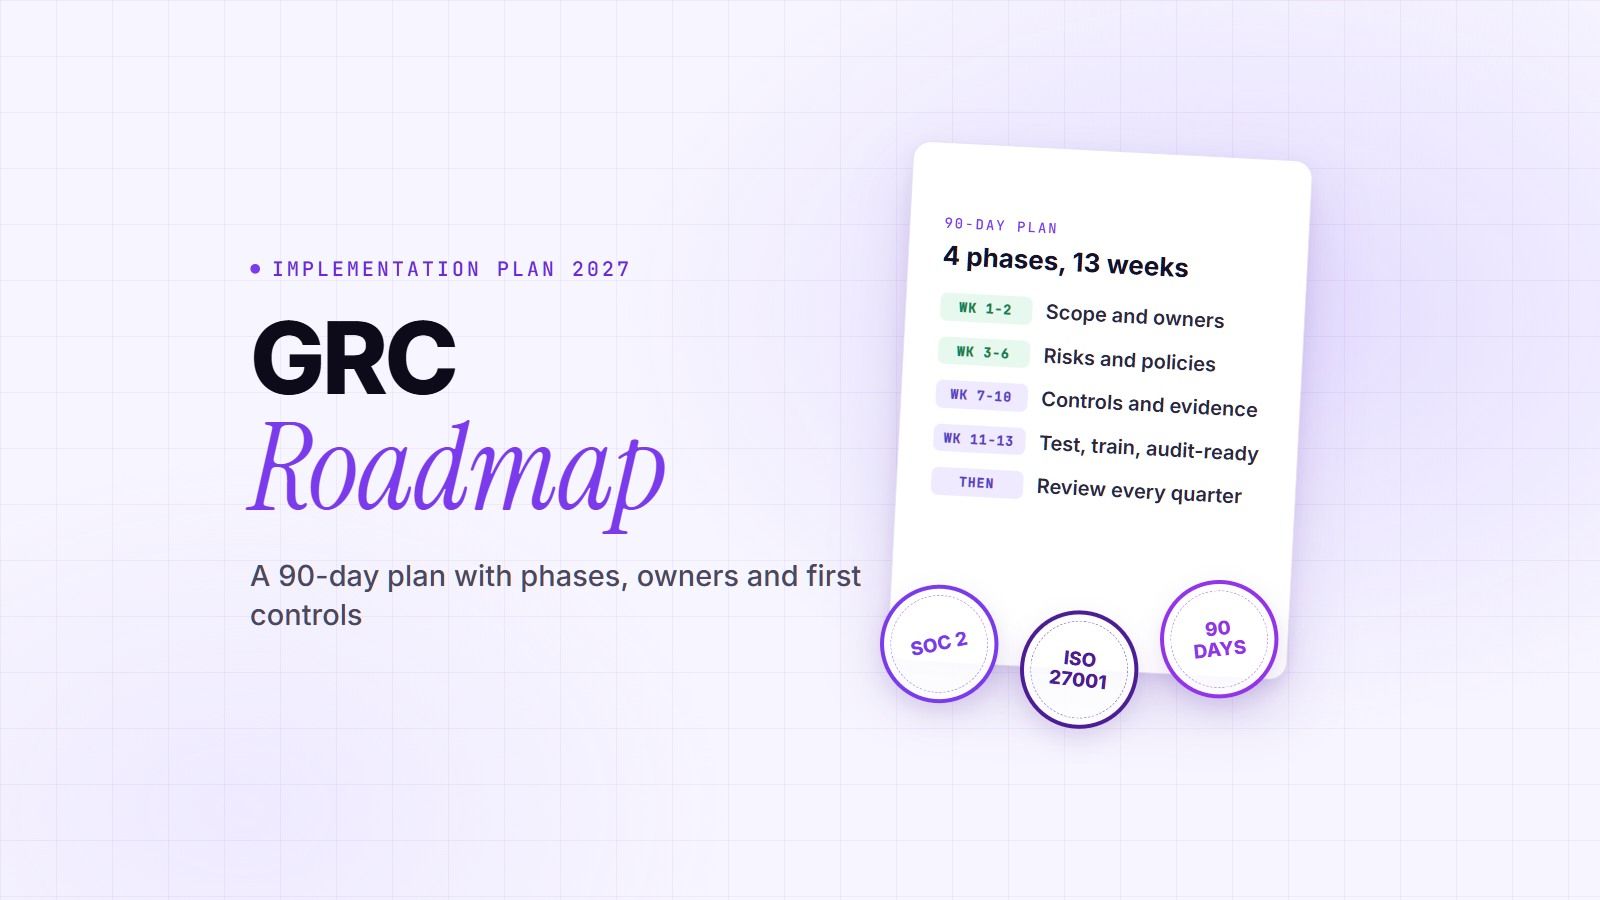
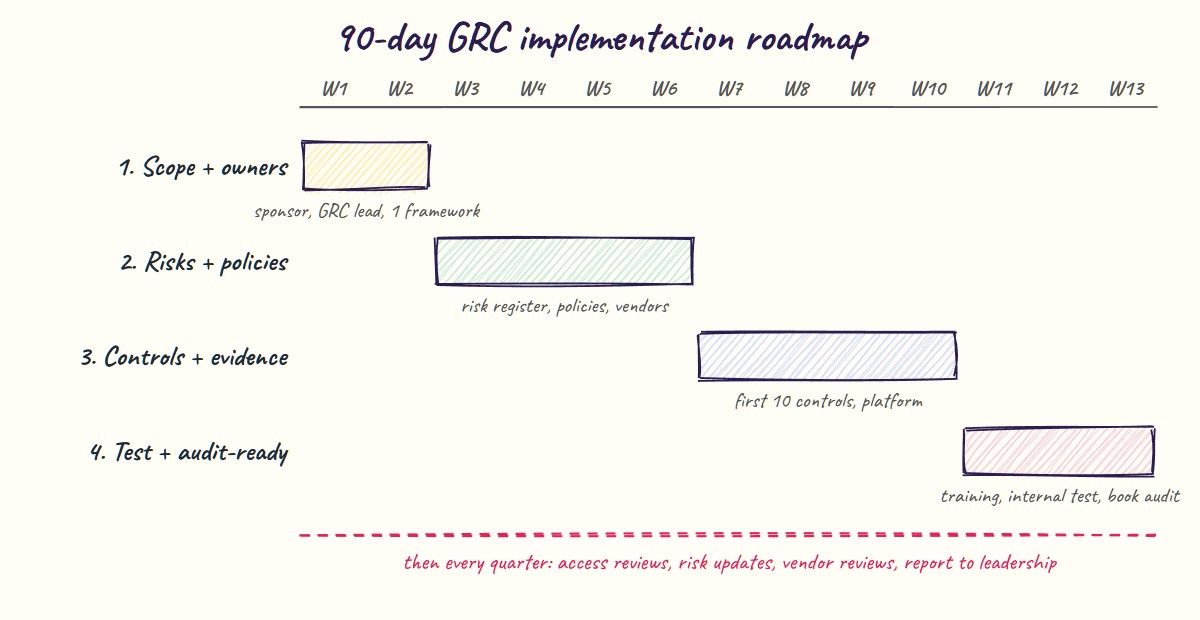
The GRC implementation roadmap runs in four phases over about 13 weeks: scope and owners, risks and policies, controls and evidence, then audit readiness.
| Phase | Weeks | What you do | Output | Lead owner |
|---|---|---|---|---|
| 1. Scope and ownership | 1 to 2 | Pick the first framework, define which products, systems and teams are in scope, name an executive sponsor and a GRC lead | Scope statement, owner list, project plan | CEO or CTO |
| 2. Risks and policies | 3 to 6 | Build an asset inventory, run a risk assessment, write and approve core policies, set up a vendor list | Risk register, approved policies, vendor list | GRC lead |
| 3. Controls, tools and evidence | 7 to 10 | Turn on the first controls, connect a GRC or compliance platform, start collecting evidence automatically | Controls in place, evidence flowing, gaps tracked | Engineering lead |
| 4. Test, train and get audit-ready | 11 to 13 | Run training, test controls internally, fix gaps, book the auditor | Internal test results, training records, audit date | GRC lead |
| Ongoing | Every quarter | Access reviews, risk updates, vendor reviews, policy updates, metrics to leadership | Quarterly GRC report | GRC lead |
Use the table as your GRC implementation plan, and copy the four phases into your project tracker as GRC implementation steps. Keep the first framework to one. Most teams that try SOC 2, ISO 27001 and HIPAA at once finish none of them on time.
Phase 1: Scope and Ownership (Weeks 1 to 2)
Phase 1 decides what the GRC program covers and who is accountable for it, before anyone buys a tool.
- Name the driver: the customer deal, regulation or investor asking for it.
- Pick one framework first, usually SOC 2 for US buyers or ISO 27001 for European buyers.
- Draw the scope line: which product, cloud accounts and teams are in, and which are out.
- Name owners: an executive sponsor, a GRC lead and one owner per control area.
Phase 2: Risks and Policies (Weeks 3 to 6)
Phase 2 finds your biggest risks and writes the policies that say how you will control them.
- Asset inventory: systems, data stores, laptops and SaaS tools in scope.
- Risk assessment: score each risk by likelihood and impact, and pick a treatment. Our guide to the GRC strategy and maturity model covers how to set risk appetite.
- Core policies: information security, access control, change management, incident response, vendor management and business continuity.
- Vendor list: every vendor that touches customer data, with its risk level.
Phase 3: Controls, Tools and Evidence (Weeks 7 to 10)
Phase 3 turns policies into working controls and starts collecting the evidence an auditor will ask for.
- Set up the first 10 controls listed below.
- Choose a platform that connects to your cloud, identity and code tools. Compare options in our GRC tools guide.
- Automate evidence collection so proof builds up daily instead of before the audit. See how GRC automation works.
- Track every gap as a ticket with an owner and a due date.
Phase 4: Test, Train and Get Audit-Ready (Weeks 11 to 13)
Phase 4 checks that controls actually work, trains staff, and gets you to a booked audit.
- Security awareness training for everyone, with completion records.
- Internal control testing: sample each control the way an auditor would.
- Fix the gaps the test finds, then retest.
- Book the auditor and agree the audit period. Our SOC 2 compliance checklist lists the evidence to prepare.
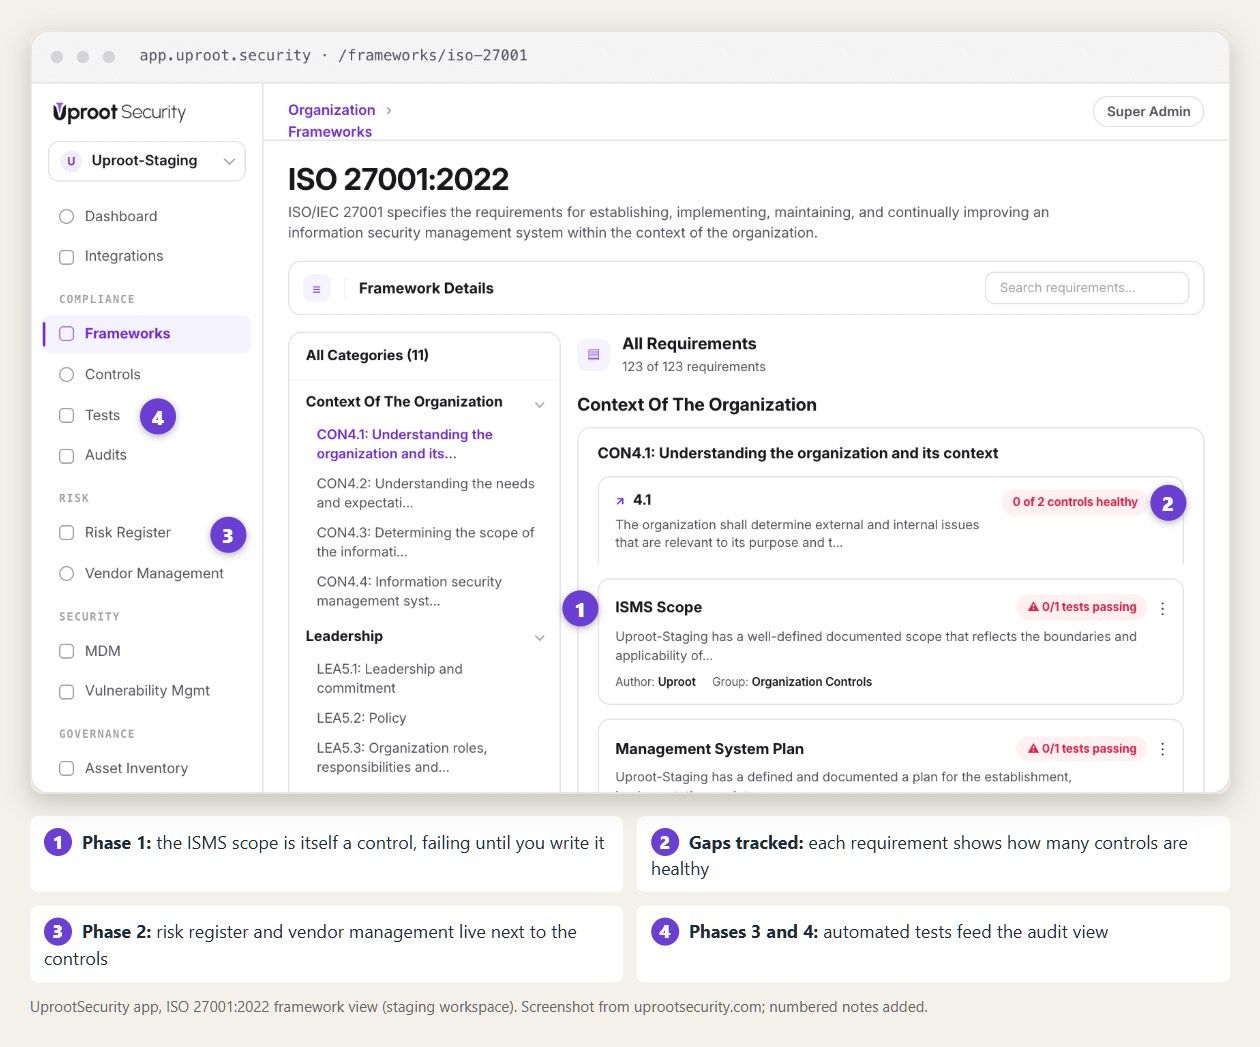
Want a roadmap built for your company? Talk to a compliance expert and we will map your 90 days in one call.
Who Owns What in a GRC Program?
A GRC program needs one accountable lead, an executive sponsor, and a named owner for every control area.
| Activity | CEO or CTO | GRC lead | Engineering | HR | Legal or finance |
|---|---|---|---|---|---|
| Set scope and budget | Accountable | Responsible | Consulted | Informed | Consulted |
| Risk assessment | Consulted | Accountable | Responsible | Consulted | Consulted |
| Policies | Approves | Accountable | Consulted | Consulted | Consulted |
| Technical controls and evidence | Informed | Accountable | Responsible | Informed | Informed |
| Onboarding, offboarding, training | Informed | Accountable | Consulted | Responsible | Informed |
| Vendor reviews and contracts | Informed | Accountable | Consulted | Informed | Responsible |
| Audit and customer questionnaires | Informed | Accountable | Responsible | Informed | Consulted |
In a startup, the GRC lead is often the CTO or a senior engineer working with an outside compliance expert.
The First 10 Controls to Set Up
The first GRC controls to set up are the ones auditors test most and attackers abuse most: access, data protection, logging and vendors.
| Control | SOC 2 | ISO 27001:2022 |
|---|---|---|
| Multi-factor authentication for all staff | CC6.1 | A.8.5 |
| Quarterly user access reviews | CC6.2, CC6.3 | A.5.18 |
| Offboarding within a set time | CC6.2 | A.5.18, A.6.5 |
| Encryption of stored data | CC6.1 | A.8.24 |
| Audit logging and alerts | CC7.2 | A.8.15 |
| Backups with a tested restore | A1.2 (if Availability is in scope) | A.8.13 |
| Vendor inventory and reviews | CC9.2 | A.5.19 |
| Risk register reviewed each quarter | CC3.2 | Clause 6.1.2 |
| Approved information security policies | CC5.3 | A.5.1 |
| Security awareness training | CC2.2 | A.6.3 |
Mappings show the closest requirement in each framework; your auditor decides how each control is tested.
How Long Does GRC Implementation Take?
GRC implementation takes about 90 days for a small software company, and longer for a first audit report or an enterprise rollout.
| Goal | Typical time |
|---|---|
| Working GRC program (owners, risks, policies, first controls) | About 90 days |
| First SOC 2 Type 1 report | About 3 to 4 months |
| First SOC 2 Type 2 report | About a year, including the 3 to 12 month observation period |
| ISO 27001 certificate | About 3 to 6 months for most small companies |
| Enterprise GRC software rollout | Often 6 months or more, depending on integrations and business units |
These are typical ranges from our work with SaaS companies, not guarantees. Our guide to the SOC 2 Type 2 report explains that timeline in detail.
GRC Roadmap by Company Size
A GRC roadmap changes with company size: startups need one framework fast, scaleups add frameworks, and enterprises add formal risk and audit functions.
| Size | What changes | Typical tooling |
|---|---|---|
| Startup (under 50 people) | One framework, the CTO as GRC lead, outside expert help | A compliance automation platform |
| Scaleup (50 to 500) | Second and third frameworks, a dedicated GRC owner, formal vendor reviews | Compliance automation plus a trust center |
| Enterprise (500+) | Enterprise risk management, internal audit, many business units | An enterprise GRC suite |
For what each option costs, see our GRC software pricing guide.
How to Measure GRC Progress
You measure GRC progress with a few numbers leadership can read each quarter, such as controls passing and risks past due.
- Controls passing: the share of controls with current, passing evidence.
- Risks past due: open risks whose treatment date has passed.
- Policy acknowledgment: the share of staff who have signed current policies.
- Evidence freshness: controls whose evidence is older than its review cycle.
- Questionnaire turnaround: days to answer a customer security questionnaire.
Common GRC Implementation Mistakes
The most common GRC implementation mistakes are buying a tool before setting scope, chasing several frameworks at once, and leaving controls without owners.
- Tool first, scope later. A platform cannot tell you which systems are in scope.
- Three frameworks at once. Finish one, then map its controls to the next.
- No named owners. Controls without an owner drift within a quarter.
- Spreadsheets that rot. Manual trackers go stale between audits.
- Policies nobody follows. Write policies that match how the team actually works.
How UprootSecurity Helps You Implement GRC
UprootSecurity gives you a dedicated compliance expert and a platform that runs your roadmap, so a small team reaches audit-ready.
| What the roadmap needs | How UprootSecurity delivers it |
|---|---|
| Scope, owners and a plan | A dedicated compliance expert who builds the roadmap with you |
| Risks, policies and vendors | Risk register, policy templates and vendor management in the platform |
| Controls and evidence | Continuous monitoring across 140+ integrations |
| The next framework | 22 frameworks mapped to one set of controls |
| Proof for customers | Trust center and questionnaire automation on Growth and Enterprise plans, plus a yearly penetration test included |
Need a GRC program running before your next enterprise deal? → Book a demo today
Frequently Asked Questions
A GRC implementation roadmap is a phased plan for setting up governance, risk management and compliance in a company. It lists the steps in order, with owners, outputs and dates, from defining scope through risk assessment, policies and controls to being ready for an audit.
GRC implementation usually takes about 90 days to reach a working program for a small software company. A first SOC 2 Type 2 report takes about a year end to end, and enterprise GRC software rollouts often take six months or more, depending on integrations and business units.
The steps to implement GRC are to set scope and owners, assess risks, write policies, set up controls and a platform, collect evidence, train staff, test controls internally and book the audit. After that, you run reviews every quarter so the program stays current between audits.
A GRC program is the ongoing set of people, processes and tools a company uses to govern security decisions, manage risk and prove compliance. It includes owners, a risk register, policies, controls, evidence and regular reviews, and it usually supports frameworks such as SOC 2, ISO 27001 or HIPAA.
In a startup, the CTO or a senior engineer usually owns GRC, often with help from an outside compliance expert. The CEO acts as executive sponsor and approves policies. As the company grows past about 50 people, many hire or appoint a dedicated GRC or compliance lead.
A startup should start a GRC program when enterprise customers begin asking for SOC 2, ISO 27001 or security questionnaires, or when it handles sensitive data. Starting before the first big deal is easier, because controls set up early cost less than fixing habits later.
Implement the framework your customers ask for first. For most US software companies that is SOC 2, and for companies selling mainly in Europe or the UK it is ISO 27001. Once one is in place, much of the evidence carries over to the next framework.
You can start GRC with documents and spreadsheets, but most growing companies move to GRC or compliance software within the first year. Software collects evidence automatically, tracks owners and reminds people of recurring tasks, which spreadsheets cannot do reliably once you have several frameworks or many controls.
GRC implementation cost depends on company size, frameworks and tooling. Small companies mainly pay for a compliance platform, audit fees and staff time, while enterprises pay more for enterprise GRC suites and rollout services. Our GRC software pricing guide compares current platform costs and hidden fees.
A GRC framework describes what your program contains, such as policies, controls, risk methods and roles. A GRC roadmap describes when and in what order you build it, with phases, owners and dates. You need both: the framework is the blueprint, and the roadmap is the build plan.
Sources
- AICPA, 2017 Trust Services Criteria (with revised points of focus, 2022): https://www.aicpa-cima.com/resources/download/2017-trust-services-criteria-with-revised-points-of-focus-2022
- ISO/IEC 27001:2022, Annex A control numbers (standard document): https://www.iso.org/standard/27001