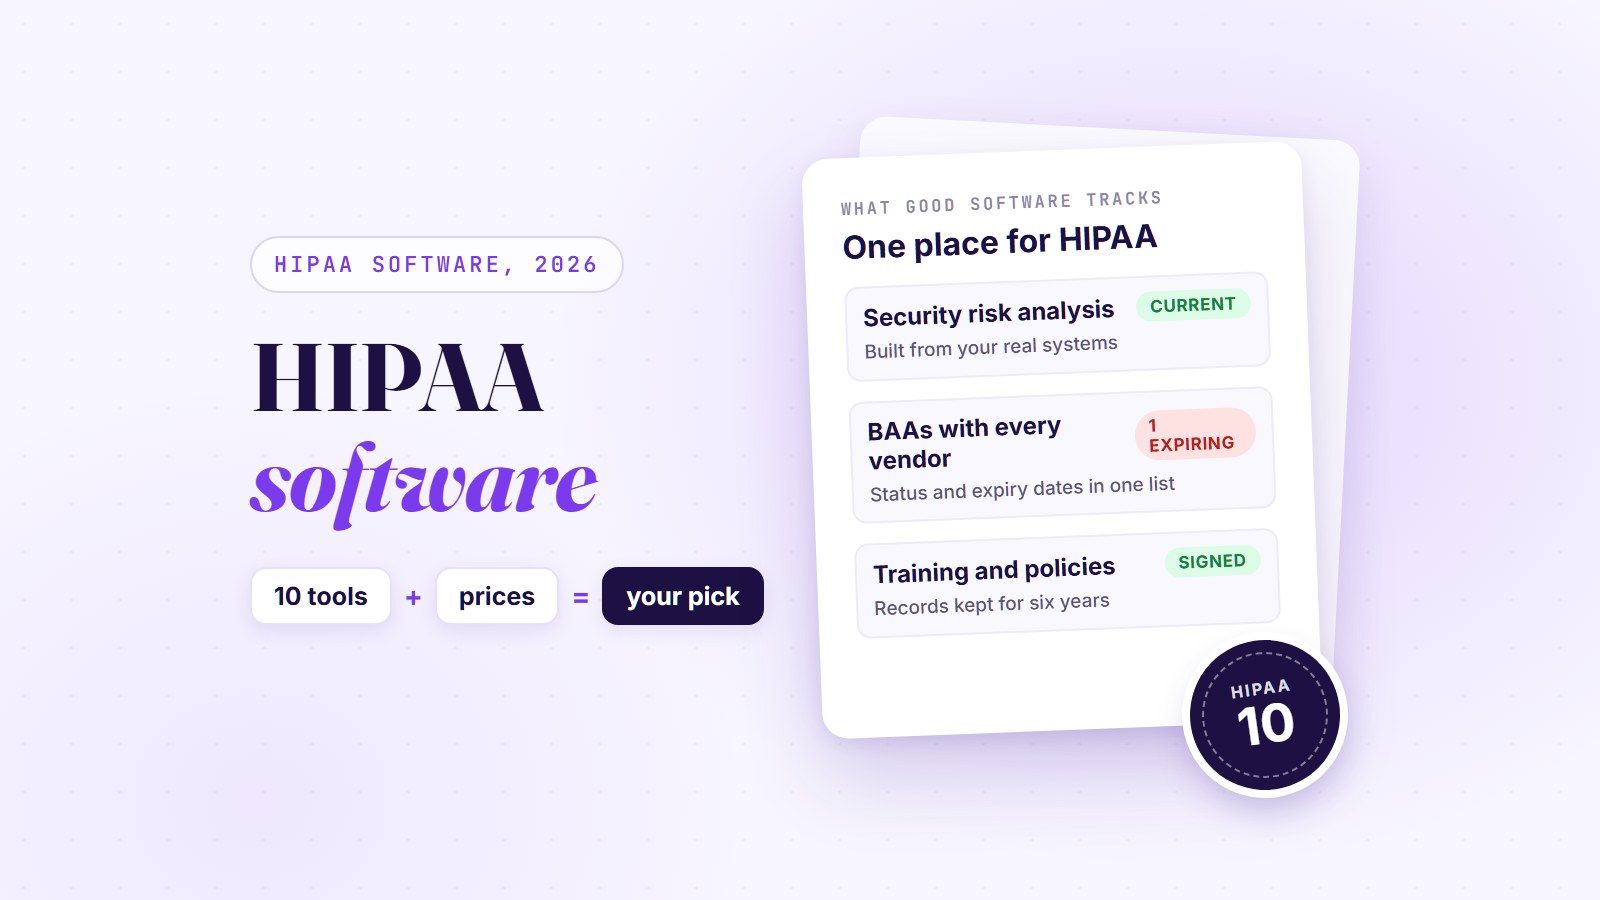
HIPAA compliance software, also called HIPAA compliance tools, helps you run and prove your HIPAA program: risk analysis, policies, staff training, vendor agreements and audit evidence in one place.
It does not make you compliant on its own. It keeps the work organized, reminds people what is due, and gives you proof when a customer or regulator asks. This guide compares 10 HIPAA compliance software tools, shows the prices that are published, and explains how to pick one. New to HIPAA? Start with our HIPAA compliance hub.
Reviewed by Riya Ann Varghese, GRC Engineer, ISO 27001 lead auditor certified. Last updated November 20, 2026.
HIPAA Compliance Software vs HIPAA-Compliant Software
HIPAA compliance software manages your compliance program, while HIPAA-compliant software is any app that can safely store or send patient data under a signed business associate agreement (BAA).
| HIPAA compliance software | HIPAA-compliant software | |
|---|---|---|
| What it is | A tool to run and prove your HIPAA program | An app that handles PHI safely |
| Examples | Compliance platforms like the 10 below | EHRs, secure email, cloud storage, Microsoft 365 or Google Workspace under a BAA |
| Main job | Risk analysis, policies, training, BAAs, evidence | Storing, sending or processing patient data |
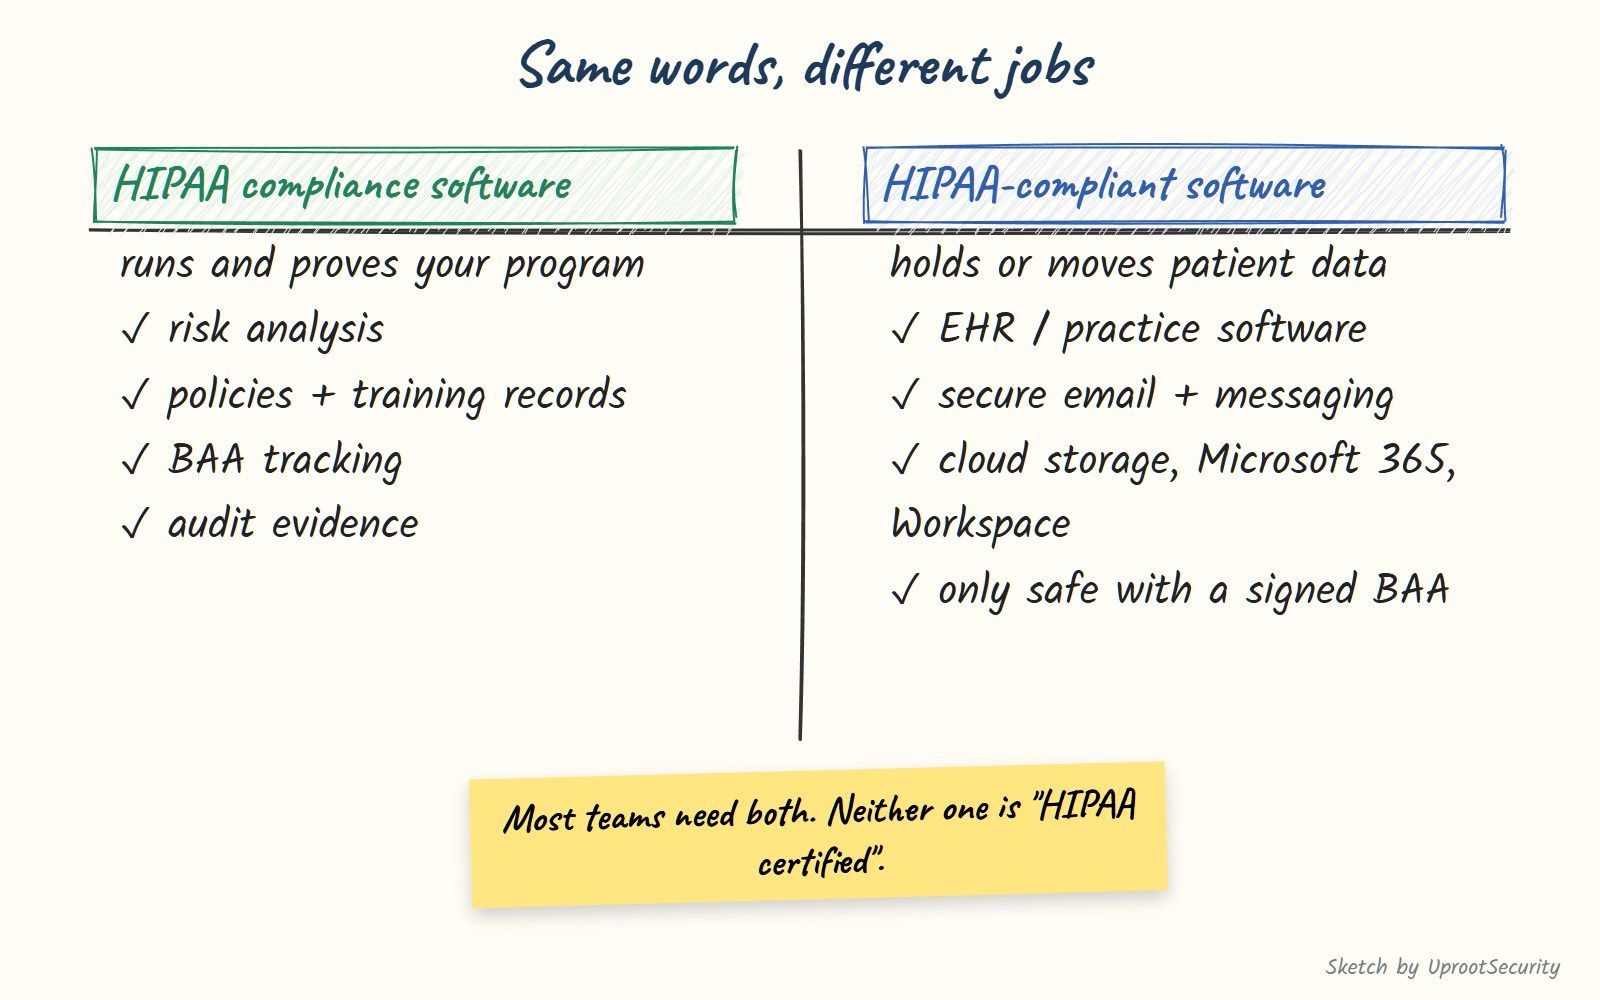
This guide covers the first kind. If you are looking for an EHR or therapy practice software, that is a different category.
Best HIPAA Compliance Software and Solutions in 2026
The 10 tools below, which are the HIPAA compliance solutions we see buyers compare most, fall into two groups. Healthcare-only tools suit practices and clinics. Multi-framework platforms suit health-tech and SaaS companies that also need SOC 2 or ISO 27001. We make UprootSecurity, so we list it first and describe it the same way as the others.
| Tool | Type | Best for | Published price |
|---|---|---|---|
| UprootSecurity | Multi-framework + dedicated expert | Health-tech and SaaS business associates | Custom quote |
| Compliancy Group (The Guard) | Healthcare-only, coached | Small to mid-size providers and vendors | Quote only |
| Accountable | Healthcare-only | Small practices and early startups | $169, $254 or $679/month, billed annually |
| Vanta | Multi-framework | SaaS companies handling PHI | Quote only |
| Drata | Multi-framework | Larger health-tech and SaaS teams | Quote only |
| Secureframe | Multi-framework | Tech companies needing HIPAA and SOC 2 | Quote only |
| Sprinto | Multi-framework | Startups and SaaS | Quote only |
| Medcurity | Healthcare-only | Practices, clinics and rural hospitals | From $499/year (small practice risk analysis) |
| Abyde | Healthcare-only | Small medical and dental practices | Quote only (by locations and staff) |
| HIPAA One (Intraprise Health) | Healthcare-only | Practices up to health systems | Quote only |
Prices were checked on each vendor's own website in October 2026, and Accountable and Medcurity were re-checked on November 20, 2026. "Quote only" means the vendor does not publish a price.
1. UprootSecurity
UprootSecurity is a compliance platform that maps the HIPAA Security Rule to your real systems and pairs every customer with a dedicated compliance expert.
- Risk analysis built from your environment and kept current.
- BAA tracking with status and expiry, and policy records kept for six years.
- HIPAA, SOC 2 and ISO 27001 on one set of controls, with 22 frameworks and 140+ integrations.
- Trust center and security questionnaire automation on Growth and Enterprise plans, and a yearly penetration test included.
Tradeoff: built for tech companies; a small dental office may not need multi-framework features. Price: custom quote.
2. Compliancy Group (The Guard)
Compliancy Group's The Guard walks healthcare organizations through HIPAA with guided self-audits and a compliance coach.
- Six self-audits for covered entities (five for business associates) with gap remediation.
- Policy templates, yearly training with attestation tracking, and incident reporting.
- Vendor and BAA management, plus OSHA coverage.
Tradeoff: healthcare-only, so it will not cover SOC 2 if customers ask. Price: quote only.
3. Accountable
Accountable is a HIPAA platform for small healthcare businesses that publishes its prices.
- Security risk assessment, policies, training and incident response.
- Vendor and BAA management, a data flow map and a trust center.
- Higher plans add phishing simulation, vulnerability scans and a yearly pentest.
Tradeoff: best for small teams; extra seats add cost as you grow. Price: $169, $254 or $679 a month billed annually ($199, $299 or $799 billed monthly), with 15 to 20 seats included.
4. Vanta
Vanta is a multi-framework compliance platform with a HIPAA product for SaaS companies that handle PHI.
- HIPAA policy templates and built-in training.
- Vendor risk management, including collecting BAAs from your vendors.
- Continuous monitoring with evidence pulled from your systems, mapped to SOC 2, ISO 27001 and GDPR.
Tradeoff: powerful for tech companies, but a lot of platform for a small clinic. Price: quote only. See our Vanta review for real-world pricing.
5. Drata
Drata is a compliance automation platform that links HIPAA risks to controls and monitors them continuously.
- Risk management tied to HIPAA controls.
- Policy reviews and versioning, and business associate reviews through vendor workflows.
- Controls reused across SOC 2, ISO 27001 and other frameworks.
Tradeoff: its HIPAA pages do not mention built-in training, and it fits larger teams best. Price: quote only. See our Drata review.
6. Secureframe
Secureframe offers HIPAA alongside SOC 2, ISO 27001 and NIST frameworks.
- HIPAA policy library with employee sign-off and training with quizzes.
- Vendor tracking, with BAAs sent for e-signature and stored.
- Continuous monitoring with 150+ integrations.
Tradeoff: its HIPAA page does not describe a dedicated HIPAA risk assessment workflow. Price: quote only. See our Secureframe review.
7. Sprinto
Sprinto is a compliance automation platform for startups that covers HIPAA among its frameworks.
- Periodic risk assessments and AI-assisted policies.
- Ready-made training and vendor reviews.
- Continuous monitoring across its integrations.
Tradeoff: Sprinto has no dedicated HIPAA product page, so confirm HIPAA depth in a demo. Price: quote only. See our Sprinto review.
8. Medcurity
Medcurity focuses on the HIPAA security risk analysis for healthcare providers.
- Risk analysis across administrative, physical, technical and privacy safeguards.
- A guided tier with an onsite physical assessment and year-round advising.
- Training, policies, BAA tracking and network vulnerability assessments.
Tradeoff: healthcare-only and provider-focused. Price: from $499 per year for the self-service small practice risk analysis; larger organizations get a quote.
9. Abyde
Abyde offers HIPAA programs for small medical and dental practices, with separate versions for covered entities and business associates.
- Security risk analysis with a scorecard.
- Auto-generated policies and staff training.
- Business associate management, OSHA coverage and live support.
Tradeoff: built for practices, not software companies. Price: quote only, based on locations and employees, with 10% off for paying upfront.
10. HIPAA One (Intraprise Health)
HIPAA One, now offered by Intraprise Health, automates security and privacy risk assessments for healthcare organizations.
- Security risk analysis and privacy and breach risk assessments.
- Workforce training.
- Optional review by a professional assessor.
Tradeoff: assessment-focused rather than a full program tool. Price: quote only.
Not sure if you need a healthcare-only tool or a multi-framework platform? Talk to a compliance expert before you book demos with five HIPAA compliance software vendors.
How Much Does HIPAA Compliance Software Cost?
HIPAA compliance software costs from about $500 a year for a small-practice risk analysis to about $8,000 a year for a full small-business plan, with multi-framework platforms priced by quote.
Published prices from the tools above:
- Medcurity: from $499 per year for a small practice risk analysis.
- Accountable: $2,028, $3,048 or $8,148 per year, billed annually.
Multi-framework platforms such as Vanta, Drata, Secureframe and Sprinto do not publish prices. Our reviews of each tool show what buyers report paying.
Software is not the whole cost. Budget for:
- Risk analysis help if you want an expert to run or review it.
- Penetration testing and vulnerability scans, which hospital customers often ask for.
- Staff time to fix gaps, write procedures and collect evidence.
- A SOC 2 audit if customers want third-party proof. Audit firms charge for this separately.
HIPAA Compliance Software Requirements: What to Look For
Good HIPAA compliance management software must support a real risk analysis, policies, training, BAA tracking, and evidence you can show an auditor or customer.
| Feature | Why it matters | Question to ask the vendor |
|---|---|---|
| Security risk analysis | Required by the Security Rule and the first thing OCR asks for | Is it built from our systems or a questionnaire template? |
| Policy management | Policies must be current, acknowledged and kept six years | Do you track versions, sign-off and retention? |
| Training and attestation | You must prove each person was trained | Can we assign role-based training and export records? |
| BAA and vendor management | Every vendor that touches PHI needs a BAA | Do you track BAA status and expiry dates? |
| Continuous monitoring | Catches drift like disabled MFA or logging | Which of our systems do you connect to? |
| Incident and breach logging | Breaches have reporting deadlines | Can staff report incidents, and is there a breach workflow? |
| Evidence and reporting | You need proof for customers and regulators | Can we export an evidence package? |
| Multi-framework support | Saves work if you also need SOC 2 or ISO 27001 | Are HIPAA controls mapped to SOC 2? |
Need a step-by-step list of what your program should cover? Use our HIPAA compliance checklist.
Covered Entity or Business Associate: Which Tool Fits?
Healthcare providers usually fit a healthcare-only tool, while software vendors that handle PHI usually fit a multi-framework platform.
- Covered entities (practices, clinics, hospitals, health plans) need patient-facing privacy work, training for clinical staff and often OSHA. Tools like Compliancy Group, Abyde, Medcurity and HIPAA One are built for this.
- Business associates (health-tech, SaaS, billing and analytics vendors) need technical safeguards, cloud monitoring and proof for hospital customers, often a SOC 2 report too. Multi-framework platforms such as UprootSecurity, Vanta, Drata, Secureframe and Sprinto fit better.
Not sure which you are? See our guide to HIPAA covered entities.
Using HIPAA and SOC 2 Together
HIPAA and SOC 2 share many controls, so one well-run program can cover most of both.
| Control | HIPAA Security Rule | SOC 2 criteria |
|---|---|---|
| Risk assessment | 164.308(a)(1)(ii)(A) | CC3.2 |
| Security training | 164.308(a)(5) | CC1.4, CC2.2 |
| Incident response | 164.308(a)(6) | CC7.3, CC7.4 |
| Vendor agreements | 164.308(b) (BAAs) | CC9.2 |
| Access control | 164.312(a) | CC6.1 |
| Audit logging | 164.312(b) | CC7.2 |
| Encryption in transit | 164.312(e) | CC6.7 |
The differences matter too. HIPAA has rules SOC 2 does not, such as BAAs, patient privacy rights and breach notification deadlines. SOC 2 ends in an independent auditor's report, which HIPAA does not require. Learn more in What is SOC 2.
Red Flags When Choosing HIPAA Software
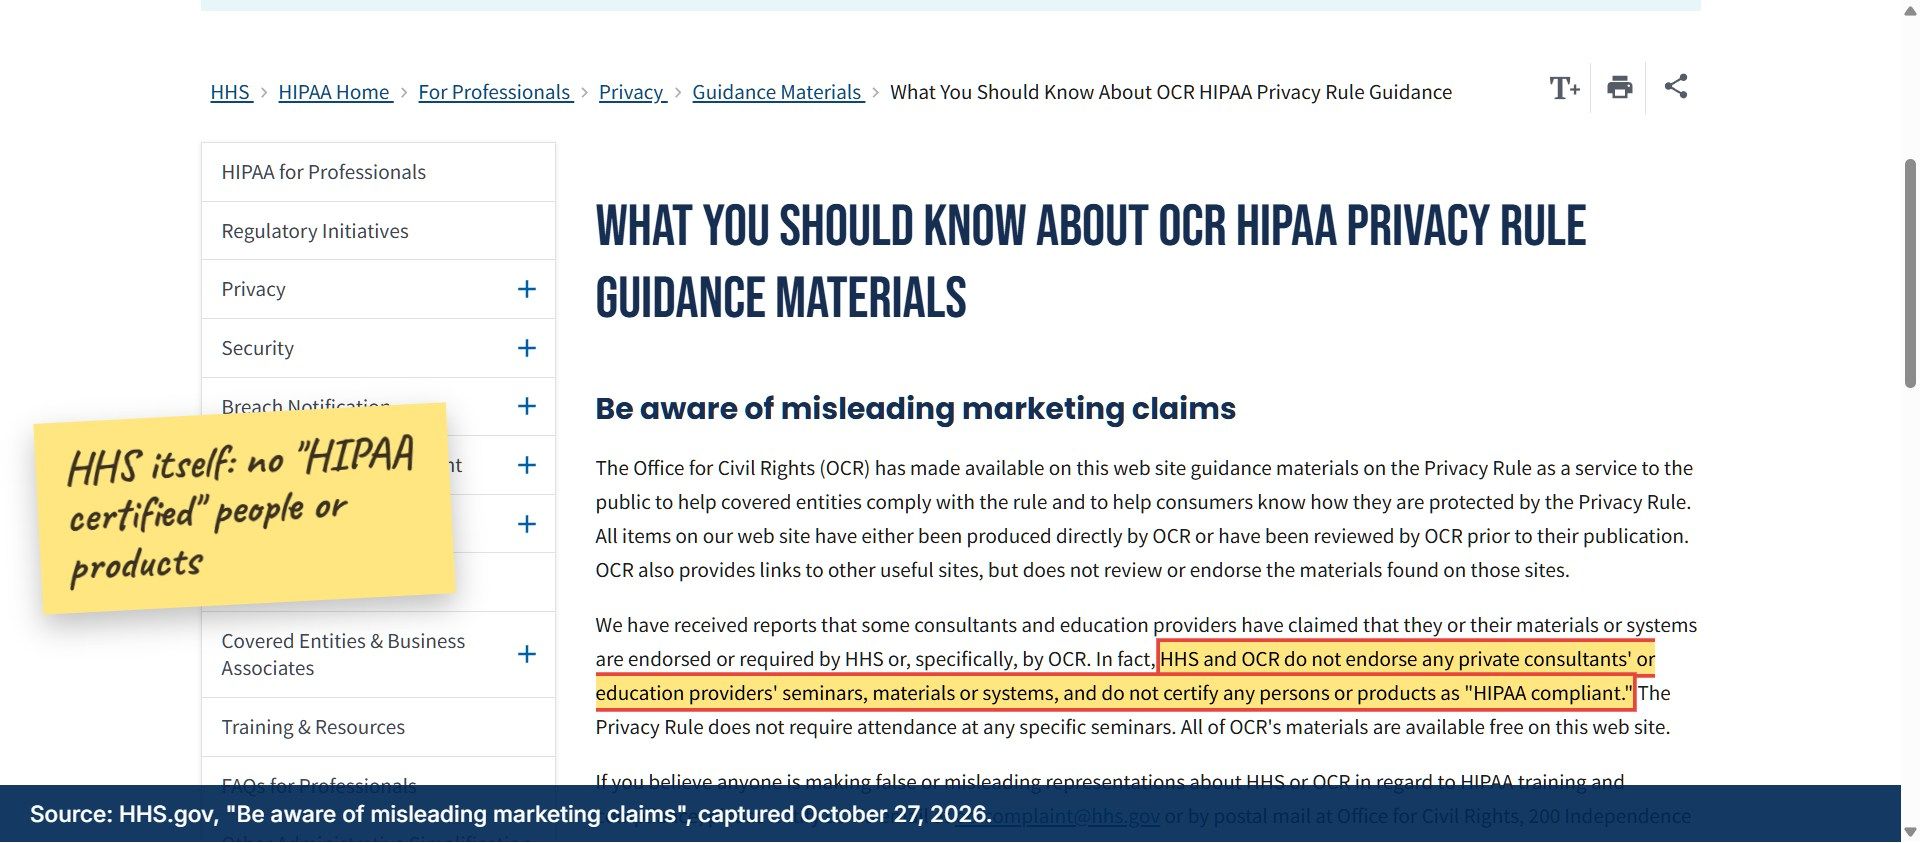
- "HIPAA certified" badges. HHS does not certify any person or product as HIPAA compliant, so treat badges and seals as marketing.
- Thinking software equals compliance. The tool tracks the work. Your team still has to do it.
- Template-only risk analysis. A generic questionnaire is not an accurate and thorough analysis of your systems.
- No plan for BAAs. If the tool cannot track vendor agreements, you will miss one.
How UprootSecurity Helps You Run HIPAA Without the Spreadsheets
UprootSecurity gives health-tech and SaaS teams one platform for HIPAA and the frameworks customers ask for next, with a dedicated expert to guide the work.
| What you need | How UprootSecurity delivers it |
|---|---|
| A risk analysis that matches your systems | Maps the Security Rule to your environment and keeps it current |
| Every vendor under a BAA | BAA tracking with status and expiry dates |
| HIPAA and SOC 2 without double work | 22 frameworks on one set of controls, 140+ integrations |
| Fast answers for hospital security reviews | Trust center and questionnaire automation on Growth and Enterprise plans |
| Someone to ask when it gets hard | A dedicated compliance expert |
| Security testing customers expect | A yearly penetration test is included |
Still running HIPAA from spreadsheets and shared drives? → Book a demo today
Frequently Asked Questions
The best HIPAA compliance software depends on who you are. Small practices often choose healthcare-only tools such as Medcurity, Accountable or Compliancy Group. Health-tech and SaaS companies that also need SOC 2 usually choose a multi-framework platform such as UprootSecurity, Vanta, Drata or Secureframe.
HIPAA compliance software costs from about $499 a year for a small-practice risk analysis to around $8,000 a year for a full small-business plan. Multi-framework platforms that also cover SOC 2 do not publish prices and quote by company size and frameworks. Also budget for testing, staff time and any audit.
There is no HIPAA-certified software. HHS does not certify any person or product as HIPAA compliant, so "HIPAA certified" badges are marketing. What matters is whether a vendor will sign a BAA when it handles PHI, and whether your own program, policies and safeguards meet the rules.
HIPAA compliance software helps you run and prove your HIPAA program with risk analysis, policies, training and BAA tracking. HIPAA-compliant software is any app, such as an EHR or secure email, that can safely handle patient data under a signed BAA. Most organizations need both.
Software cannot make you HIPAA compliant on its own. It organizes the work and collects proof, but your team still has to complete the risk analysis, fix gaps, train staff and sign BAAs. Tools that include a compliance expert help close that gap.
Startups that handle PHI for healthcare customers must meet HIPAA, but software is not legally required. Most startups use it because hospital customers ask for a risk analysis, policies, training records and BAAs before buying, and software makes that proof quick to share.
HIPAA compliance software should include a security risk analysis, policy management with six-year retention, training with attestation, BAA and vendor tracking, incident logging and exportable evidence. Software vendors should also look for continuous monitoring and SOC 2 mapping.
Microsoft 365 and Google Workspace can be used with PHI once a BAA is in place. Microsoft offers its BAA by default through its data protection terms, and Google Workspace admins accept a BAA in the Admin console. Personal Gmail accounts are not covered, so never use them for PHI.
OpenAI signs a BAA for eligible API customers and for sales-managed ChatGPT Enterprise and Edu accounts, but not for ChatGPT Business. Without a signed BAA, do not put PHI into ChatGPT. Check OpenAI's current terms before use, since they change.
The proposed HIPAA Security Rule update from January 2025 is still not final, and regulators now target July 2027. It would make safeguards such as encryption, multi-factor authentication and yearly penetration tests mandatory. Until then, the current Security Rule applies, but good software can help you prepare.