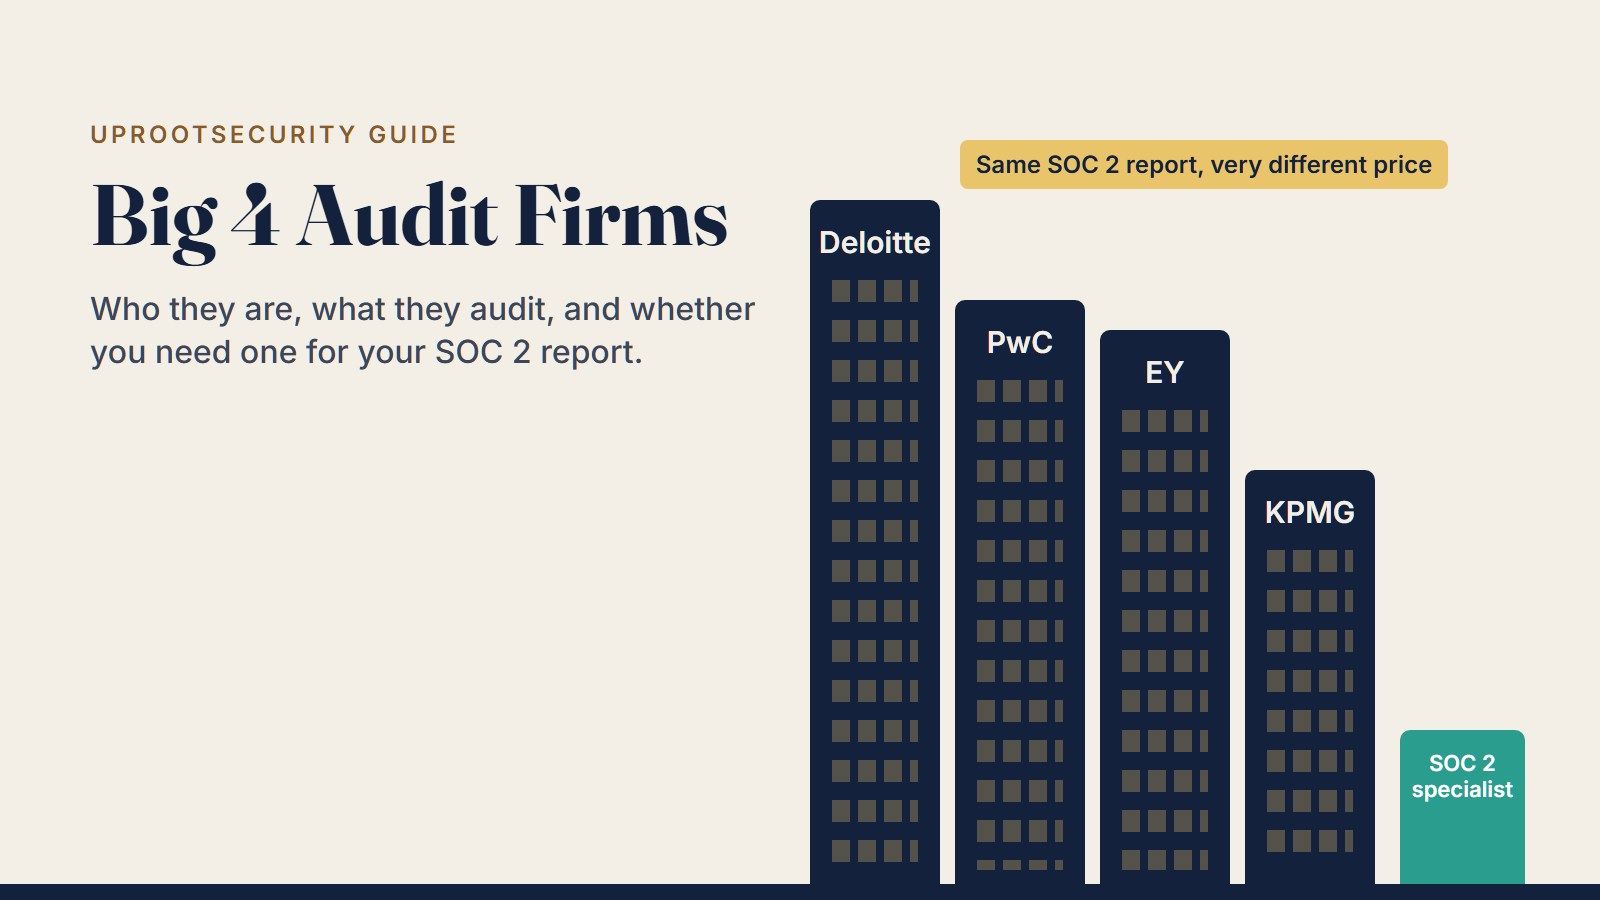
The Big 4 audit firms are Deloitte, PwC, EY and KPMG, the four largest accounting and audit networks in the world by revenue.
Together they audit about 90% of the largest US public companies. Many founders first hear about them when a customer asks for a SOC 2 report and someone asks, "Should we use a Big 4 firm?" This guide covers who the Big 4 are, what they do, and when a Big 4 name is worth paying for in a SOC 2 audit.
Reviewed by Riya Ann Varghese, GRC Engineer, ISO 27001 lead auditor certified. Last updated October 27, 2026.
Who Are the Big 4 Audit Firms?
The Big 4 audit firms are Deloitte, PricewaterhouseCoopers (PwC), Ernst & Young (EY) and KPMG, global networks of member firms that sell audit, tax and advisory services.
| Firm | Latest global revenue | Year ended | Origin |
|---|---|---|---|
| Deloitte | $74.5 billion | May 31, 2026 | Founded in London in 1845 |
| PwC | $60.2 billion | June 30, 2026 | 1998 merger of Price Waterhouse and Coopers & Lybrand |
| EY | $57.0 billion | June 30, 2026 | 1989 merger of Ernst & Whinney and Arthur Young |
| KPMG | $39.8 billion | September 30, 2025 | 1987 merger that formed today's network; named after its founders Klynveld, Peat, Marwick and Goerdeler |
Revenue figures come from each firm's own annual announcement. The firms close their years in different months, and KPMG reports its 2026 results in December, so its figure is a year older.
Each "firm" is really a network. Deloitte US, Deloitte UK and Deloitte India are separate legal partnerships that share a brand, methods and quality rules. When you sign an audit engagement, you sign with your local member firm.
Which Big 4 Firm Is Number 1?
Deloitte is the largest Big 4 firm by revenue, followed by PwC, EY and KPMG.
"Best" depends on what you need. Each firm has stronger teams in some industries and countries than others. For an audit, the partner and team assigned to you matter more than the logo on the report.
What Do the Big 4 Audit Firms Do?
The Big 4 audit firms sell four main kinds of services: audit and assurance, tax, consulting, and risk advisory.
| Service line | What it covers |
|---|---|
| Audit and assurance | Financial statement audits, internal control audits for public companies, and attestation reports such as SOC 1 and SOC 2 |
| Tax | Corporate and international tax planning, filings and tax disputes |
| Consulting | Strategy, technology, AI and transformation projects |
| Risk and cyber advisory | Risk programs, cybersecurity, regulatory compliance and readiness work |
One rule shapes how these services mix. Independence rules stop a firm from auditing work it designed or runs for the same client. So a Big 4 firm that builds your controls cannot also audit them.
How Much of the Audit Market Do the Big 4 Control?
The Big 4 audit about half of all SEC-registered companies and about 90% of the largest ones.
The 2026 "Who Audits Public Companies?" report from Ideagen Audit Analytics puts Deloitte at 15%, EY at 13%, PwC at 12% and KPMG at 11% of the non-SPAC SEC market. For large accelerated filers, the biggest public companies, the Big 4 share is about 90%.
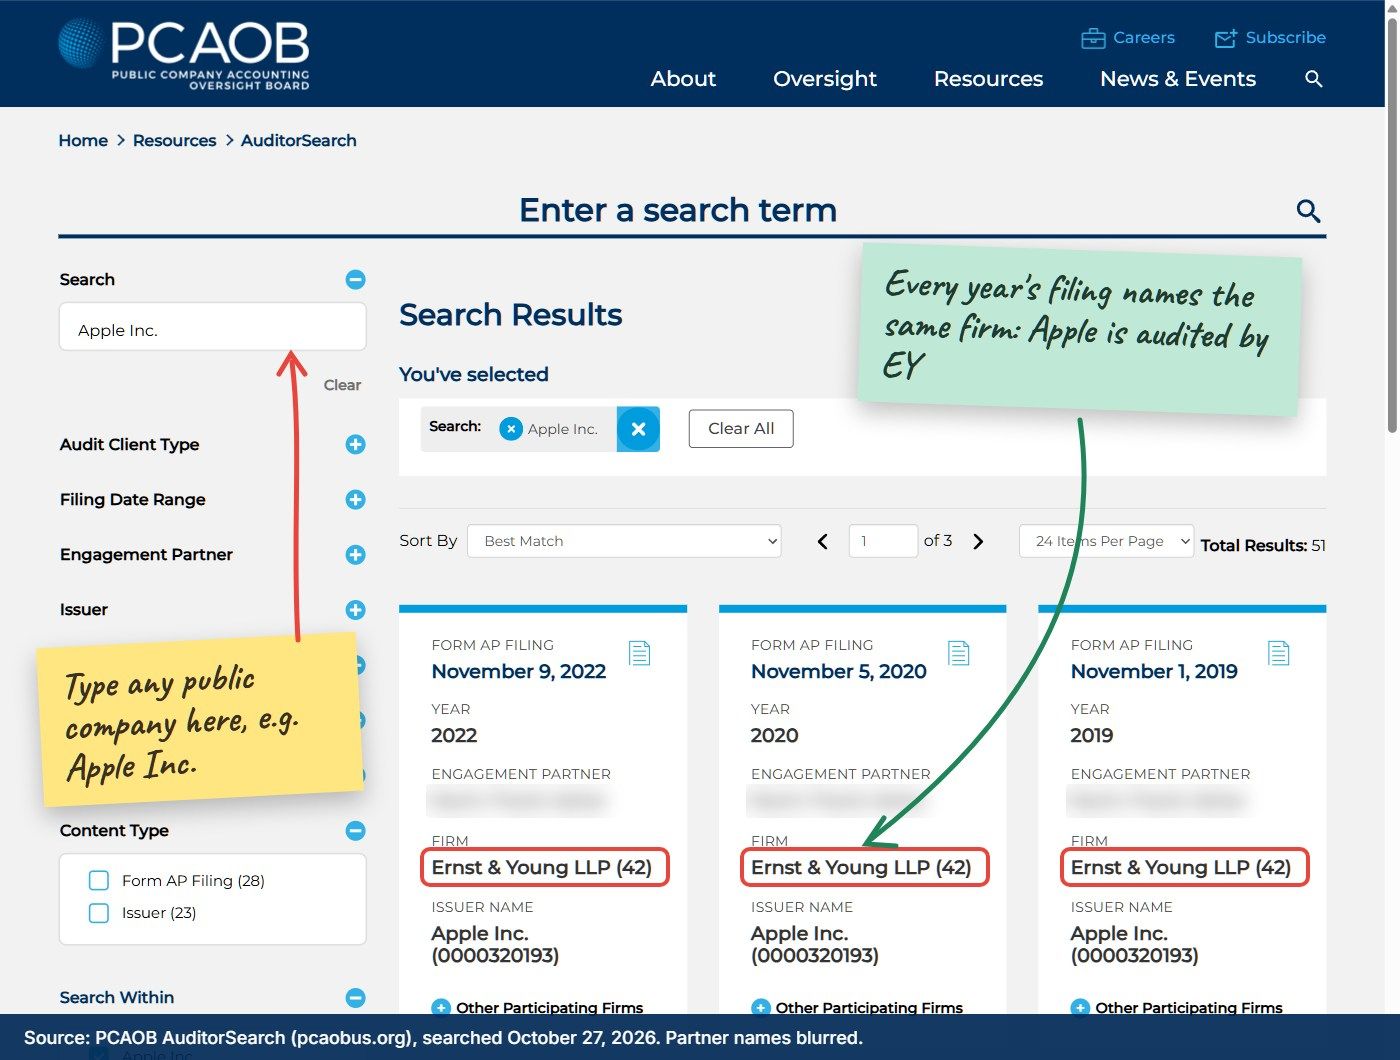
You can check who audits any US public company in the PCAOB's free AuditorSearch tool. Every audit of a public company files a Form AP that names the audit firm and the lead partner. For example, Apple's Form AP filings show Ernst & Young LLP as its auditor.
Do the Big 4 Do SOC 2 Audits?
Yes, all four Big 4 firms perform SOC 2 audits, but most startups and mid-size SaaS companies get their SOC 2 report from a specialist or mid-tier CPA firm instead.
A SOC 2 report must come from a licensed CPA firm, and every Big 4 firm qualifies. The reasons smaller companies usually look elsewhere are practical:
- Cost. Big 4 SOC 2 engagements are estimated at $65,000 to $200,000, several times what a specialist firm charges for a similar scope.
- Fit. Big 4 SOC teams are built around large, multi-region companies. A 30-person SaaS company is a small client for them.
- Team experience. The partner on the sales call is rarely the person testing your controls. Ask how many SOC 2 audits the assigned team has done.
- Independence. If a Big 4 firm already does consulting or readiness work for you, it may not be able to audit you.
Big 4 vs Mid-Tier vs Specialist Firms for SOC 2
Big 4, mid-tier and specialist firms can all issue the same SOC 2 report, but they differ in cost, speed and the kind of client they serve best.
| Firm type | Examples | Estimated SOC 2 cost | Best fit | Watch out for |
|---|---|---|---|---|
| Big 4 | Deloitte, PwC, EY, KPMG | $65,000 to $200,000 | Large public or global companies, or a customer that requires a Big 4 name | Price, slower scheduling, independence conflicts with existing consulting |
| Mid-tier (full-service CPA) | BDO, Grant Thornton, RSM, Baker Tilly, Crowe | $30,000 to $80,000 | Mid-market companies that also need a financial audit or tax work | SOC 2 may be one service among many, so check team experience |
| Specialist SOC 2 firm | See our list of best SOC 2 auditors | $15,000 to $50,000 | Startups and SaaS companies that need SOC 2, ISO 27001 or HIPAA | Less brand recognition outside security teams |
These ranges are estimates from soc2auditors.org and depend on scope. A small company with a focused, Security-only scope can pay about $5,000 to $20,000 for a SOC 2 Type 2 audit. For a full breakdown, see how much a SOC 2 audit costs.
When Does a Big 4 SOC 2 Report Make Sense?
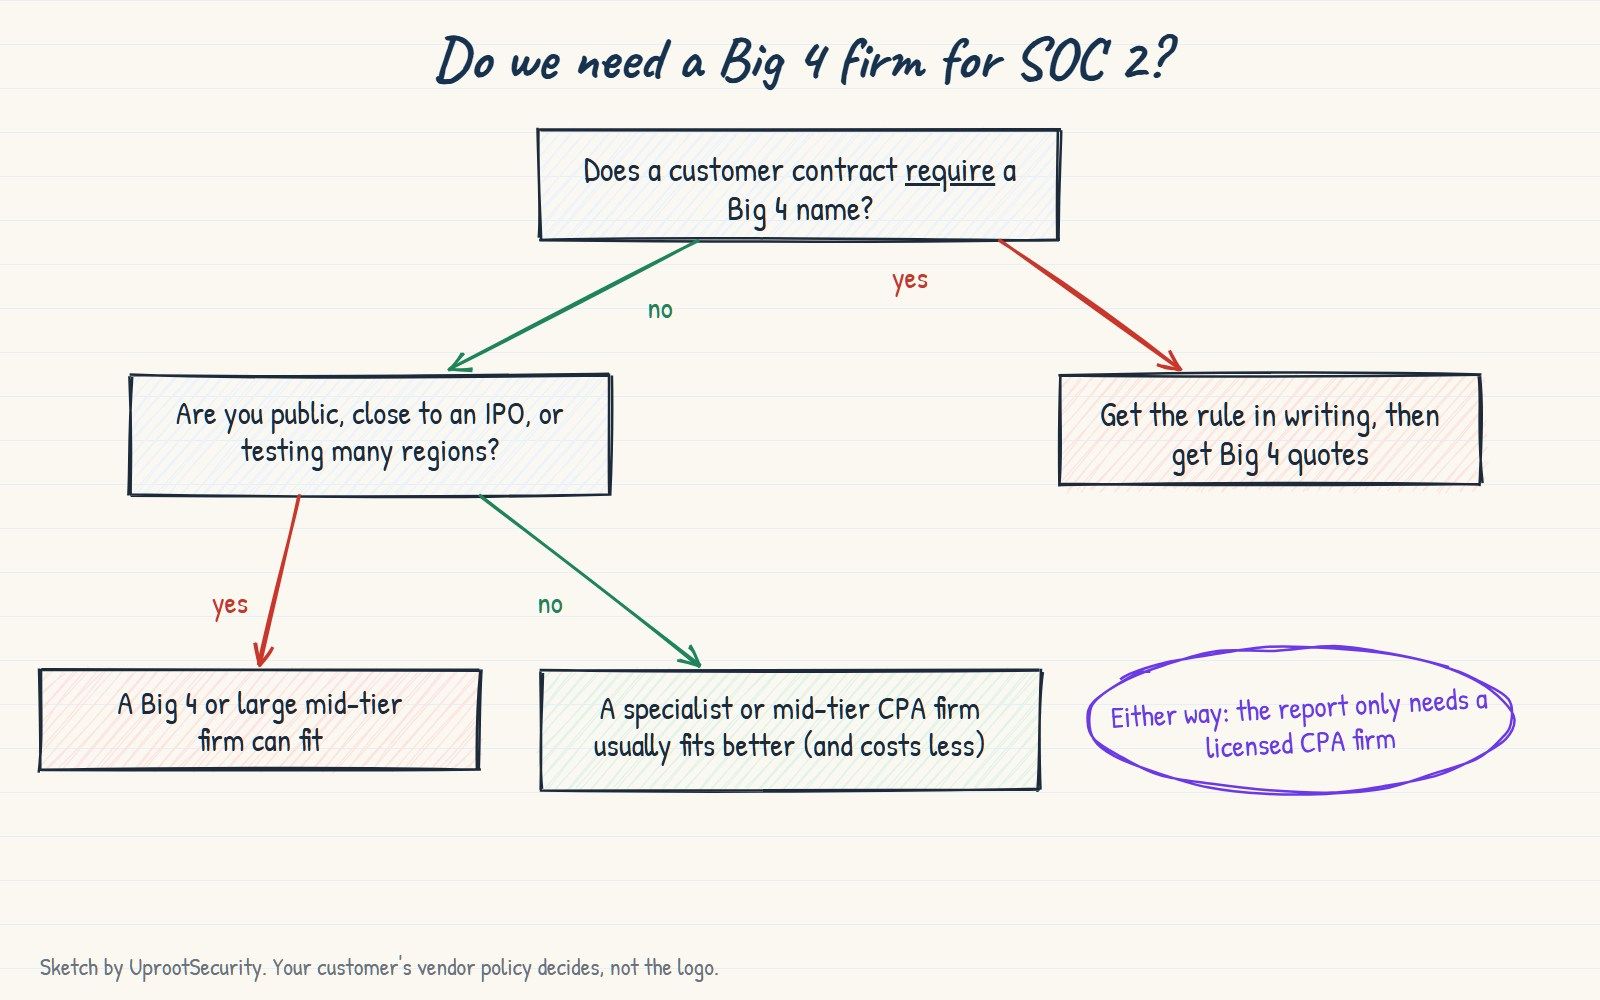
A Big 4 SOC 2 report makes sense when a customer contract names a Big 4 firm, or when your company is large, public and global enough that a Big 4 firm already fits.
- A customer requires it. A few large buyers write a Big 4 name into their vendor policy. Ask for that rule in writing before you pay for it.
- You are public or close to an IPO and want one firm across your financial audit and SOC reports.
- Your scope is global, with many regions, data centers or business units to test.
Outside these cases, the logo rarely changes a deal. Procurement teams check that the report is current, covers the right systems, and has a clean opinion.
Does a SOC 2 Report Need to Come From a Big 4 Firm?
No, a SOC 2 report does not need to come from a Big 4 firm, as long as a licensed CPA firm issues it.
The AICPA does not rank firms by size. Customers read the auditor's opinion, the scope and any exceptions, not the brand. To check a firm before you sign, see our list of SOC 2 auditors for startups.
Not sure which auditor fits your SOC 2? Talk to a compliance expert. We help you scope the audit and introduce you to firms that fit your size and budget.
What Are the Alternatives to the Big 4 Audit Firms?
The main alternatives to the Big 4 are mid-tier audit firms, often called Tier 2 firms, and specialist firms that focus on one type of audit.
Tier 2 firms are large national and international networks just below the Big 4 in size. They usually offer more partner time and lower fees.
- BDO: a global network that focuses on mid-market and growing companies.
- Grant Thornton: yes, Grant Thornton is a mid-tier firm, one of the largest outside the Big 4.
- RSM: a large network known for middle-market audit, tax and consulting.
- Baker Tilly: yes, Baker Tilly is a mid-tier firm, with a large US practice.
- Crowe: a global network with strong financial services and healthcare practices.
Many of these firms issue SOC 2 reports. Specialist SOC 2 firms go further and focus almost only on security and compliance audits, which suits SaaS companies that need SOC 2, ISO 27001 and HIPAA from one auditor.
From the Big 8 to the Big 4: A Short History
The Big 4 formed through mergers and one collapse, shrinking from eight large firms in the 1980s to four by 2002.
- 1980s: the "Big 8" firms dominate auditing.
- 1989: two mergers create Ernst & Young and Deloitte & Touche, leaving the Big 6.
- 1998: Price Waterhouse and Coopers & Lybrand merge into PricewaterhouseCoopers, leaving the Big 5.
- 2002: Arthur Andersen collapses after the Enron scandal, leaving the Big 4.
Enron also led to the Sarbanes-Oxley Act and the PCAOB, which now inspects the audit firms that audit US public companies.
How We Wrote This Guide
We read the top-ranking Big 4 guides, the questions people ask Google and AI tools about the Big 4 and SOC 2, and the audits we prepare our customers for. Revenue figures come from each firm's own announcement, market share from Ideagen Audit Analytics, and auditor data from the PCAOB. A GRC engineer reviewed every section.
How UprootSecurity Helps You Get SOC 2 Without a Big 4 Price
UprootSecurity is a compliance platform that gets you ready for your SOC 2 audit, then introduces you to independent CPA firms that fit your size and budget. We do not perform the audit ourselves, so your auditor stays independent.
Most companies do not need a famous auditor. They need a clean report, on time, that answers the customer's security questions. That depends on how well you prepare.
| What your customer or auditor asks for | How UprootSecurity delivers it |
|---|---|
| A SOC 2 report from a trusted firm | Introductions to independent audit firms that match your size, scope and budget |
| A clear audit scope | A dedicated compliance expert who scopes the audit with you |
| Evidence that controls worked all period | Continuous monitoring across 140+ integrations, with dated evidence |
| A penetration test report | A yearly pentest included in your plan |
| ISO 27001 or HIPAA next | 22 frameworks from one set of controls |
| Fewer security questionnaires | Trust center and questionnaire automation on Growth and Enterprise plans |
See our SOC 2 for startups guide for the full plan, or how continuous monitoring works.
Is a SOC 2 audit quote bigger than your budget? → Book a demo today
Frequently Asked Questions
The Big 4 audit firms are Deloitte, PwC, EY and KPMG. They are the four largest accounting and audit networks in the world and audit about 90% of the largest US public companies. Each operates as a network of separate member firms that share one brand and set of quality standards.
Deloitte is the biggest Big 4 firm, with $74.5 billion in global revenue for the year ended May 2026. PwC is second at $60.2 billion, EY third at $57.0 billion, and KPMG fourth at $39.8 billion for the year ended September 2025.
It is the Big 4 today. There was a Big 5 until 2002, when Arthur Andersen collapsed after the Enron scandal. Before that, mergers had already shrunk the Big 8 of the 1980s to the Big 6 in 1989 and the Big 5 in 1998.
No, JPMorgan Chase is not in the Big 4. It is a bank, not an accounting firm. The Big 4 are Deloitte, PwC, EY and KPMG. People sometimes mix up the Big 4 accounting firms with the largest banks or with the Big 3 consulting firms, McKinsey, BCG and Bain.
Audit regulators check the Big 4's work. In the US, the PCAOB inspects the audits these firms perform for public companies, and in the UK the Financial Reporting Council does the same. The US firms are private partnerships, so they do not publish audited financial statements the way public companies do.
Yes, Deloitte, PwC, EY and KPMG all perform SOC 2 audits. They mostly serve large, public and global companies. Most startups and mid-size SaaS companies use specialist or mid-tier CPA firms, which cost less and focus more on SOC 2 work.
A Big 4 SOC 2 audit is estimated at $65,000 to $200,000, depending on scope. Specialist firms are estimated at $15,000 to $50,000 and mid-tier firms at $30,000 to $80,000. A small company with a focused scope can pay about $5,000 to $20,000.
No, a SOC 2 report only needs to come from a licensed CPA firm. The AICPA does not rank firms by size, and most customers accept a report from any licensed firm. A Big 4 name matters only if a customer's vendor policy specifically requires one.
Only a licensed CPA firm can perform a SOC 2 Type 2 audit and issue the report. A non-CPA firm can help you prepare, but it cannot sign the report. The firm that audits you must be independent, so it cannot also have built your controls.
Tier 2 audit firms are large accounting networks just below the Big 4 in size, such as BDO, Grant Thornton, RSM, Baker Tilly and Crowe. They usually charge less than the Big 4, give more partner attention, and many of them perform SOC 2 audits for mid-market companies.
Sources
- Deloitte FY2026 global revenue announcement: https://www.deloitte.com/global/en/about/press-room/global-revenue-announcement.html
- PwC FY26 global financial performance: https://www.pwc.com/gx/en/news-room/press-releases/2026/pwc-announces-fy26-global-financial-performance.html
- EY FY2026 global revenue: https://www.ey.com/en_gl/newsroom/2026/10/ey-global-revenue-increases-4-point-7-percent-to-us-dollars-57b-for-fiscal-year-2026
- KPMG FY25 global revenue: https://kpmg.com/kw/en/media/2025/12/kpmg-delivers-rise-in-global-revenue.html
- Ideagen Audit Analytics, Who Audits Public Companies 2026 (summary): https://www.thecorporatecounsel.net/blog/2026/04/who-audits-public-companies.html
- PCAOB AuditorSearch: https://pcaobus.org/resources/auditorsearch
- SOC 2 audit cost estimates by firm type: https://soc2auditors.org
- UprootSecurity pricing page (SOC 2 Type 2 audit fee range): https://www.uprootsecurity.com/pricing