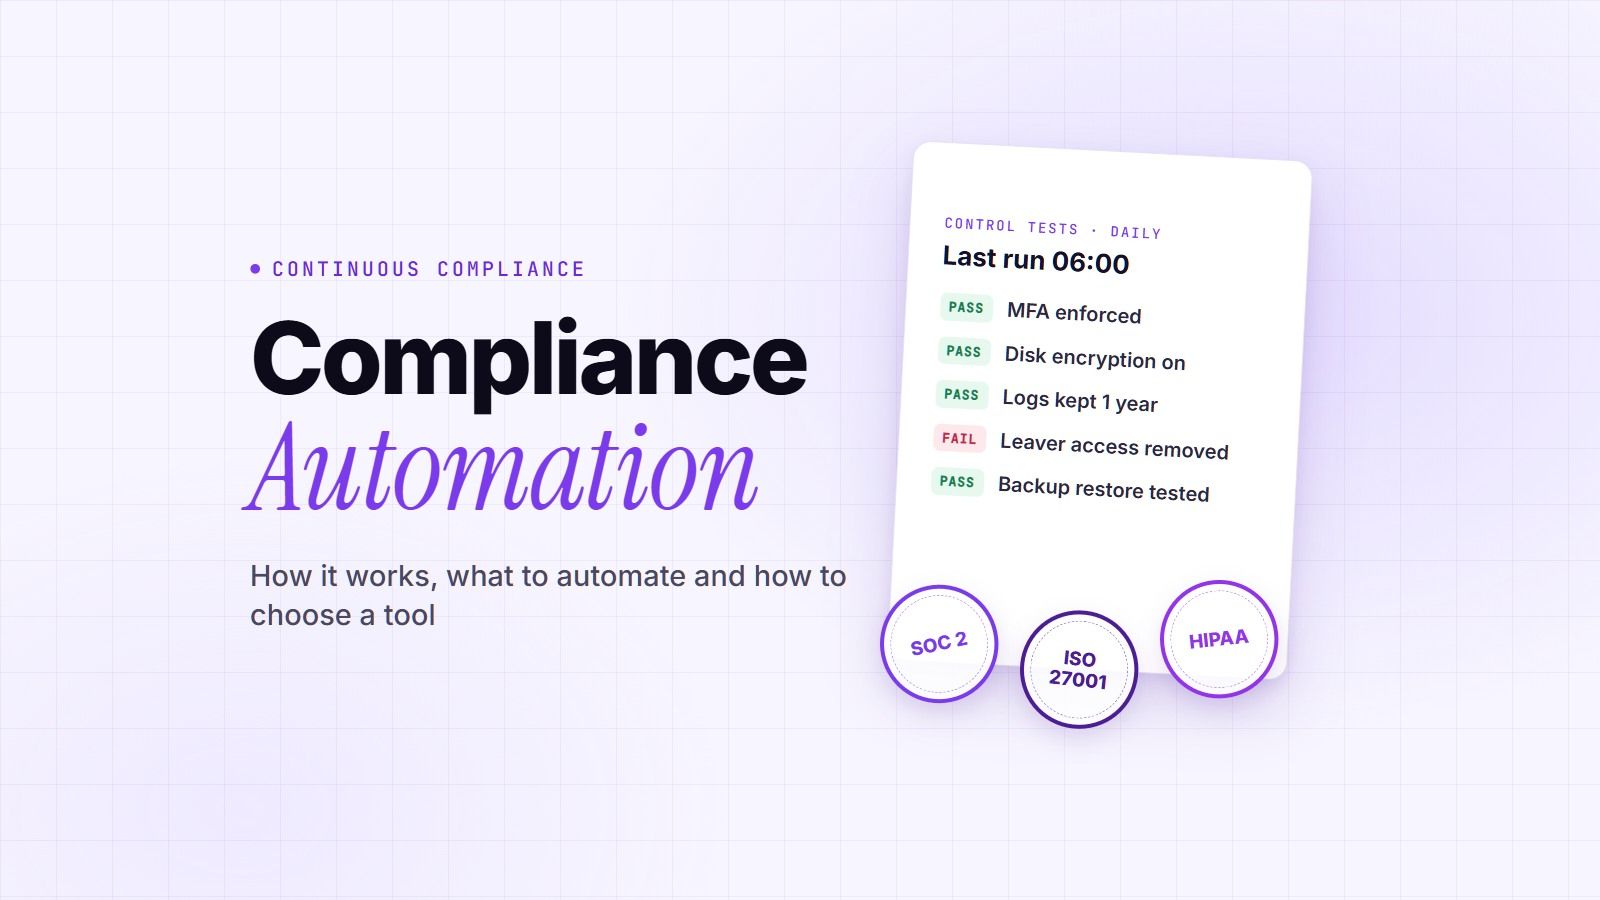
Compliance automation uses software to collect evidence, test controls and flag gaps across your systems continuously, instead of by hand before each audit.
For a company working toward SOC 2, ISO 27001, HIPAA or PCI DSS, that means fewer screenshots and spreadsheets, fewer surprises in the audit, and one set of controls that counts for several frameworks. This guide explains how automated compliance works, what you can and can't automate, what auditors think of automated evidence, and how to choose a compliance automation platform.
Reviewed by Riya Ann Varghese, GRC Engineer, ISO 27001 lead auditor certified. Last updated: November 9, 2026.
What Is Compliance Automation?
Compliance automation is software that connects to your systems and keeps checking them against the controls your frameworks require.
Instead of someone collecting screenshots before an audit, the platform pulls settings and records from your cloud, identity provider, HR system and code repositories. It tests them against each control, keeps the results as evidence, and alerts the right person when something drifts. Security compliance automation is the same idea applied to security frameworks such as SOC 2 and ISO 27001. If you also need enterprise risk and governance workflows, see our guide to GRC automation.
How Does Compliance Automation Work?
Compliance automation works in four steps: connect your systems, test controls, map evidence to each framework, then alert owners and track fixes.
| Step | What happens | Example |
|---|---|---|
| 1. Connect | The platform links to your cloud, identity, HR, code and ticketing tools through integrations | Read-only access to AWS, Okta, GitHub, your HR system |
| 2. Test | Automated tests check each control, often daily or hourly | "Is MFA on for every user?" "Is this database encrypted?" |
| 3. Map | Each result is saved as evidence and mapped to every framework that needs it | One MFA test counts for SOC 2, ISO 27001, HIPAA and PCI DSS |
| 4. Alert and fix | Failures go to the control owner, with a ticket and a record of the fix | A former employee still has access, so IT gets a task to remove it |
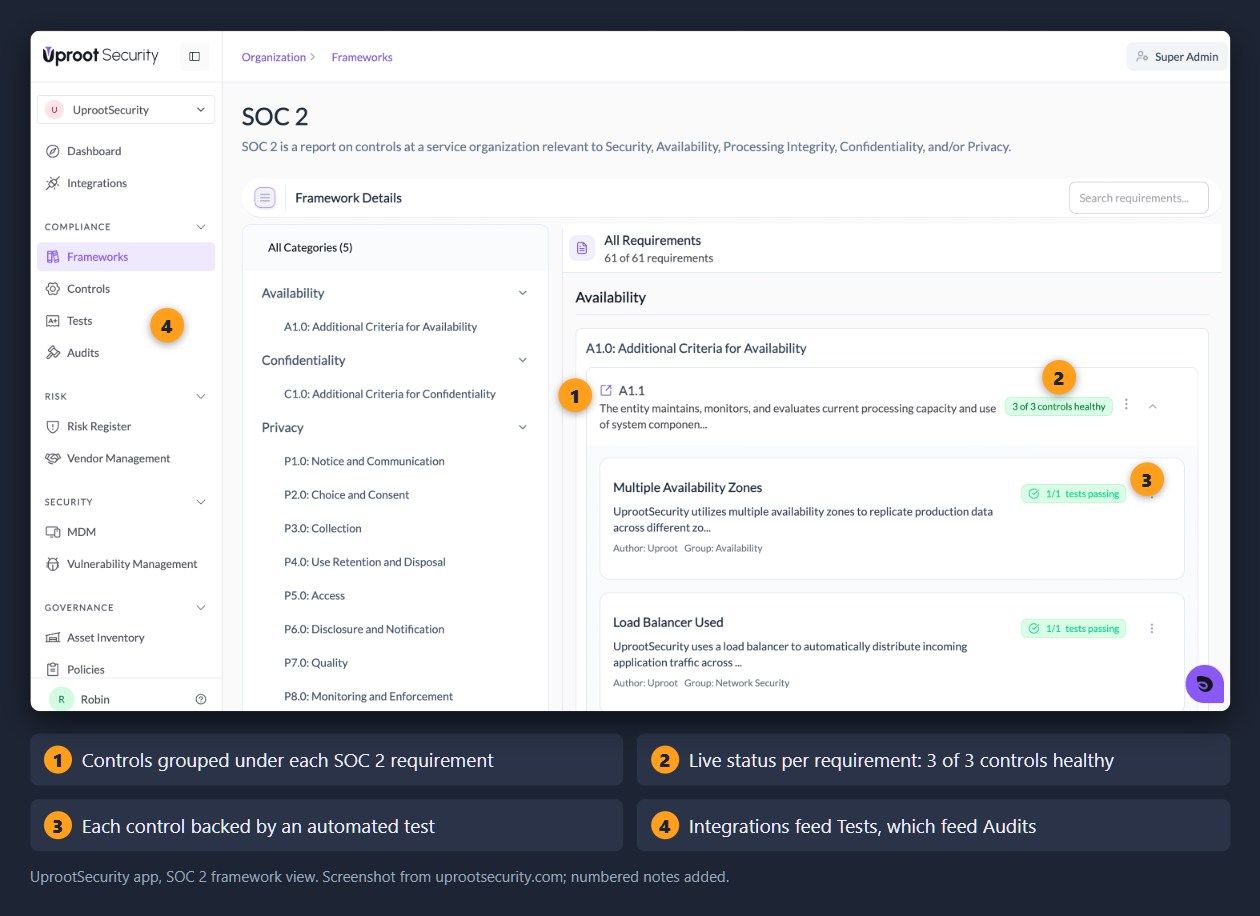
This is what continuous compliance monitoring means in practice. Recurring control testing runs on its own, so a skipped access review or a new unencrypted bucket shows up in days, not at audit time.
What Can (and Can't) You Automate in Compliance?
You can automate most evidence collection and technical checks, part of the paperwork, and none of the judgment calls.
| Automate fully | Automate partly | Still needs a person |
|---|---|---|
| MFA and password settings | Policies (templates, approvals, staff sign-off) | Deciding scope and which frameworks to pursue |
| Encryption and cloud configuration checks | Vendor reviews (tracking, reminders, document collection) | Risk decisions and accepting risk |
| Onboarding and offboarding checks | Risk assessment (scoring, register upkeep) | Reviewing vendor reports and judging them |
| Log retention and alerting checks | Security questionnaires (answer libraries) | Talking to the auditor and explaining exceptions |
| Training completion and background check tracking | Access reviews (lists and reminders; a manager still approves) | Fixing the actual problem a test finds |
AI is speeding up the middle column, for example drafting policies and answering questionnaires; our guide to AI agents for compliance covers where it helps. Security compliance automation still stops short of judgment calls.
So can compliance be fully automated? No. Automation removes the repetitive collecting and checking, which is most of the hours, but a person still owns every control and every decision. For a side-by-side of effort and cost, see our guide to manual vs automated compliance.
One Control, Four Frameworks: How Mapping Saves Work
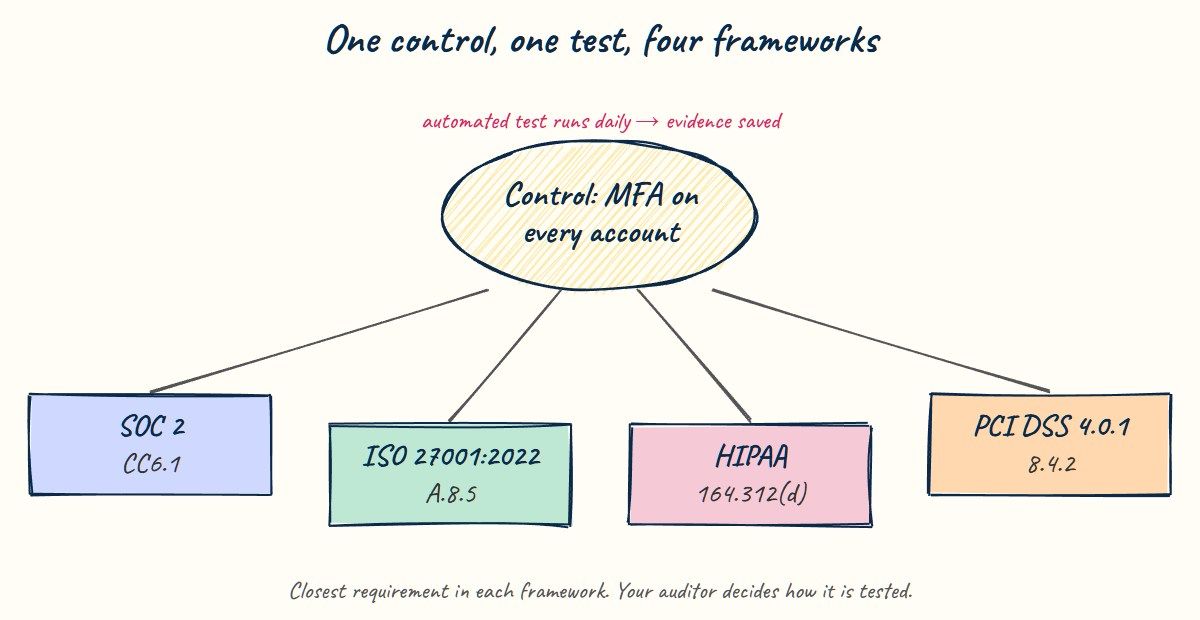
Cross-framework mapping means one control and one piece of evidence count toward every framework that asks for it.
This is where automated compliance saves the most time for companies adding a second or third framework. Here is how four common controls map:
| Control | SOC 2 | ISO 27001:2022 | HIPAA Security Rule | PCI DSS v4.0.1 |
|---|---|---|---|---|
| Multi-factor authentication | CC6.1 | A.8.5 Secure authentication | 164.312(d) Person or entity authentication | 8.4.2 MFA for access into the cardholder data environment |
| Encryption of stored data | CC6.1 | A.8.24 Use of cryptography | 164.312(a)(2)(iv) Encryption and decryption (addressable) | 3.5.1 Stored card numbers made unreadable |
| User access reviews | CC6.2, CC6.3 | A.5.18 Access rights | 164.308(a)(4) Information access management | 7.2.4 Review user accounts every six months |
| Audit logging | CC7.2 | A.8.15 Logging | 164.312(b) Audit controls | 10.2.1 Audit logs enabled |
Adding a second framework soon? Talk to a compliance expert about which of your SOC 2 controls already count for ISO 27001 or HIPAA.
Do Auditors Accept Automated Evidence?
Yes, auditors accept automated evidence, but they still check that system-generated reports are complete and accurate before relying on them.
Audit standards treat this as "information produced by the company." For example, PCAOB AS 1105 says auditors should test the accuracy and completeness of such information, or the controls over it. In a SOC 2 audit, that usually means the auditor asks how a report was generated, checks a sample against the source system, and may ask for a screen share.
Automation helps here because every test result is timestamped and tied to its source. It does not remove the auditor's own testing, and a good platform makes it easy to show where each piece of evidence came from.
How to Automate Compliance: 5 Steps
To automate compliance, map your current controls, pick your frameworks, connect a platform, automate evidence collection, then review coverage every quarter.
- Review where you stand. List the frameworks you need, your current controls, and which tasks eat the most hours today.
- Set scope and goals. Start with one framework and the systems in scope, for example SOC 2 for your production cloud.
- Connect your systems. Integrate cloud, identity, HR, code and ticketing tools first, since they hold most of the evidence.
- Automate evidence collection and tests. Turn on control tests, assign an owner to every control, and route alerts to those owners.
- Review and expand. Each quarter, check which controls are still manual, add new systems, and map your next framework. Continuous compliance monitoring only works if coverage keeps up with your stack.
Many teams pair this with a SOC 2 compliance checklist so nothing is missed in the first audit.
What to Look For in a Compliance Automation Platform
The best compliance automation platform connects deeply to your stack and includes enough expert help to get you through the audit.
| What to check | Question to ask the vendor |
|---|---|
| Integration depth | Do you test settings in our cloud and identity provider, or only pull lists? |
| Test frequency | How often do control tests run, and what triggers an alert? |
| Cross-framework mapping | Will our SOC 2 evidence count for ISO 27001 or HIPAA without rework? |
| Evidence quality | Can the auditor see where each piece of evidence came from and when? |
| Remediation workflow | Do failures create tickets with owners and deadlines? |
| Expert help | Who helps us scope, write policies and talk to the auditor? |
| Total cost | What do the audit, pentest and extra frameworks cost on top of the platform? |
Compliance Automation Tools to Consider
Compliance automation tools differ mostly in how much expert help they include, how many frameworks they cover and who they are built for.
Disclosure: we make UprootSecurity, so we list it first. Each tradeoff below is our honest read, and the names link to our full reviews where we have one.
| Tool | Best for | Tradeoff to weigh |
|---|---|---|
| UprootSecurity | Startups and scaleups that want a dedicated compliance expert, automation and a yearly pentest in one plan | A younger brand than the biggest platforms, with a smaller review base |
| Vanta | Teams that want a large integration library and a well-known name | Audit and pentest are usually extra; pricing rises with frameworks and headcount |
| Drata | Larger companies wanting deep customization | Can be more platform than a small team needs |
| Secureframe | Companies wanting guided setup across several frameworks | Audit is not included; check what support level each plan has |
| Sprinto | Cost-conscious teams pursuing SOC 2 or ISO 27001 | Check support hours and auditor coordination for your region |
| Hyperproof | Mid-size and larger compliance teams running many frameworks | Built for dedicated compliance teams more than founders |
For a longer comparison with pricing notes, see our list of SOC 2 compliance vendors.
What Are the Benefits of Compliance Automation?
The main benefits of compliance automation are less manual work, faster audits, fewer missed controls and easier expansion to new frameworks.
- Less manual work: evidence is collected for you, so engineers stop taking screenshots.
- Faster audits: evidence is ready and organized when fieldwork starts.
- Fewer exceptions: drift is caught between audits, not by the auditor.
- Easier growth: controls you already run count toward the next framework.
How UprootSecurity Automates Compliance
UprootSecurity pairs continuous monitoring with a dedicated compliance expert, so automation handles the evidence and a person handles the judgment.
| What you need | How UprootSecurity delivers it |
|---|---|
| Evidence collected without screenshots | Continuous monitoring across 140+ integrations |
| One program for several frameworks | 22 frameworks mapped to one set of controls |
| Someone to own scope, policies and the auditor | A dedicated compliance expert |
| Annual penetration test | A yearly penetration test included |
| Answering customer security reviews | Trust center and questionnaire automation on Growth and Enterprise plans |
Tired of collecting audit evidence by hand? → Book a demo today
Frequently Asked Questions
Compliance automation is software that connects to your cloud, identity, HR and code systems and checks them against your framework's controls. It runs tests on a schedule, saves the results as evidence, maps them to each framework, and alerts the control owner when something fails, so you stay audit-ready between audits.
The best compliance automation software depends on your stack, frameworks and how much help you need. Startups often want a platform with a compliance expert included, while larger teams may want deep customization. Compare integration depth, cross-framework mapping, evidence quality, support and total cost, including audit and pentest fees.
No, compliance cannot be fully automated. Software can collect most evidence and run technical checks, but people still decide scope, accept risks, review vendors, fix failing controls and work with the auditor. The best results come from automation for repetitive checks plus a clear owner for every control.
No, AI is not replacing compliance, but it is taking over repetitive tasks such as drafting policies, answering questionnaires and summarizing evidence. Auditors and customers still expect people to own controls and decisions. AI agents work best as assistants inside a compliance program, not as its owner.
A common example is offboarding. When an employee leaves, the HR system marks them inactive, the compliance platform checks every connected tool, and it flags any account still active. The IT owner gets a task, removes access, and the platform saves the record as evidence for SOC 2 and ISO 27001.
Yes, auditors accept automated evidence, but they test that system-generated information is complete and accurate before relying on it. Expect them to ask how a report was produced and to compare samples with the source system. Timestamped evidence tied to its source makes that check quick.
Compliance automation tools run control tests on a schedule, often daily or hourly, and log every result with a timestamp. Recurring tasks such as quarterly access reviews get reminders and an audit trail. This gives auditors proof that controls worked across the whole period, which a SOC 2 Type 2 report requires.
Connecting your main systems to a compliance automation platform usually takes days to a few weeks. Closing the gaps it finds, writing policies and running controls long enough for an audit takes longer, often a few months before a first SOC 2 Type 1 or the start of a Type 2 window.
Compliance automation is usually worth it for a startup that needs SOC 2 or ISO 27001 to close deals, because engineer time is expensive and manual evidence collection repeats every year. It matters most once you plan a Type 2 report or a second framework. Very small, one-off efforts may manage with spreadsheets.
Compliance automation focuses on collecting evidence and testing controls for frameworks like SOC 2 and ISO 27001. GRC software is broader and also covers enterprise risk management, policies, internal audit and governance reporting. Many modern platforms do both, but GRC tools usually target larger companies with dedicated risk teams.