Continuous compliance monitoring, a dedicated compliance expert and audit-ready evidence in one platform, so passing the audit actually means something.
Compliance frameworks covered: SOC 2 · ISO 27001 · ISO 42001 · HIPAA · GDPR · PCI DSS v4.0.1 · NIST CSF 2.0 · DORA · and 14 more
Themes from Drata's own pricing page and verified reviews on G2.
Plans are tiered with no public prices. The entry plan is capped at 50 employees, and extra frameworks cost more.
You get a custom quote up front, with pentesting included in the plan.
Reviewers say setup and mapping controls across frameworks take time, and alerts get noisy until tuned.
A dedicated compliance expert maps controls and tunes alerts with you, so week one is review.
Some reviewers say niche or legacy systems need manual workarounds.
With 140+ integrations and a dedicated compliance expert, the gaps a connector can't reach are handled with you, not left to you.
Where we overlap, and where we go further.
| Capability |  UprootSecurity | Drata |
|---|---|---|
| Continuous control monitoring across cloud and identity | Yes | Yes |
| Auditor collaboration workspace | Yes | Yes, Audit Hub |
| Policy templates and acceptance tracking | Yes | Yes |
| MCP server that can never delete your records | Yes, no delete access | Limited, can delete evidence, risks and vendors |
| Penetration testing included in the plan | Included | Limited, partner credits only |
| Trust center in the same plan as compliance | Yes, Growth and Enterprise | Limited, separate Trust Center plan |
| Signed evidence you can verify offline | Yes, sha256 + ed25519 | Limited, not publicly documented |
| Log of every file your auditor viewed | Yes | Limited, not publicly documented |
"Limited" means narrower, sold separately, or not publicly documented, per Drata's pages and reviews, November 2026. Where Drata is ahead: more frameworks (30+ pre-built vs 22), more integrations (hundreds vs 140+), and G2 support (9.6/10).
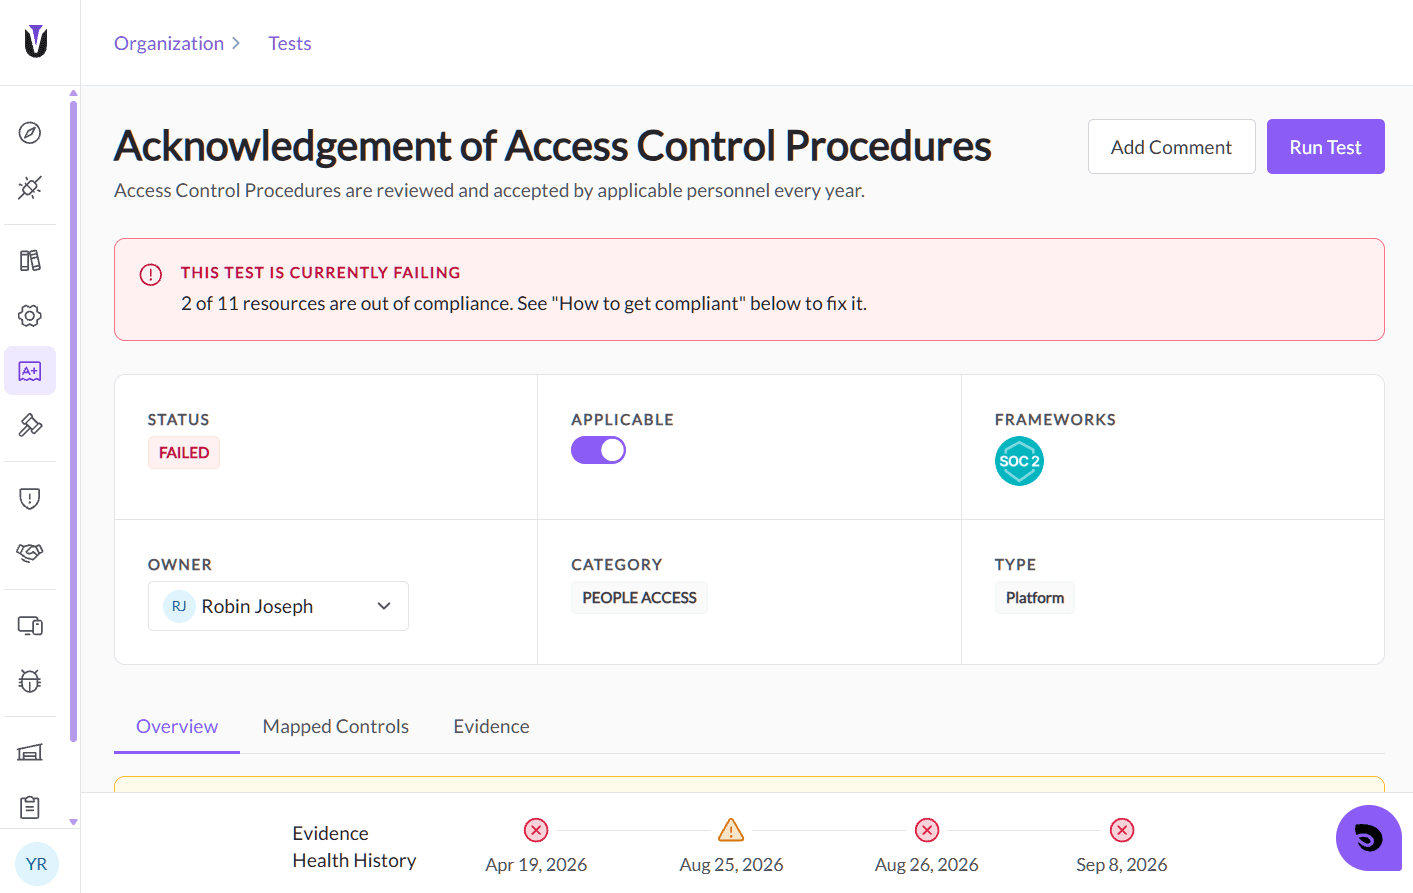
Every artifact is fingerprinted on arrival and sealed, so you can prove it hasn't changed, offline.
sha256 + ed25519 signature, write-once storage
Stale evidence re-pulls before your auditor sees it
Export the full library, any time
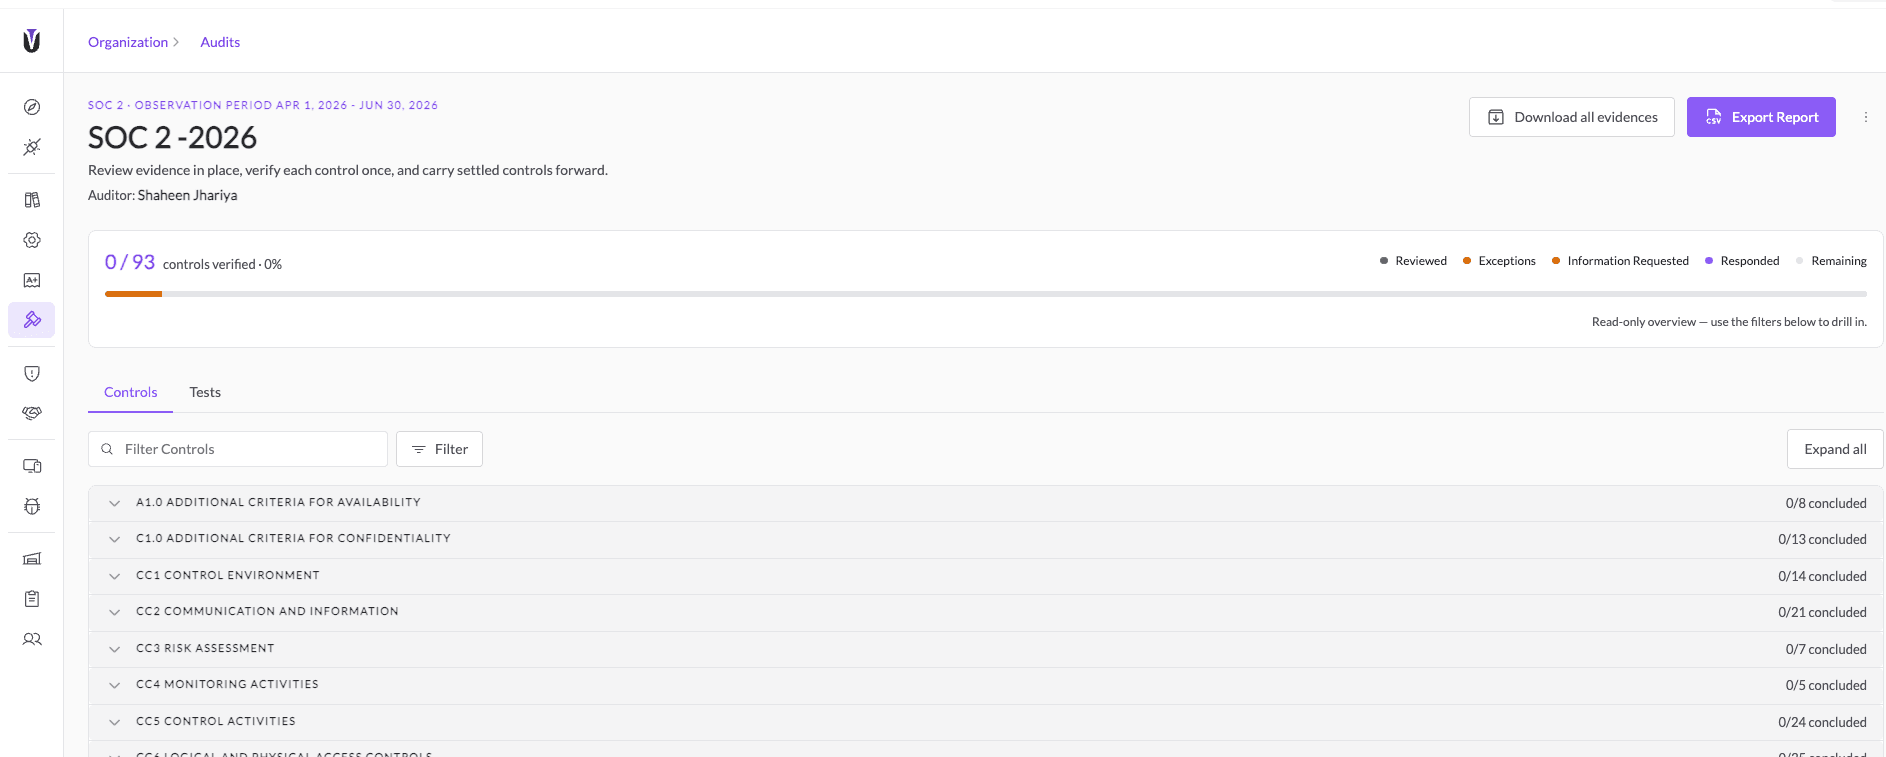
Scoped, read-only, time-boxed access. Every view is recorded.
One-click revoke, SSO enforced
No email attachments
3 days median fieldwork
Let Claude Code or Cursor triage tests and file evidence, within published limits.
Writes need Owner or Admin
Cannot delete tests, policies, vendors or risks
Cannot reach another org or user
1,247 tests across cloud, identity, code and vendors, most every 15 minutes.
Alerts to PagerDuty and Slack, with a fix attached
Fixes as Terraform or IAM JSON
86% of drift auto-resolved, 14-min median
Decisions an auditor needs a name behind stay with a person.
Approving and publishing a policy
Accepting and scoring a risk
Assigning a vendor's risk tier
Answering a vendor questionnaire
Completing a vendor review
Deciding what enters the risk register
SOC 2 and ISO 27001 should be byproducts of being secure, not the product you bought.
Continuous risk monitoring and vendor breach alerts cost extra, on top of the platform
Controls get checked once a year, on a date in a contract
Gaps arrive as a PDF that someone has to translate into tickets
The dashboard is green while a real gap is still open
You pass the audit and still don't know if you'd survive an attacker
Drift is caught and fixed automatically, inside the platform you already pay for
1,247 checks running continuously, not once a year
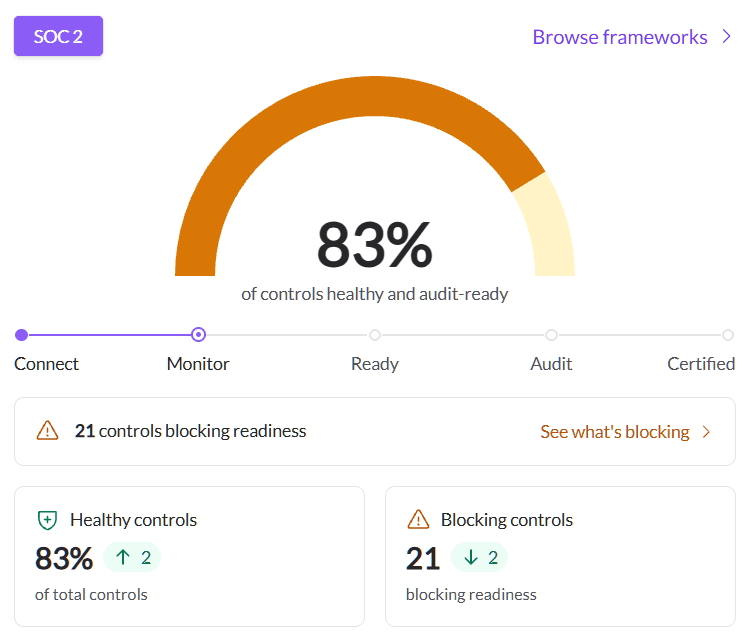
Failing controls arrive with an owner and a fix attached
Every one of those checks is also your signed evidence for SOC 2, ISO 27001 and PCI
The audit report is the byproduct. Being secure is the product
So we built the move around your audit window.
We import your evidence, policies and mappings, with dates and approvals intact.
Same firm, same audit period. They get a read-only portal invite.
One engineer owns your migration, with a shared Slack channel from the first call.
30 minutes with a compliance expert, a read-only role, and your real SOC 2 or ISO 27001 posture.
About this comparison. Claims about Drata are drawn from Drata's published pricing, framework, help and developer pages and from verified customer reviews on G2. Claims about UprootSecurity are drawn from uprootsecurity.com. Review themes are reported, not product fact. Figures were checked on 6 November 2026. Drata is a trademark of its respective owner; this page is published by UprootSecurity and is not endorsed by Drata.
