Manual vs Automated Compliance: Costs and When to Switch
Robin Joseph
Senior Security Consultant
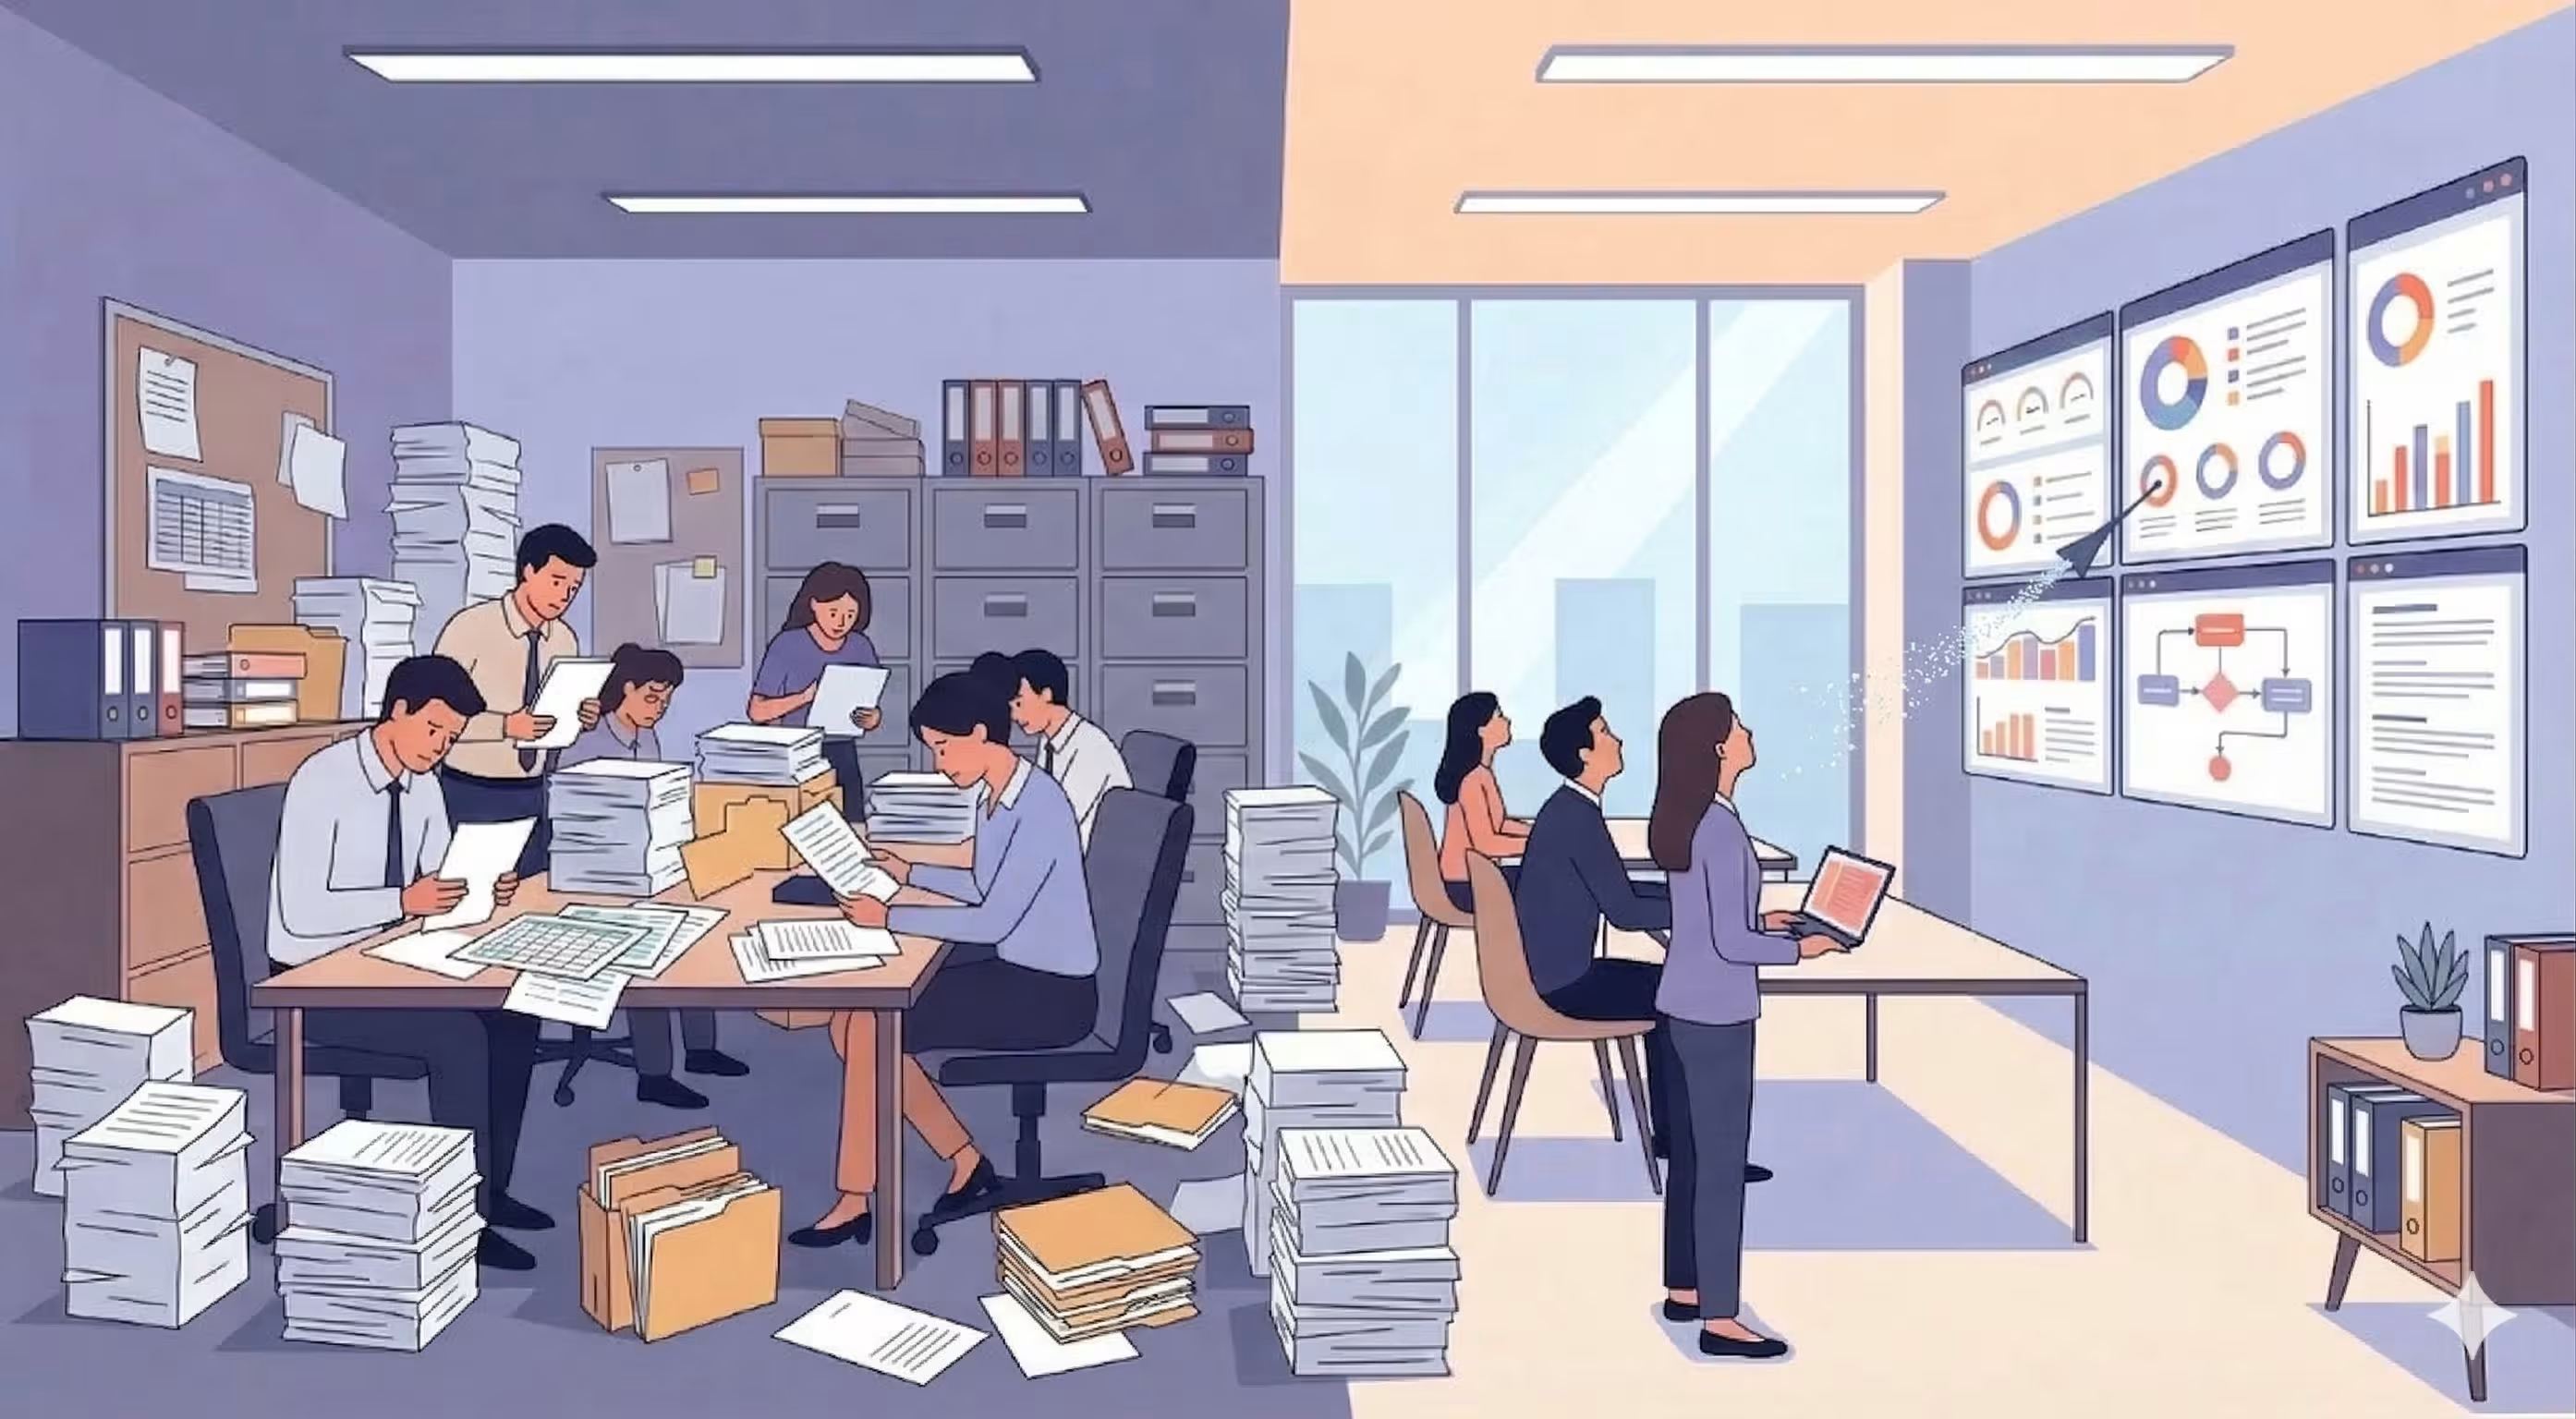
Manual compliance means people collect evidence, track controls, and chase approvals by hand, usually in spreadsheets. Automated compliance connects to your cloud, identity, and code tools and does this all year. Manual can work for one framework and a small team. Automation starts to pay off once you renew SOC 2 or ISO 27001 every year, run more than one framework, or keep losing time to security questionnaires.
The automated way of doing compliance helps a company stay more secure and more compliant. The manual way, done for long enough, tends to slide into compliance theater: paperwork that looks complete but does not reflect what is actually running. The rest of this guide compares the two on cost, then on risk and when it is time to switch.
Manual vs Automated Compliance at a Glance
This table covers the differences that matter most in the manual vs automated compliance decision.
| Area | Manual compliance | Automated compliance |
|---|---|---|
| Evidence collection | Screenshots, exports, and emails gathered by people before each audit | Pulled from your systems on a schedule and time-stamped |
| Control monitoring | Checked at set points, often before an audit | Checked continuously, with alerts when a control fails |
| Audit readiness | A scramble before each audit | Evidence is already in place |
| Error risk | Typos, stale files, and version mix-ups | Fewer copy-and-paste errors, but a wrong setup can still miss a control |
| Several frameworks | The work is repeated for each framework | One control can be mapped to several frameworks |
| Cost profile | No tool fee, but staff time that repeats every audit | A platform fee, with less staff time |
| Scale | Effort grows with headcount, systems, and frameworks | Effort grows slowly as you add systems |
| Who runs it | Someone who owns the trackers and chases people | Someone who owns setup and fixes what gets flagged |
| Best for | One framework, a small team, a simple stack | Yearly renewals, several frameworks, a growing team |
The short version: manual is cheaper to start and gets more expensive as you grow. Automation costs more up front and saves time as audits, frameworks, and systems pile up. The next two sections cover the two questions in the title, what each approach really costs and when to switch.
The first time through is the easy comparison. A first-year audit only has to show controls were in place for a shorter window, so a manual tracker built in a hurry can still pass. The second year is where the gap shows up: the auditor now expects evidence collected across the full period since the last report, not evidence assembled right before the fieldwork starts. A spreadsheet that was rebuilt from memory a week before the deadline does not hold up to that. This is usually the point teams feel the real cost of staying manual.
The Real Cost of Manual vs Automated Compliance
Manual compliance looks cheap because there is no invoice. The cost is staff time, and it repeats every audit. Automated compliance has a visible fee, and it changes where the time goes. Compare them line by line instead of comparing a fee against zero.
Where the Money Goes
| Cost line | Manual compliance | Automated compliance |
|---|---|---|
| Platform fee | None | Yearly fee. Uproot's SOC 2 plan starts at $8,000 a year for one entity, one framework, and up to 200 employees |
| Staff time on evidence | High. Evidence is collected again for every audit and every framework | Lower. Evidence is collected on a schedule |
| Staff time on setup | Low at first | Higher in the first weeks, while systems are connected |
| Auditor fees | Yes | Yes, the same |
| Readiness help | Consultants or contractors are more common | Less often needed |
| Rework after findings | More likely, because stale or missing evidence surfaces at audit time | Less likely, because failures show up during the year |
What Automation Does Not Change
Automation does not remove the auditor fee. Auditor fees go straight to the CPA firm, typically $15,000 to $35,000 for a first Type II, according to Uproot's SOC 2 page. Those fees apply either way. What automation changes is how much staff time goes into preparing for the audit. For more on audit pricing, see how much a SOC 2 audit costs. If you are comparing what tools charge, our GRC software pricing guide explains the pricing models.
How to Estimate Your Own Manual Cost
Use your own numbers, not a number from a vendor. Count these four things:
- The hours your team spends on evidence, follow-ups, and tracker updates before each audit.
- The hours spent on the same work between audits, such as quarterly access reviews.
- The loaded hourly cost of the people doing it, including engineers pulled from product work.
- How many audits and frameworks you run each year.
Multiply hours by hourly cost, then by the number of audits. Compare that total with the platform fee plus the setup hours. We do not print an hours-per-audit figure here, because we could not find a trustworthy public source and it varies a lot from company to company.
Hidden Costs on Both Sides
Manual programs carry hidden costs: rework after audit findings, deals delayed while someone hunts for a report or a questionnaire answer, and engineers pulled away from product work. Automation has hidden costs too, mainly setup time and the effort of keeping integrations connected. Neither is free. The point is to know which cost you are choosing.
Signs It Is Time to Switch From Manual to Automated
Most teams do not switch because of a plan. They switch because something breaks. Look for these six signs before it does:
- Audit prep pulls engineers off product work for weeks. If evidence gathering feels like a second job, the cost is already showing up in your roadmap.
- You are adding a second framework. ISO 27001 after SOC 2 means many controls overlap, and a spreadsheet per framework repeats the work.
- Customers send security questionnaires faster than you can answer them. Slow answers delay deals.
- You cannot say today which controls are passing. If the answer is "we will know at the audit", you are checking too rarely.
- Evidence lives in more than three places. Email, shared drives, tickets, and chat make it hard to prove anything quickly.
- One person is a single point of failure. If they leave, the process leaves with them.
A Quick Score
Give yourself one point for each sign that is true today. This is a rule of thumb, not a formula.
- 0 to 1 points: Manual is likely fine. Set a date to review the decision.
- 2 to 3 points: Start comparing platforms now, before your next audit, not during it.
- 4 or more points: You are already paying for manual work in time and risk. Plan the switch for the start of your next observation window.
Switching does not mean replacing people. It means the same people stop copying files and start fixing problems.
What Is Manual Compliance?
Manual compliance is running your compliance program by hand. People write the policies, collect the evidence, track which controls are done, and send files to the auditor. The tools are usually spreadsheets, shared drives, ticketing systems, and email.
It works when the scope is small: one framework, a few systems, and a team that can keep the tracker current. There is no platform fee, and you control every step.
Where Spreadsheets Break
Spreadsheets hold up until the whole process depends on them. Then three problems show up. Ownership gets fuzzy, because nobody is sure who updated which row. Versions drift, because a file gets copied and edited in two places. And evidence goes stale, because a screenshot from March does not prove a control worked in September.
Research on spreadsheet quality is old but consistent. Field audits of real company spreadsheets found errors in at least 86% of them, according to Panko (2000). That study is not about compliance, but it shows why a manual tracker needs constant checking.
There is also a people risk. One person usually builds the tracker. When they leave, the logic behind it leaves too.
What Does Automated Compliance Mean?
Automated compliance, also called compliance automation, means software does the repeat work of a compliance program. It connects to your cloud, identity provider, code repositories, HR system, and endpoint tools, then does four things:
- Collects evidence directly from those systems, with a timestamp
- Runs continuous compliance monitoring, testing controls on a schedule and flagging any that fail
- Maps one control to every framework it satisfies
- Builds the reports and access your auditor asks for
Software does not do the judgment work. People still set scope, write policies, fix problems, and answer the auditor. For a step-by-step view, see our guide on how compliance automation works.
For example, Uproot's continuous monitoring runs more than 1,200 tests every fifteen minutes, and its evidence library stores each item hashed and time-stamped.
Examples of What Gets Automated
- Pulling evidence such as access lists and configuration settings from cloud and identity tools
- Testing controls on a schedule, such as multi-factor authentication or encryption settings
- Tracking employee tasks such as policy acceptance, training, and device checks
- Reminding owners when a control fails or evidence is about to expire
- Mapping one control to SOC 2, ISO 27001, HIPAA, and GDPR requirements
- Giving auditors a read-only view instead of sending files by email
What to Look For in a Compliance Automation Platform
Rankings change, and the best fit depends on your stack, so use criteria instead of a list of names:
- Integrations: does it connect to the cloud, identity, code, and HR tools you already use?
- Frameworks: can one control cover several frameworks, so you do not repeat work?
- Testing: are controls tested continuously, or only when someone clicks a button?
- Auditor experience: can your auditor see scoped evidence without email?
- Pricing: is the fee public, and what does it leave out, such as auditor costs?
- Support: who helps when a control fails or an integration breaks?
Compare two or three platforms against this list before you book a demo.
Can SOC 2 Compliance Be Automated?
Mostly the evidence work can be. Software can collect proof from your systems, test controls on a schedule, and flag failures. It cannot decide your scope, write policies that fit how you work, or pass the audit for you. A licensed CPA firm still performs the SOC 2 audit and issues the report.
| Software can handle | People still handle |
|---|---|
| Collecting evidence from cloud, identity, and code tools | Deciding scope and which trust criteria to include |
| Testing controls on a schedule | Fixing a control that fails |
| Tracking policy acceptance and training | Writing policies that match how the company works |
| Keeping evidence time-stamped and organized | Reviewing vendors and making risk decisions |
| Giving the auditor a read-only view | Choosing the auditor and answering their questions |
The same split applies to ISO 27001, HIPAA, and GDPR. Automation shortens preparation and keeps evidence current. It does not replace the audit or the decisions behind it.
Risks of Each Approach
Risks of Manual Compliance
- Errors and stale evidence: a file is out of date, or a row was never updated.
- Gaps between audits: a control fails in May and nobody finds out until November.
- Audit-time crunch: the team stops other work to collect evidence.
- Key-person dependency: the tracker only makes sense to its author.
- Scale: each new framework or system multiplies the work.
Risks of Automated Compliance
- False confidence: a green dashboard does not mean every control is in scope.
- Integration gaps: a system that is not connected produces no evidence.
- Setup effort: mapping controls to your real systems takes work.
- Ignored alerts: flagged failures that nobody owns do not get fixed.
Automation reduces the risk it can see, such as configuration drift, missing multi-factor authentication, and unreviewed access. It does not reduce risk in systems it is not connected to. Neither approach is a regulatory requirement: SOC 2, ISO 27001, HIPAA, and GDPR ask you to show controls work, not to use a particular tool.
When Manual Compliance Is Still Fine
Manual compliance can still be the right call. It tends to work when all of these are true:
- You are working toward one framework.
- Your stack is small, for example one product and one cloud account.
- Nobody is asking for continuous evidence.
- One named person owns the tracker, with a backup.
A ten-person team with one SOC 2 Type II a year could run this well. Set a date to review the decision, and revisit it when any of the four points above change.
Is a Hybrid Compliance Approach Enough?
A hybrid compliance approach automates evidence collection and monitoring, and keeps policies, risk decisions, and vendor reviews with people. Most teams end up here, because judgment work needs a person.
The risk is a half-connected setup. Some systems feed a platform and others are tracked in a spreadsheet, so nobody trusts either one. The fix is a simple rule: one source of truth for each control.
How Do You Decide What to Automate?
Ask two questions about each task. Does it repeat? Can a system answer it with a yes or no? If both answers are yes, automate it. If the task needs context or a decision, keep it with a person.
- Automate: evidence collection, access reviews, configuration tests, reminders, and reports.
- Keep human: scope, policy wording, risk decisions, vendor reviews, and talking to the auditor.
- Automate, then review: alerts and exceptions, where software finds the issue and a person decides what to do.
How to Move From Manual to Automated
- Write down what you have. List your frameworks, systems, evidence locations, and owners.
- Decide the scope. Pick the frameworks you need now and the ones you will need next, so you do not do the same work twice.
- Connect the biggest systems first. Start with cloud, identity, code, and HR.
- Run both for one cycle. Compare the platform's results with your tracker and fix any mismatch.
- Retire the spreadsheet. Keep one source of truth, and move policies and reviews into the platform.
Connecting systems is the quick part. Getting your team to trust and act on the results is what takes about one audit cycle. Tell your auditor early which evidence will come from the platform. If you are a startup planning this from scratch, our compliance for startups guide covers what to do first.
Frequently Asked Questions
Automated compliance means software does the repeat work of a compliance program. It connects to your cloud, identity, and code tools, collects time-stamped evidence, tests controls on a schedule, and flags failures. People still set the scope, write policies, fix problems, and answer the auditor. It is also called compliance automation.
Manual compliance is running your compliance program by hand. People write policies, collect evidence, track which controls are done, and send files to the auditor, usually with spreadsheets, shared drives, and email. It works for small scopes, but the effort grows with every framework, system, and audit.
The main differences are timing, effort, and scale. Manual compliance collects evidence by hand at set points, mostly before an audit. Automated compliance collects it all year and alerts you when a control fails. Manual effort grows with every framework and system. Automated effort grows more slowly, but adds a platform fee.
Mostly the evidence work can. Software can collect proof from your systems, test controls on a schedule, and flag failures. It cannot write your policies for you, decide your scope, or pass the audit. A CPA firm still performs the SOC 2 audit, so automation shortens the preparation, not the audit itself.
Move when audit prep pulls engineers off product work, when you add a second framework, when customers send security questionnaires faster than you can answer, or when you cannot say which controls pass today. If two or three of these apply, start comparing platforms before your next audit, not during it.
It adds a platform fee, but manual work has a cost too: staff time that repeats every audit. According to Uproot's SOC 2 page, its plan starts at $8,000 a year for one framework and up to 200 employees. Auditor fees, typically $15,000 to $35,000 for a first Type II, are separate either way.
The best tool depends on your frameworks, team size, and stack. Look for integrations with your cloud, identity, and code tools, one control mapped to many frameworks, continuous testing, an auditor view, and clear pricing. Ask what the fee leaves out, such as auditor costs. Compare two or three platforms against your own checklist.
Automate work that repeats and that a machine can check, such as evidence collection, access reviews, and configuration tests. Keep work that needs judgment with people, such as scope, policies, risk decisions, and vendor reviews. A simple test: if a system can answer yes or no, automate it. If it needs context, keep it human.
No. Automation removes copy-and-paste work such as gathering evidence and building reports. People still decide scope, write policies, review vendors, fix failed controls, and talk to auditors. The same team can spend its time on fixes and decisions instead of chasing files.
Evidence is collected and time-stamped as you go, so it already exists when the auditor asks. Continuous compliance monitoring tests controls all year, so failures show up when they happen instead of during the audit. That turns audit prep from a project into a review of what is already in place.
Choosing the Right Approach for Your Team
Manual compliance is a fair choice for a small scope. It stops being fair once evidence chasing takes weeks, a second framework arrives, or customers ask for proof faster than you can produce it. At that point the question is no longer whether to automate, but which parts to automate first, and how to keep people focused on the decisions only they can make.
UprootSecurity is a compliance platform built for engineering teams that sell to enterprise customers. It connects to your cloud, identity, code, and HR tools, runs more than 1,200 tests every fifteen minutes, and stores each piece of evidence hashed and time-stamped, so your SOC 2 or ISO 27001 evidence stays current all year instead of being rebuilt before each audit. The same controls map to SOC 2, ISO 27001, HIPAA, GDPR, and more, so adding a framework does not mean starting over. Auditors get a scoped, read-only view of exactly what they test. Uproot's published median time to SOC 2 readiness is 38 days, and plans start at $8,000 a year for one framework and up to 200 employees. If your audit prep still runs on spreadsheets and email, it is worth seeing what it looks like when the evidence is already there.
Continuous Compliance & GRC Ops