ISO 27001 certification costs a company of 10 to 120 people about $15,000 to $67,500 in outside fees in the first year.
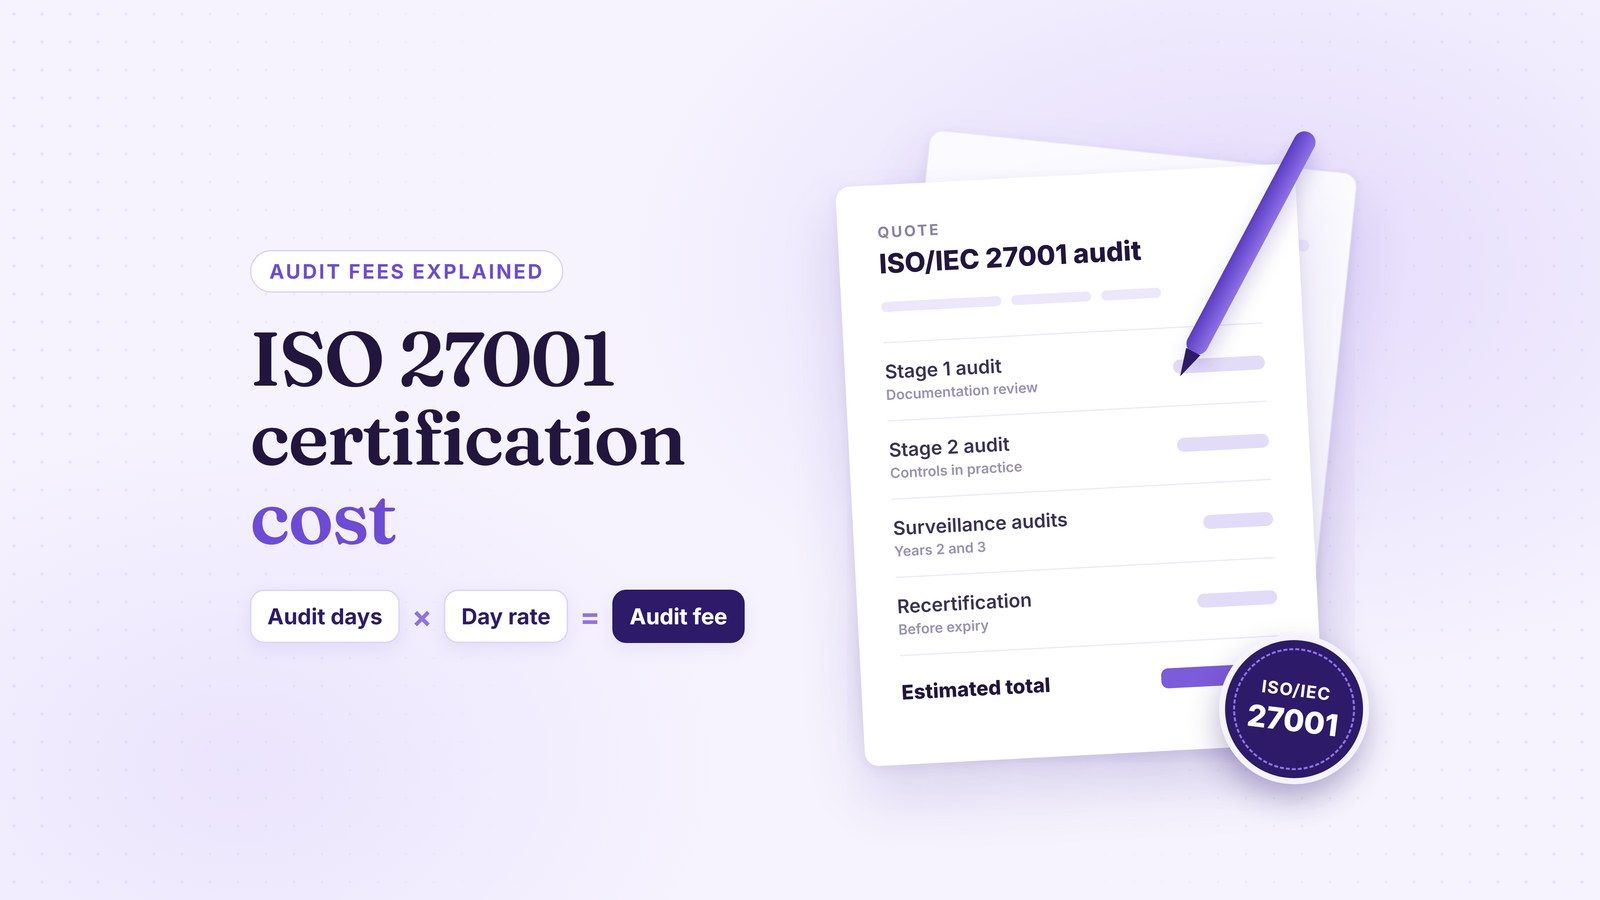
The certification audit itself is about $9,000 to $21,000 of that: the audit days your headcount requires, times the certification body's day rate. Your team's time comes on top, and it is often the biggest cost. Every number below is sourced or marked as our estimate.
Reviewed by Riya Ann Varghese, GRC Engineer, ISO 27001 lead auditor certified. Last updated November 17, 2026.
What Does ISO 27001 Cost by Company Size?
The ISO 27001 cost for a 10-person company is about $15,000 to $25,000 in first-year outside fees, rising to $38,500 to $67,500 for 120 people.
| Cost item | About 10 staff | About 40 staff | About 120 staff |
|---|---|---|---|
| Certification audit (Stage 1 + Stage 2) | about $9,000 | about $15,000 | about $21,000 |
| Year 1 outside fees (audit, standard, consultant days) | $15,000 to $25,000 | $25,500 to $43,000 | $38,500 to $67,500 |
| Year 1 internal staff time (wage cost, our estimate) | about $17,000 | about $29,500 | about $49,500 |
| Years 2 and 3 outside fees, each year | $4,000 to $5,500 | $6,500 to $9,000 | $9,000 to $12,500 |
| 3-year outside fees in total | $23,000 to $36,000 | $38,500 to $61,000 | $56,500 to $92,500 |
Audit fees use one published day rate, without travel or VAT. Outside fees assume a consultant handles the gap analysis, internal audit and part of the setup (day counts are our estimates). A platform subscription would replace some consultant days and staff hours. Staff time is wages only. We round our own estimates to the nearest $500.
How Much Does an ISO 27001 Audit Cost?
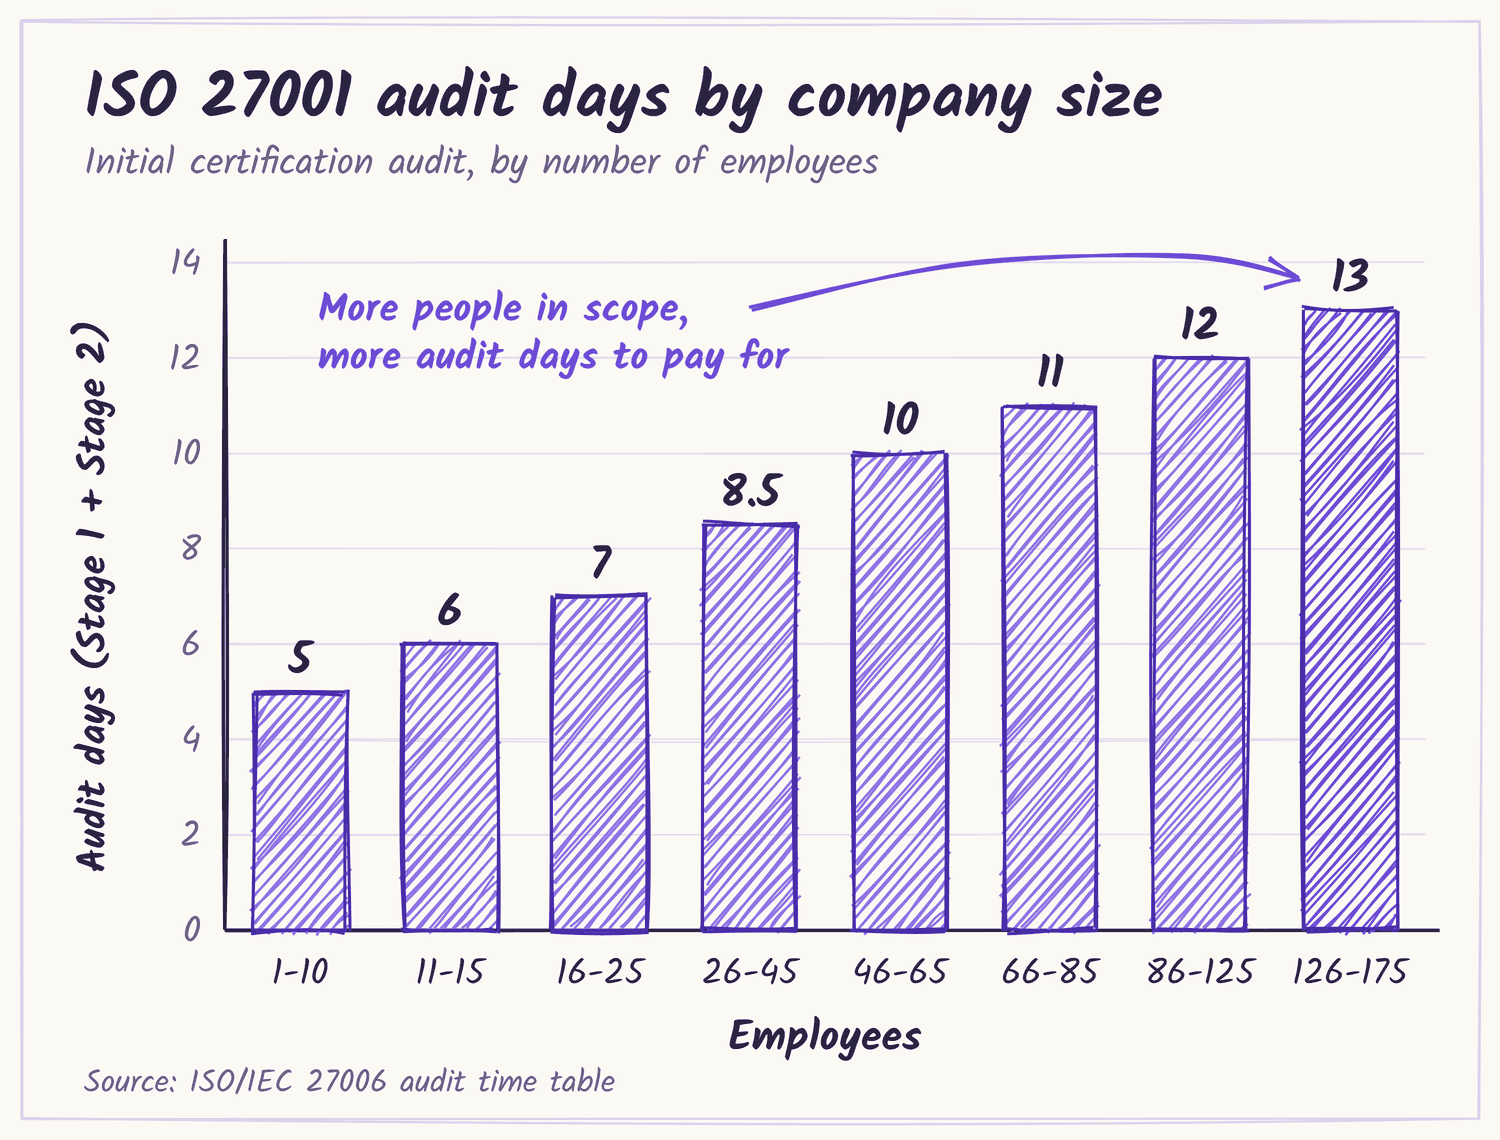
An ISO 27001 audit costs about $9,000 for a company of up to 10 people and about $23,000 for 126 to 175 people, at one published rate.
Two numbers set the ISO 27001 audit cost:
- Audit days. ISO/IEC 27006-1 sets audit time for ISO 27001 certification bodies, based mainly on the number of people in scope. Accredited bodies must follow it.
- The day rate. Each certification body sets its own. TÜV Saarland, an accredited German certification body, publishes its price list: about $1,760 per auditor day for ISO/IEC 27001, including preparation and reporting. VAT is extra and travel is billed at cost. We converted the published price to dollars at the ECB reference rate of November 13, 2026.
This is one published example rate. US certification bodies quote their own rates, so ask each body for a quote showing audit days and the day rate.
| People in scope | Audit days (Stage 1 + Stage 2) | About in USD |
|---|---|---|
| 1 to 10 | 5 | $9,000 |
| 11 to 15 | 6 | $10,500 |
| 16 to 25 | 7 | $12,500 |
| 26 to 45 | 8.5 | $15,000 |
| 46 to 65 | 10 | $17,500 |
| 66 to 85 | 11 | $19,500 |
| 86 to 125 | 12 | $21,000 |
| 126 to 175 | 13 | $23,000 |
What Changes the Number of Audit Days?
The number of ISO 27001 audit days changes with your scope, your sites and how complex your systems are.
- People in scope. Count everyone inside the ISMS scope, including contractors.
- Reductions. A simple, low-risk scope can earn a reduction of up to about 30%. For 1 to 10 people, that means about 3.5 days, or roughly $6,000.
- Additions. More sites, complex IT, many outsourced processes or a regulated business can add days.
- Travel. On-site audits add the auditor's travel time and expenses.
Our guide to the six steps to ISO 27001 certification shows where scope is set.
Not sure how many audit days your scope needs? Talk to a compliance expert at UprootSecurity before you ask bodies for quotes.
What Do Surveillance and Recertification Audits Cost?
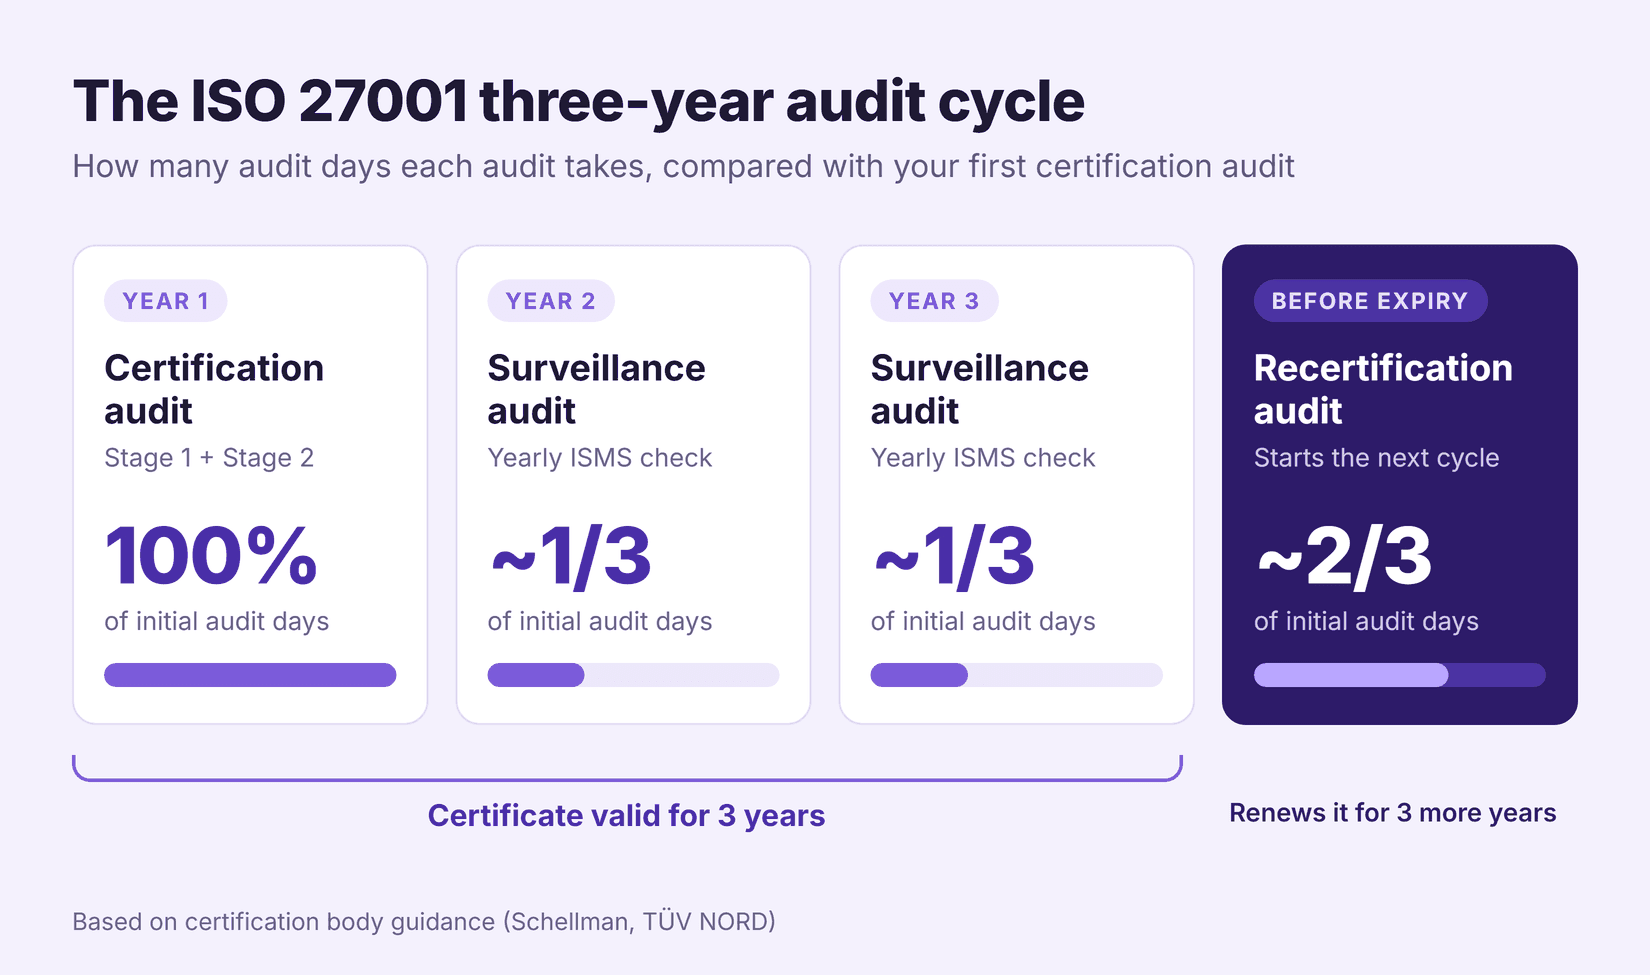
ISO 27001 surveillance audits cost about one third of your first audit each year, and a recertification audit costs about two thirds.
An ISO 27001 certificate is valid for three years. The body runs a surveillance audit in years 2 and 3, then a recertification audit before the certificate expires. Schellman, an accredited certification body, says each surveillance review takes about 1/3 of the initial audit time and recertification about 2/3. The renewal cost below uses that rule and the same day rate.
| People in scope | Surveillance audit (years 2 and 3, each) | Recertification audit (end of year 3) |
|---|---|---|
| 1 to 10 | 1.7 days, about $3,000 | 3.3 days, about $6,000 |
| 11 to 15 | 2 days, about $3,500 | 4 days, about $7,000 |
| 16 to 25 | 2.3 days, about $4,000 | 4.7 days, about $8,000 |
| 26 to 45 | 2.8 days, about $5,000 | 5.7 days, about $10,000 |
| 46 to 65 | 3.3 days, about $6,000 | 6.7 days, about $11,500 |
| 66 to 85 | 3.7 days, about $6,500 | 7.3 days, about $13,000 |
| 86 to 125 | 4 days, about $7,000 | 8 days, about $14,000 |
| 126 to 175 | 4.3 days, about $7,500 | 8.7 days, about $15,000 |
Why Do ISO 27001 Cost Estimates Vary So Much?
ISO 27001 cost estimates vary because they count different things: some quote only the audit, some the first year, and some the full three-year cycle.
Vendor guides quote $6,000 to $40,000+, often without saying what is inside. Here is one 10-person company counted four ways:
| What is counted | Often called | 10-person company |
|---|---|---|
| Stage 1 + Stage 2 audit only | "ISO 27001 audit cost" | about $9,000 |
| Year 1 outside fees | "ISO 27001 certification cost" | $15,000 to $25,000 |
| Year 1 outside fees plus staff time | "Total cost" | $32,000 to $42,000 |
| Three years of outside fees | "Cost of ownership" | $23,000 to $36,000 |
Other reasons quotes differ:
- Scope. A wider scope than customers need adds audit days.
- Certification body. Day rates differ, but all accredited bodies use the same audit-day rules.
- Path. DIY, a consultant or a platform moves cost between cash and staff time.
- Readiness. Major Stage 2 findings can mean extra audit days.
What Else Do You Pay for Besides the Audit?
Besides the audit, ISO 27001 costs include the standard, a gap analysis, an internal audit, outside help, tools, and your own team's time.
The Standard Itself
ISO/IEC 27001:2022 costs about $185 on the ISO store. ISO/IEC 27002 guidance is optional.
Gap Analysis and Internal Audit
A gap analysis shows what is missing. The internal audit is required by clause 9.2 of ISO 27001 and must be impartial, so small teams often hire it out. We estimate 2 to 5 consultant days for each.
Consultant Fees
ISO 27001 consultants charge about $500 to $1,330 per day, according to Amtivo, an accredited certification body. Your certification body cannot consult for you, because auditors must stay independent. Our year 1 totals assume 8, 15 or 25 consultant days for setup, our estimate.
Tools and a Yearly Pentest
A compliance platform collects evidence and tracks controls. Startup platform list prices run from $7,500 to $32,500 a year, as our compliance software pricing guide shows. Many teams also run a yearly penetration test at about $3,000 to $10,000, which is not in our totals.
Your Team's Time
Internal time is the cost most estimates skip. We priced it with US Bureau of Labor Statistics 2025 median wages.
| Role | BLS median hourly wage | Year 1 hours (10 / 40 / 120 staff) | Wage cost (10 / 40 / 120 staff) |
|---|---|---|---|
| ISMS owner (information security analyst) | $62.11 | 160 / 250 / 400 | $10,000 / $15,500 / $25,000 |
| Engineers (software developers, QA and testers) | $64.44 | 80 / 160 / 300 | $5,000 / $10,500 / $19,500 |
| Leadership (IT and security managers) | $84.20 | 24 / 40 / 60 | $2,000 / $3,500 / $5,000 |
| Total | $17,000 / $29,500 / $49,500 |
Hours are our estimate for a consultant-assisted project. Wages are medians before benefits.
DIY vs Consultant vs Compliance Platform: Which Costs Less?
Doing ISO 27001 yourself costs the least in cash, but it usually costs the most in staff time and in the risk of a failed audit.
| Path | What you pay for | Cash cost | Staff time | Best for |
|---|---|---|---|---|
| DIY | Audit, standard, hired internal audit | Lowest | Highest | Teams with someone who has run an ISMS before |
| Consultant | Day rate of about $500 to $1,330 plus the audit | Highest | Medium | Teams that want hands-on writing help |
| Compliance platform | Yearly subscription plus the audit | Medium | Lower for evidence | Cloud companies with many tools to connect |
| Platform plus expert | Subscription, expert guidance and the audit | Medium | Lowest | Small teams with no security hire |
How Much Does ISO 27001 Cost If You Already Have SOC 2?
ISO 27001 costs less if you already have SOC 2, because many controls overlap and you mainly add ISMS documents and the ISO audit.
What you still need to add:
- An ISMS scope statement and information security policy.
- A formal risk assessment and risk treatment plan.
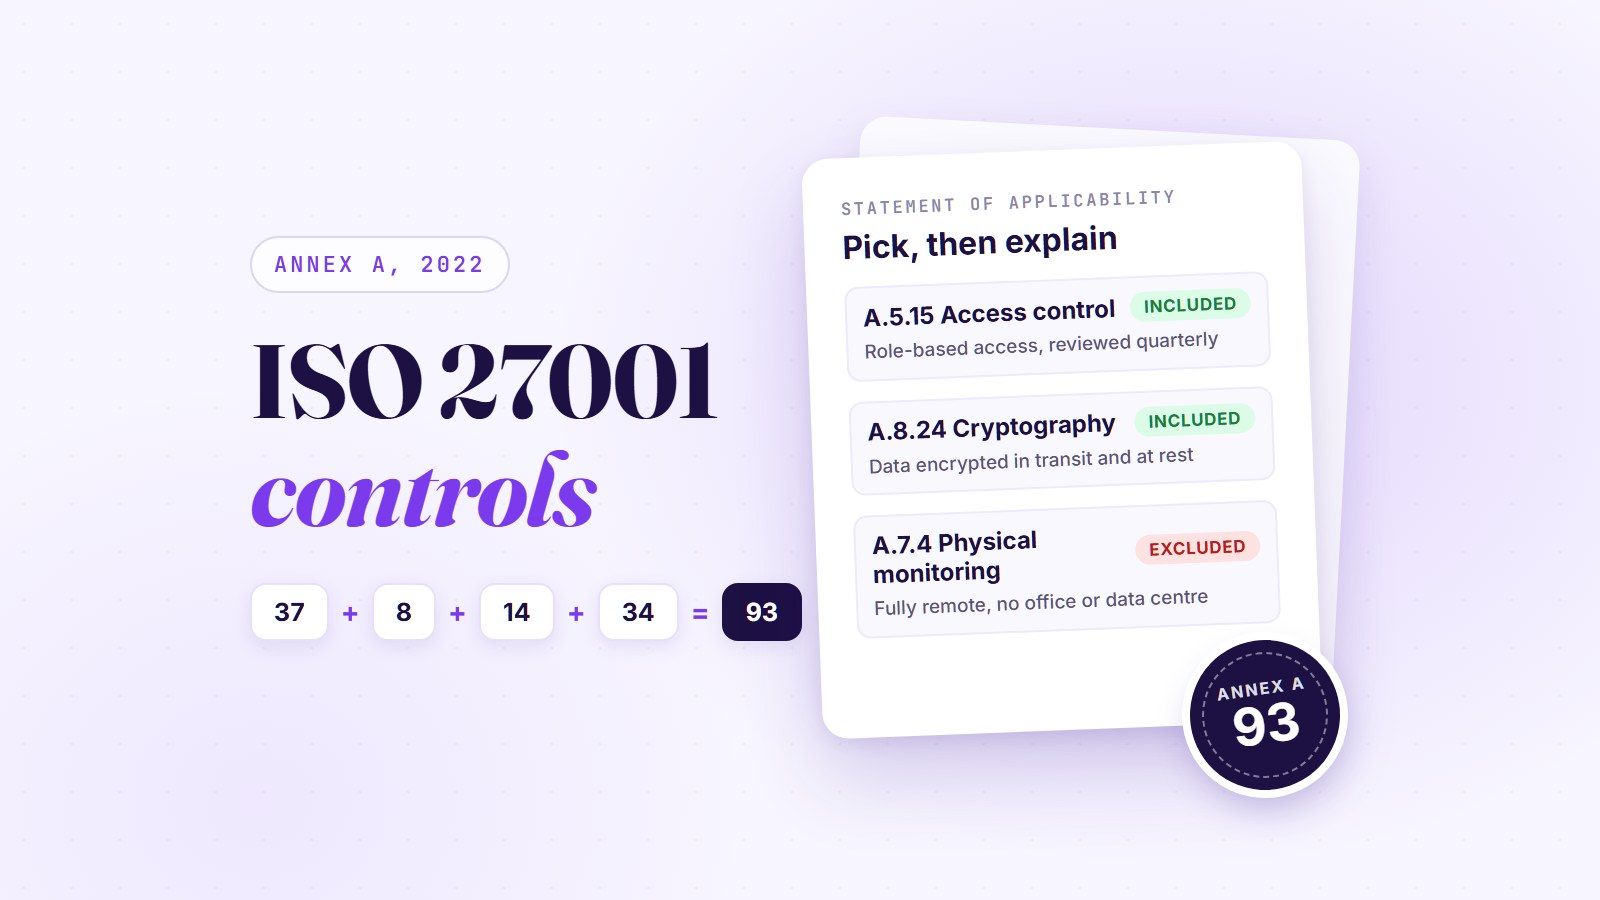
- A Statement of Applicability covering the 93 Annex A controls.
- An internal audit and a management review.
The audit fee does not shrink, because audit days follow headcount. You save on staff time. Our guide to SOC 2 vs ISO 27001 compares both, and you can also check what a SOC 2 audit costs. New to the standard? Read what ISO 27001 is, or see our guide to ISO 27001 for startups.
How Do You Check a Certification Body Is Accredited?
Companies get ISO 27001 certified, while certification bodies get accredited by an accreditation body, such as ANAB or IAS in the US or UKAS in the UK. These three are signatories of the IAF Multilateral Recognition Arrangement (MLA), which lets accreditation bodies recognise each other's work, so an accredited certificate should be accepted across borders. The International Accreditation Forum (IAF) was a forum of accreditation bodies, not an accreditor itself. From 1 January 2026 its work moved to Global Accreditation Cooperation Incorporated.
So searches for "ISO 27001 accreditation cost" usually mean the certification cost. Before you sign, ask the body for its accreditation certificate, check that its scope covers ISO/IEC 27001, and look it up on IAF CertSearch (https://www.iafcertsearch.org/). Customers may reject a certificate from an unaccredited body.
How UprootSecurity Helps You Budget and Pass ISO 27001
UprootSecurity gives you a dedicated compliance expert who scopes ISO 27001 so you do not pay for audit days you do not need. If you have SOC 2, we map your controls across 22 frameworks, so you build only what ISO 27001 adds. 140+ integrations collect evidence, cutting the staff hours that drive most of the cost.
We introduce you to accredited certification bodies. The audit is not included in our plan: you pay the audit fee directly to the body you choose. Our plans are a custom quote, and a yearly pentest is included. See how ISO 27001 compliance with UprootSecurity works.
| What you ask | What you get |
|---|---|
| "How many audit days will we need?" | A dedicated compliance expert scopes your ISMS before you request quotes |
| "We already have SOC 2. What is left?" | Control mapping across 22 frameworks shows only the ISO 27001 gaps |
| "Who collects all the evidence?" | 140+ integrations pull evidence from your cloud and tools |
| "Which auditor should we use?" | We introduce accredited certification bodies; you pay them directly |
| "Customers keep sending questionnaires" | Trust center and questionnaire automation on Growth and Enterprise plans |
Not sure what ISO 27001 will cost your team? → Book a demo today
Frequently Asked Questions
No, ISO 27001 certification is not free for companies. You pay an accredited certification body for the audit, plus the standard, outside help and staff time. Free templates exist, but only an accredited body's audit leads to a certificate. For a 10-person company, the Stage 1 and Stage 2 audit alone is about $9,000 at one published day rate.
Getting ISO 27001 certified costs about $15,000 to $67,500 in first-year outside fees for companies of 10 to 120 people. That covers the audit, the standard, and consultant days for the gap analysis, internal audit and setup. Your team's time adds roughly $17,000 to $49,500 in wages, based on our hour estimates and BLS median pay.
ISO 27001 costs a small business of about 10 people around $15,000 to $25,000 in first-year outside fees. The audit is about $9,000 for five audit days. Surveillance audits in years 2 and 3 cost about $3,000 each. A tight scope keeps it low.
ISO 27001 is a mid-sized investment for most companies, and the audit is the smaller part. The audit is about $9,000 to $21,000 for 10 to 120 people, while staff time is often the larger cost. The bill grows with headcount in scope, sites and outside help.
Most companies take about 3 to 6 months to get ISO 27001 certified. Larger or less prepared companies may need 6 to 12 months. The time covers scoping, risk assessment, building controls, running the ISMS, an internal audit, then the Stage 1 and Stage 2 audits. There is no fixed gap between the two stages.
ISO 27001 certification is valid for three years. During that time the certification body runs a surveillance audit in years 2 and 3, each about one third of the first audit's days. Before the certificate expires, a recertification audit of about two thirds of the original days starts the next three-year cycle.
Companies do not pay for ISO 27001 accreditation, because companies get certified and certification bodies get accredited. People searching for accreditation cost usually mean the certification cost, which is about $9,000 for the audit of a 10-person company. Check that your body is accredited by ANAB, IAS, UKAS or another IAF MLA signatory, using IAF CertSearch.
The ISO/IEC 27001:2022 standard costs about $185 on the ISO store. National standards bodies also sell it. ISO/IEC 27002, which explains the controls in more detail, is optional and sold separately. Buying the standard is the smallest cost in an ISO 27001 project.
ISO 27001 exams for individuals, such as lead auditor or lead implementer courses, are priced by each training provider. They are personal qualifications, not company certification. A lead auditor certificate does not make a company ISO 27001 certified; only an accredited body's audit does.
Companies need ISO 27001 certification when customers, partners or tenders require proof of information security. It is common for SaaS, cloud, fintech and health tech companies selling to enterprises in Europe, the UK and global markets. No law requires it in most countries, but many contracts do.