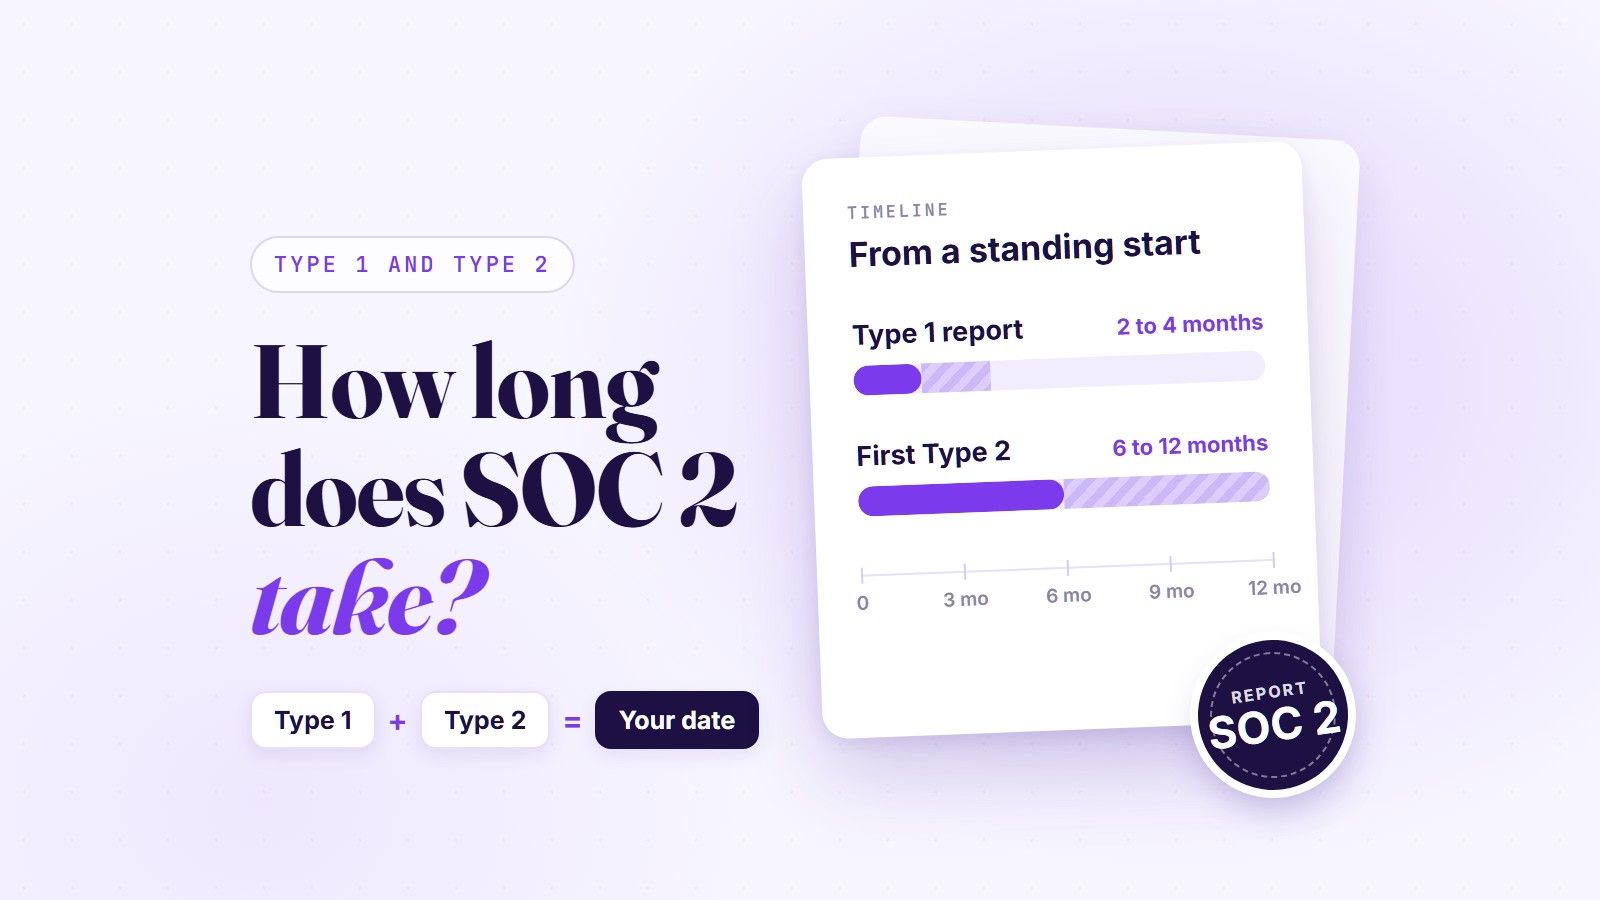
Getting SOC 2 compliant takes about 2 to 4 months for a Type 1 report and 6 to 12 months for a first Type 2. The range depends on how ready your controls are today.
If a customer is waiting, you do not have to make them wait in silence. This guide shows the real SOC 2 timeline, the fastest path week by week, and what to send the buyer this week.
Reviewed by Riya Ann Varghese, GRC Engineer, ISO 27001 lead auditor certified. Last updated November 18, 2026.
How Long Does It Take to Get SOC 2 Compliant?
From a standing start, a SOC 2 Type 1 report takes 2 to 4 months and a first Type 2 takes 6 to 12 months. The gap is the observation window: Type 1 checks controls on one date, Type 2 over 3 to 12 months.
Typical ranges per phase, from the audits our team supports:
| Phase | Type 1 | First Type 2 | Renewal Type 2 |
|---|---|---|---|
| Readiness assessment (gap check) | 1 to 3 weeks | 1 to 3 weeks | Not needed, or a quick review |
| Fixing gaps (policies, controls, evidence) | 4 to 10 weeks | 4 to 10 weeks | Ongoing |
| Observation window | None (one date) | 3 to 12 months | Usually 12 months |
| Auditor fieldwork | 2 to 5 weeks | 2 to 5 weeks | 2 to 5 weeks |
| Report writing and delivery | 2 to 6 weeks | 2 to 6 weeks | 2 to 6 weeks |
| Total | 2 to 4 months | 6 to 9 months with a 3-month window, about a year with 6 to 12 months | Report 1 to 3 months after the window ends |
The phases overlap. You book the auditor while you fix gaps, and a Type 1 sits at the short end of the fieldwork and report ranges because only one date is tested.
That table is the honest answer when a buyer asks how long does SOC 2 take. New to the basics? Our startup guide explains how to get SOC 2 compliance step by step.
How Long Does a SOC 2 Audit Take?
A SOC 2 audit takes about 2 to 5 weeks of auditor fieldwork, then 2 to 6 weeks for the written report. That is the audit phase alone.
Confusion starts when someone asks "how long does a SOC 2 audit take?" and means the whole journey. Founders hear "a few weeks", then learn a Type 2 needs months of observation first.
Keep the two apart with customers:
- The audit is the auditor testing your controls and writing the report. Weeks.
- The SOC 2 journey is readiness, the observation window, the audit and the report. Months.
Our SOC 2 audit process guide shows what happens during fieldwork.
What Decides Your SOC 2 Timeline?
Your SOC 2 timeline depends mostly on how many controls you already run and how long an observation window your buyer accepts. Five things move the date the most.
| Factor | Speeds it up | Slows it down |
|---|---|---|
| Starting maturity | MFA, access reviews and onboarding steps already in place | No written policies, shared admin accounts |
| Scope | Security criterion only, one product, cloud-only systems | All five Trust Services Criteria, many products, on-site offices in scope |
| Observation window | Buyer accepts a 3-month first window | Buyer or contract asks for 6 to 12 months |
| Auditor availability | Auditor booked in the first month | Auditor searched for after readiness ends |
| Evidence habits | Evidence collected automatically from your tools | Screenshots gathered by hand the week before fieldwork |
One named owner who chases tasks weekly saves more time than any tool.
A Customer Asked for Your SOC 2 Report: What to Send This Week
If a customer asks for your SOC 2 report before you have one, send proof of progress, not silence. Reviewers want to see you are serious and when the report arrives.
Send the highest step of this ladder you can reach today.
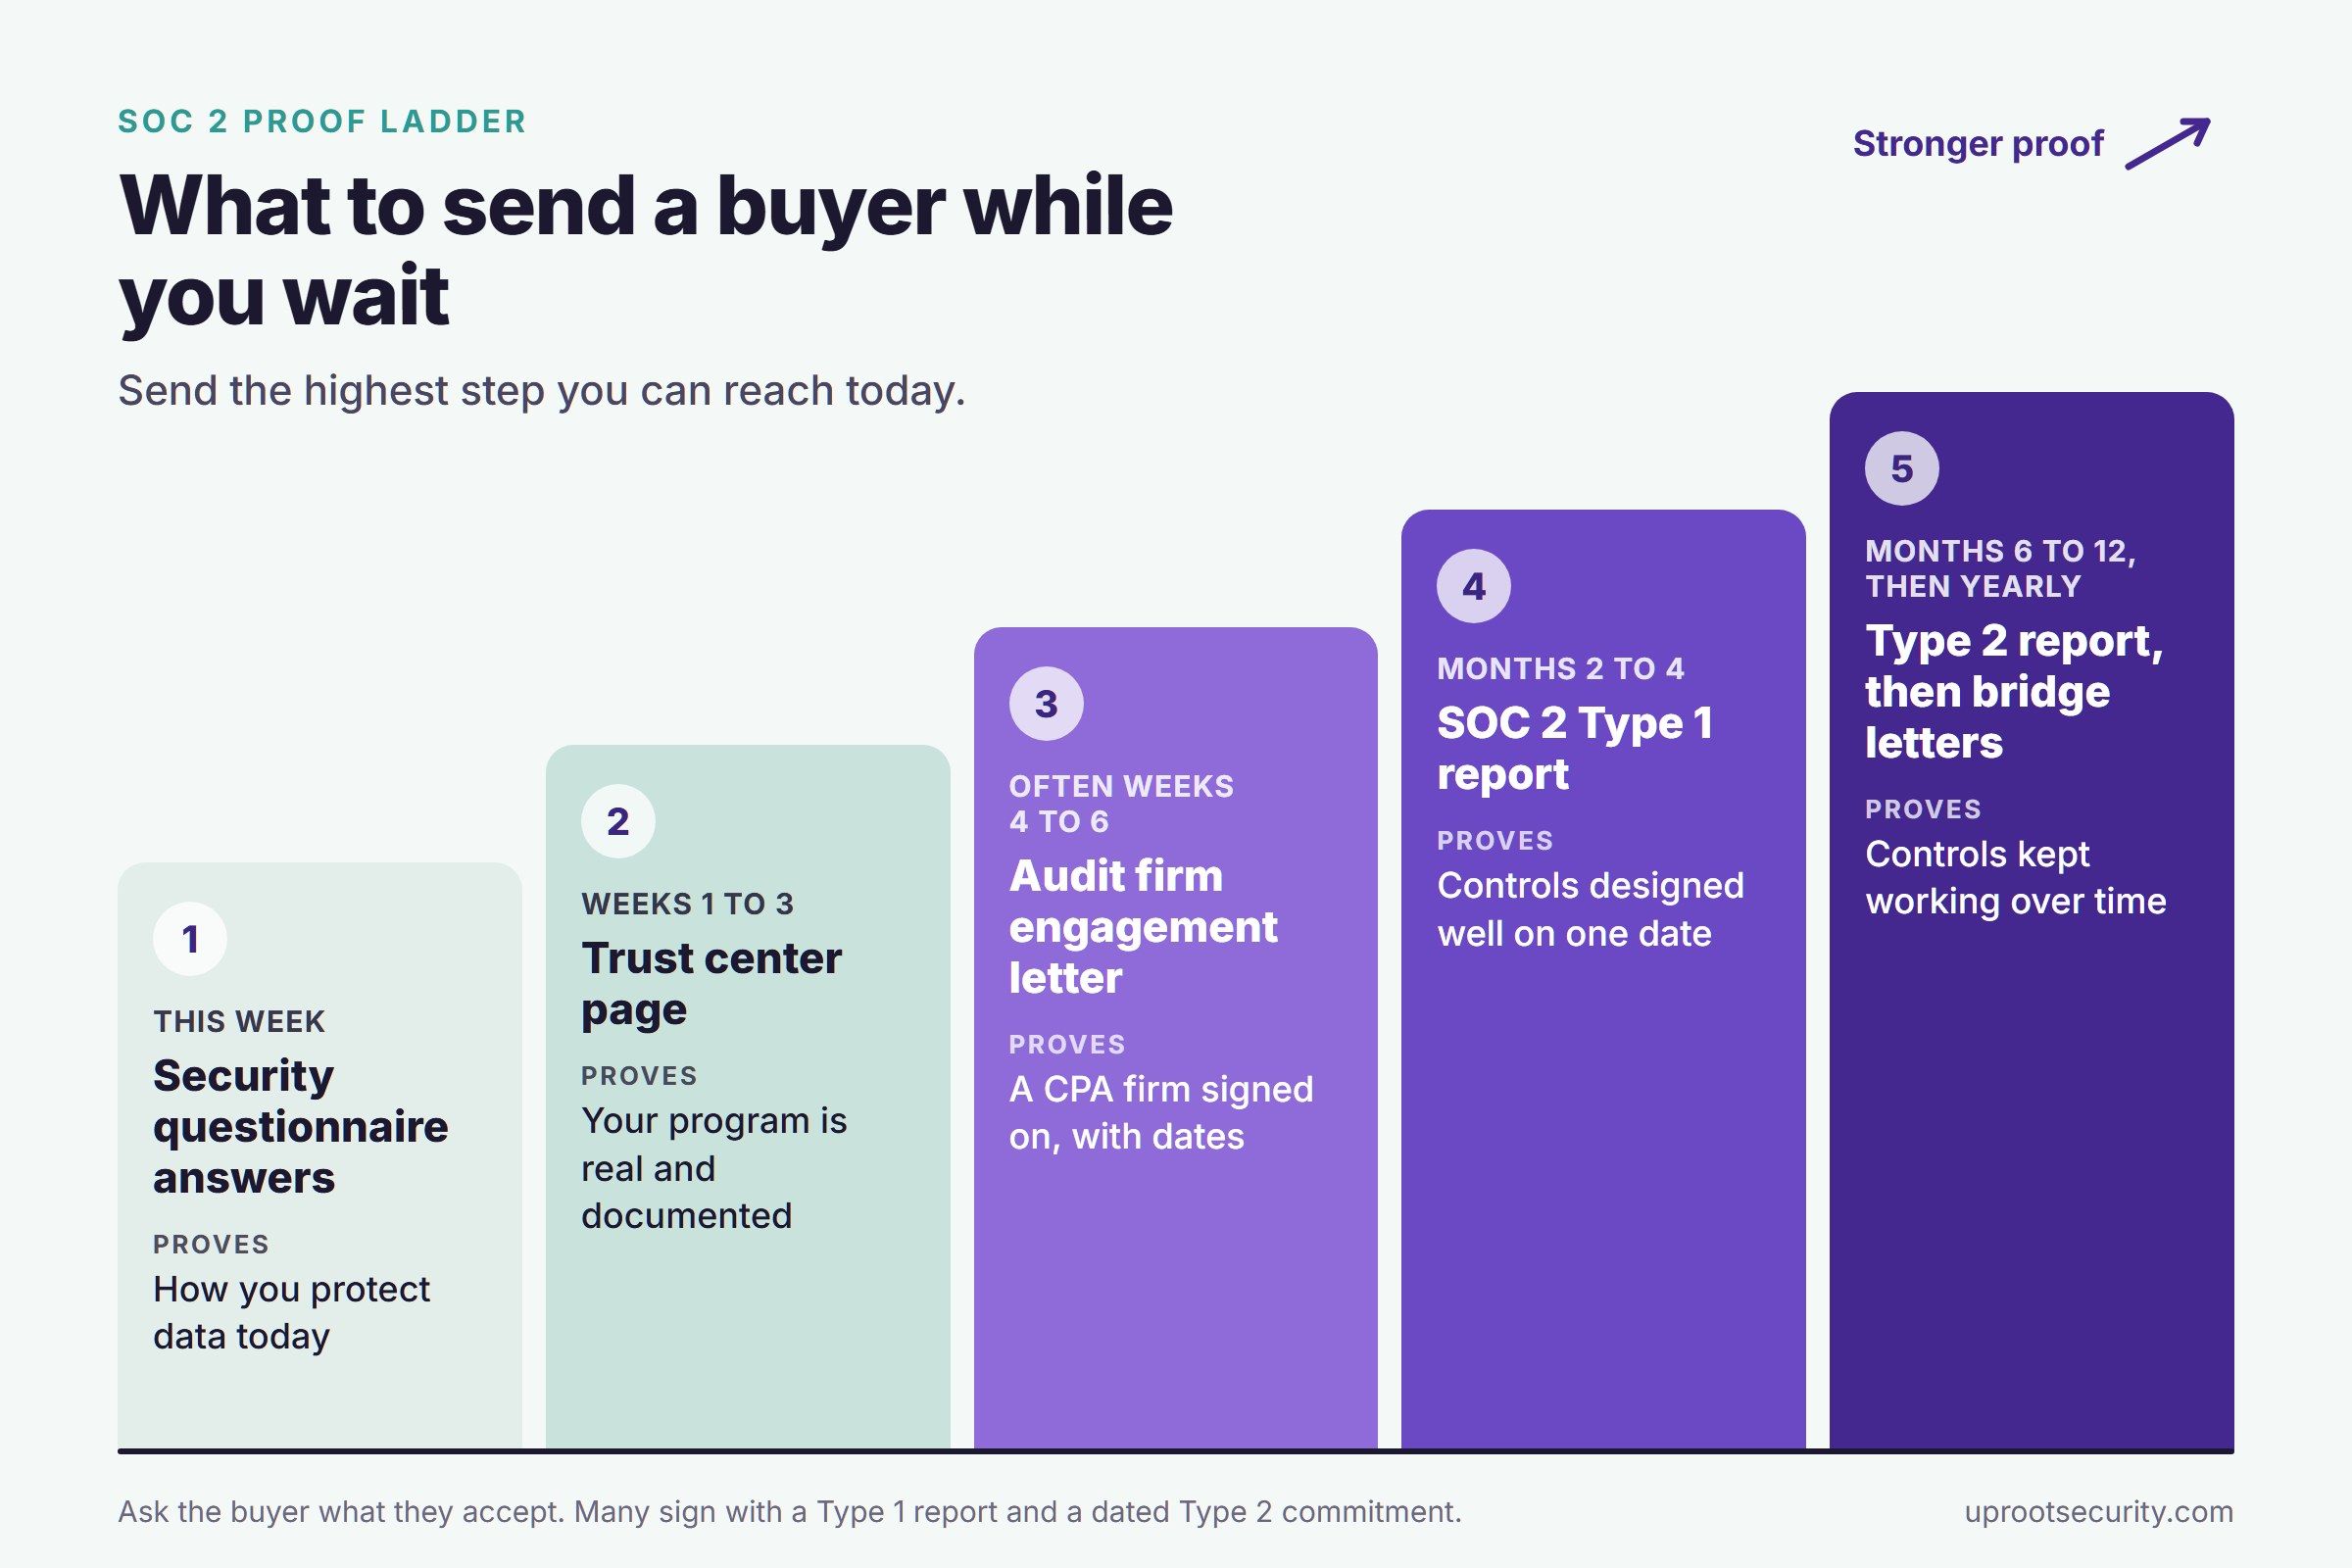
| Step | What you send | What it proves | When you can send it |
|---|---|---|---|
| 1 | A completed security questionnaire | How you handle access, data and incidents today | This week |
| 2 | A trust center page with policies and a list of controls | Your program is real and documented | Weeks 1 to 3 |
| 3 | A letter from your audit firm confirming the engagement and planned dates | An independent CPA firm has signed on, with a date | Once the auditor is booked, often weeks 4 to 6 |
| 4 | A SOC 2 Type 1 report | Your controls were designed well on one date | Months 2 to 4 |
| 5 | A SOC 2 Type 2 report, then bridge letters between reports | Your controls kept working over time | Months 6 to 12, then every year |
Our security questionnaire response guide covers step 1. Our trust center guide covers step 2. Once you have a report, a SOC 2 bridge letter covers the months between one report and the next.
Ask the buyer what they need. Many sign with a Type 1 report plus a clause committing you to a Type 2 by a set date.
Not sure what your buyer will accept? Talk to a compliance expert and get a plan for this week's reply.
Type 1 First or Straight to Type 2?
Go for a Type 1 first when a deal needs a report within 4 months. Go straight to Type 2 when the buyer will wait for it.
Let the contract's security clause decide, or ask the buyer's security team.
| What the buyer or contract says | Best path | Why |
|---|---|---|
| "We need a SOC 2 report before we sign" | Type 1 first | Fastest real report, 2 to 4 months |
| "Type 2 within 12 months of signing" | Type 1 now, Type 2 window starts right after | You close the deal and meet the clause |
| "Type 2 only, no Type 1" | Straight to Type 2 with a 3-month window | A Type 1 would not count for this buyer |
| No deadline, enterprise buyers next year | Straight to Type 2, 6 to 12 month window | A longer window carries more weight with large buyers |
Read more in our guides to the SOC 2 Type 1 report and the SOC 2 Type 2 report.
The Fastest Path: A Week-by-Week SOC 2 Plan
The fastest realistic path gets a Type 1 report in about 12 to 16 weeks and opens the Type 2 window right after. It assumes a small cloud team with one owner.
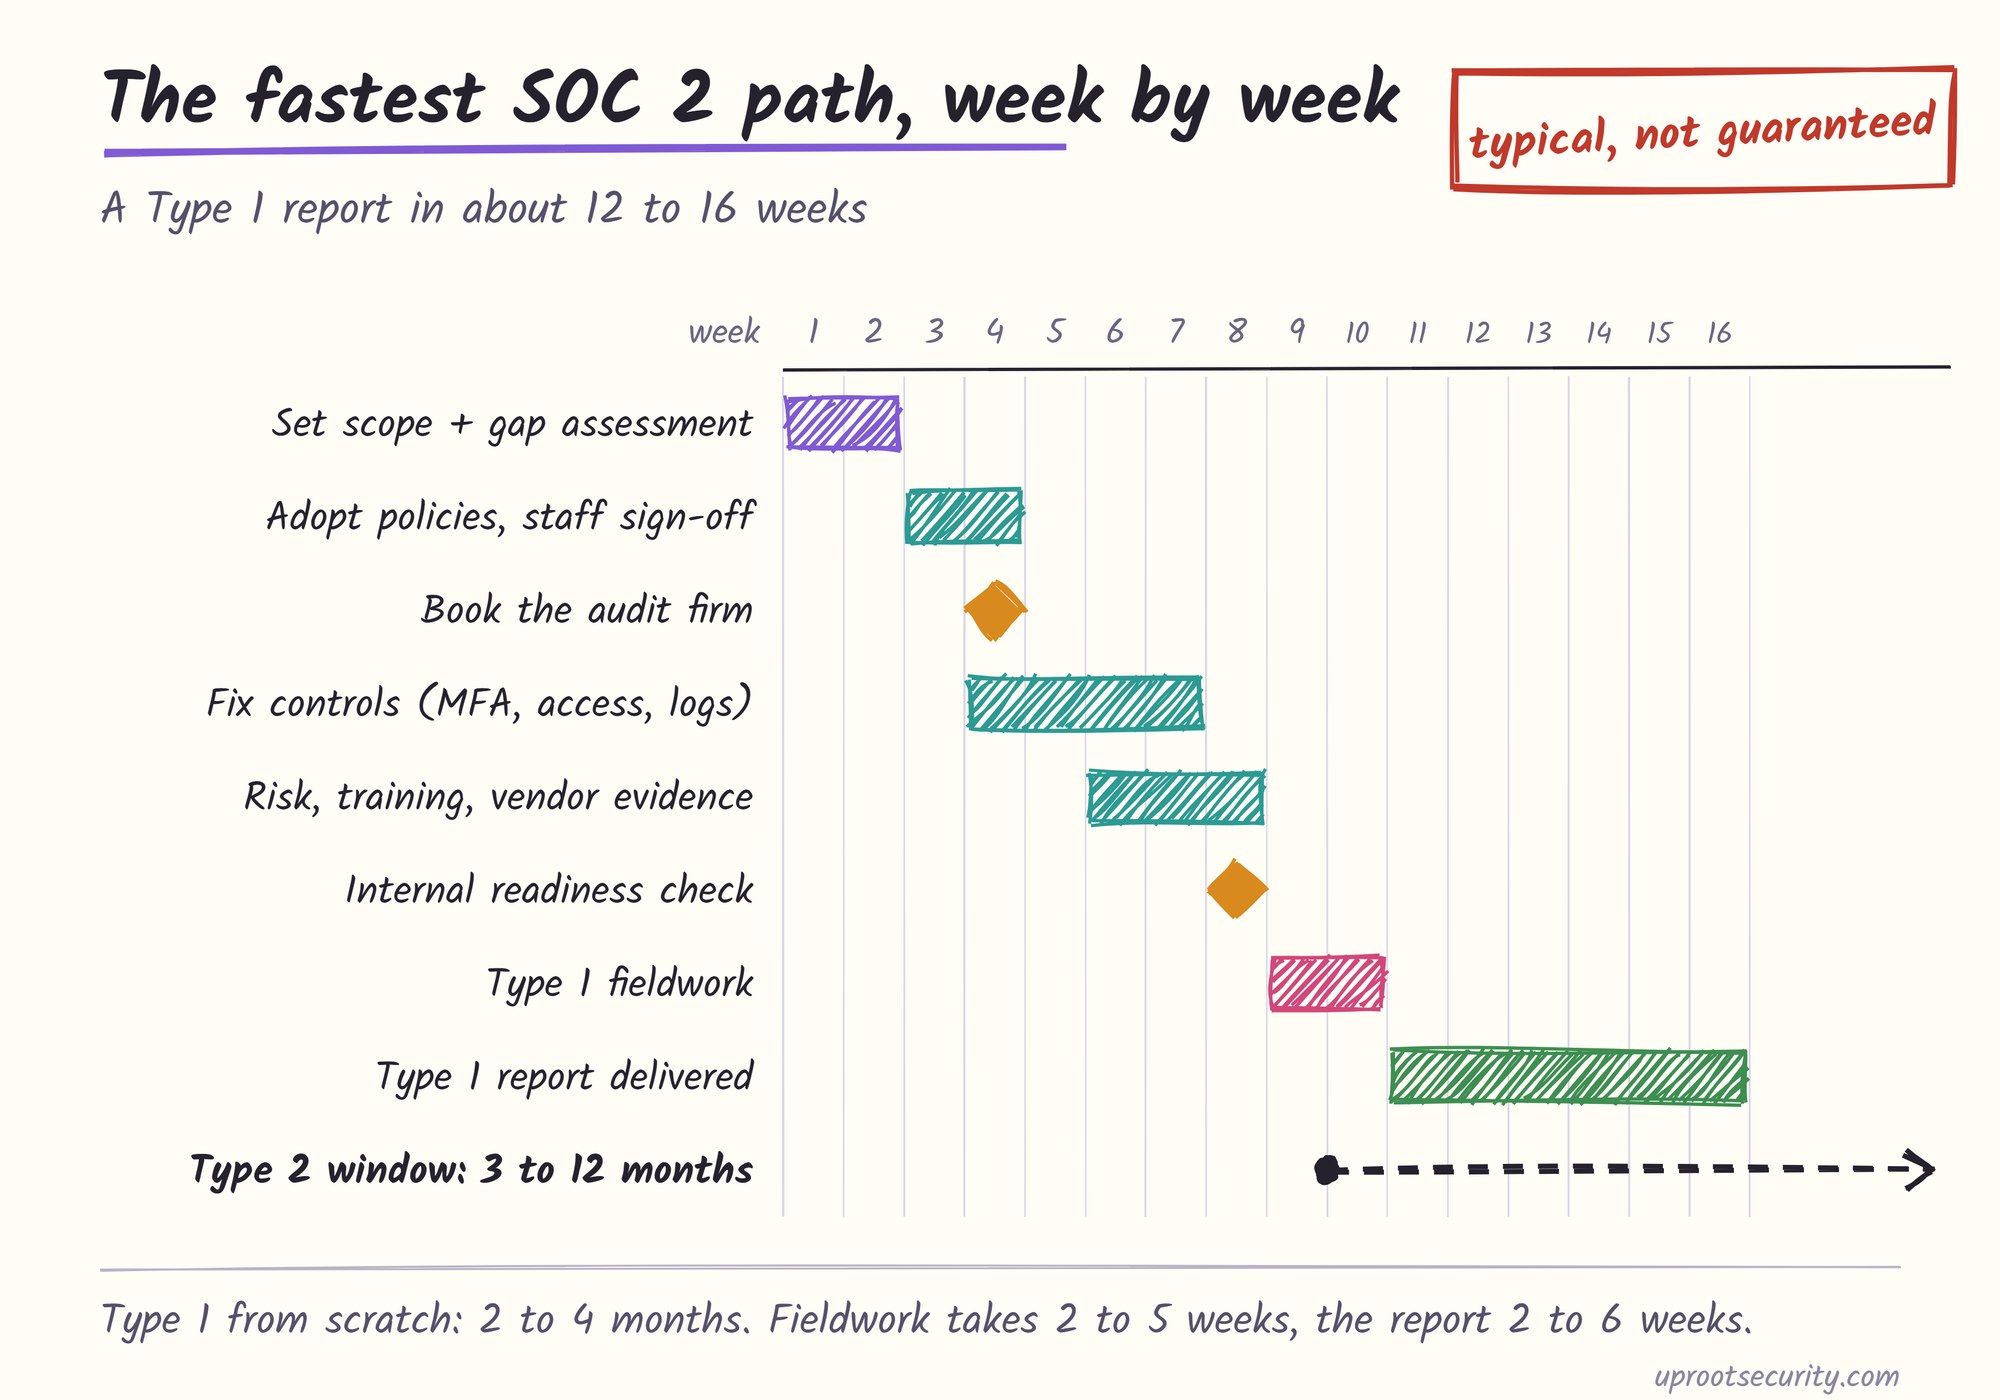
| Week | What happens | Done when |
|---|---|---|
| 1 | Set scope (systems, people, Trust Services Criteria). Name one owner. | Scope written down and agreed |
| 2 | Gap assessment. Connect cloud, code and HR tools for evidence. | Gap list with an owner per gap |
| 3 to 4 | Adopt policies (access, change management, incident response, vendors) and get staff sign-off. | Policies approved and acknowledged |
| 4 | Shortlist and book an audit firm. Agree Type 1 date and fee. | Engagement letter signed |
| 4 to 7 | Fix controls: MFA everywhere, access reviews, onboarding and offboarding, logging, backups. | Every gap closed or accepted as a risk |
| 6 to 8 | Risk assessment, security training, vendor reviews, background checks where required. | Evidence in place for each control |
| 8 | Internal readiness check of every control. | No open gaps |
| 9 to 10 | Type 1 fieldwork with the auditor. | Auditor questions answered |
| 10 onward | Type 2 observation window starts. Keep evidence flowing. | Controls running every week |
| 11 to 16 | Auditor writes and delivers the Type 1 report. | Type 1 report in the buyer's hands |
Your SOC 2 Type 2 timeline then runs from week 10. With a 3-month window, Type 2 fieldwork starts around month 6 and the report lands in month 7 to 9.
Shortlist firms with our guide to SOC 2 auditors for startups.
Can You Get SOC 2 in 2 Weeks?
A SOC 2 report in 2 weeks is not realistic from scratch, because fieldwork and report writing alone usually take 4 weeks or more.
Automation shortens readiness, never the observation window.
- Can compress: policy writing, evidence collection, gap fixes, auditor search, questionnaire answers.
- Cannot compress: the Type 2 observation window, the auditor's testing and the auditor's report review.
A promise of "SOC 2 in 2 weeks" usually means readiness in 2 weeks, with the report still weeks or months away. Useful, as long as your buyer hears the real date.
Does SOC 2 Take Longer for Teams Outside the US?
SOC 2 takes about the same time outside the US, as long as you book a licensed CPA firm early. Only a licensed CPA firm can issue a SOC 2 report under AICPA standards.
Three things catch non-US teams, such as a 60-person company in Berlin selling to US buyers:
- ISO 27001 does not replace SOC 2. Many US buyers still ask for SOC 2. Map shared controls to save work.
- Time zones. Fieldwork is mostly remote, but walkthrough calls need overlapping hours. Agree them early.
- Auditor capacity. Firms book up before year end. Book in month one.
How Long Is a SOC 2 Report Valid, and How Long Do Renewals Take?
A SOC 2 report has no formal expiry date, but most buyers expect one that covers the last 12 months.
Renewals are faster than the first report. The new window starts the day the old one ends, and the renewal report usually arrives 1 to 3 months after it closes. A bridge letter covers the months in between, so the SOC 2 Type 2 timeline never leaves buyers without cover.
How UprootSecurity Gets You to a SOC 2 Report Faster
UprootSecurity shortens the SOC 2 timeline by doing the readiness work with you, so the audit starts sooner. You get a dedicated compliance expert from day one, 140+ integrations that collect evidence automatically, and policies and controls ready to adapt.
While you prepare, our trust center and questionnaire automation (Growth and Enterprise plans) let you answer the buyer this week. We introduce you to audit firms that fit your size and budget. The audit fee is paid to the firm and typically runs $5,000 to $20,000. A yearly pentest is included. The same platform covers 22 frameworks, including ISO 27001 and HIPAA.
| What a waiting deal needs | How UprootSecurity delivers it |
|---|---|
| Answer the buyer now | Trust center and questionnaire automation (Growth and Enterprise plans) |
| Readiness in weeks, not months | A dedicated compliance expert plus ready-to-adapt policies and controls |
| Evidence that runs itself | 140+ integrations collecting evidence automatically |
| An auditor booked early | Introductions to audit firms that fit your size and budget |
| The report renewed on time | Controls monitored all year, with the expert tracking your next window |
Customer waiting on your SOC 2 report? → Book a demo today
Frequently Asked Questions
Getting SOC 2 compliant takes about 2 to 4 months for a Type 1 report and 6 to 12 months for a first Type 2. The biggest variable is the Type 2 observation window, which runs 3 to 12 months. Teams with MFA, access reviews and written policies already in place land at the short end.
A SOC 2 readiness assessment usually takes 1 to 3 weeks. It compares your current controls with the Trust Services Criteria and lists the gaps. Fixing those gaps is the longer part, often 4 to 10 weeks, depending on how many policies and controls you still need.
A real SOC 2 report in 2 weeks is not realistic for teams starting from scratch. Auditor fieldwork and report writing alone usually take 4 weeks or more. In 2 weeks you can finish a gap assessment, a trust center page and security questionnaires, which often keep a deal moving.
A SOC 2 report is generally treated as current for 12 months after its period ends. The report has no formal expiry date, but most buyers ask for a new one every year. If your next report is not ready yet, a bridge letter from your company covers the gap for a few months.
SOC 2 is not hard to get for a small cloud company, but it takes steady work over several months. The hard parts are policies people actually follow, evidence collected on time and controls that keep running through the observation window. A compliance platform and an expert remove most of the manual effort.
A SOC 2 audit fee typically runs $5,000 to $20,000, paid to the CPA firm that performs the audit. The price depends on report type, scope and company size, and Type 2 audits cost more than Type 1. Budget separately for a compliance platform, staff time and any tools you need to close control gaps.
The fastest way for a startup to get SOC 2 is a tightly scoped Type 1 report, with the auditor booked in month one. Use automation to collect evidence, adapt ready-made policies instead of writing them from scratch, and start the Type 2 observation window right after the Type 1 date.
Send a completed security questionnaire, your trust center link and an audit firm letter while your SOC 2 audit is in progress. The letter should confirm the engagement and planned dates. Add a written date for your report. Most reviewers accept this for a short time, especially when a Type 1 report is weeks away.